Trojan.ICLoader
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 6,946 |
| Threat Level: | 80 % (High) |
| Infected Computers: | 182,504 |
| First Seen: | January 12, 2015 |
| Last Seen: | October 3, 2026 |
| OS(es) Affected: | Windows |
The detection of Trojan.ICLoader on your system indicates a potential security threat that requires immediate attention. Trojans are a type of malware that can cause significant harm to your computer and compromise your personal data. In this report, we will provide you with an overview of the Trojan.ICLoader threat, its operating methods, symptoms of infection, and steps to remove it from your system.
Table of Contents
What Is Trojan.ICLoader?
Trojan.ICLoader is a type of Trojan horse malware that can infect your computer without your knowledge or consent. The name "Trojan" refers to the malicious program's ability to disguise itself as a legitimate application, allowing it to bypass security measures and gain access to your system. Trojan.ICLoader can be used to steal sensitive information, install additional malware, or provide unauthorized access to your computer.
How Trojan.ICLoader Operates
Trojan.ICLoader operates by exploiting vulnerabilities in your system or tricking you into installing it. Once installed, it can communicate with its command and control servers to receive instructions and transmit stolen data. The malware can also install additional components, such as keyloggers or ransomware, to further compromise your system. Trojan.ICLoader can be difficult to detect, as it may not exhibit obvious symptoms of infection, making it essential to use reputable security software to identify and remove the threat.
Symptoms of Infection
While Trojan.ICLoader may not always exhibit noticeable symptoms, some common signs of infection include slow system performance, unexpected pop-ups or advertisements, and unauthorized changes to your system settings. You may also notice that your browser is being redirected to suspicious websites or that your personal data is being stolen. If you suspect that your system is infected with Trojan.ICLoader, it is crucial to take immediate action to remove the malware and prevent further damage.
How to Remove Trojan.ICLoader
- Boot your computer in Safe Mode with Networking to prevent the malware from loading and to allow you to download and install removal tools.
- Use a reputable malware removal tool, such as SpyHunter, to perform a full scan of your system and identify all components of the Trojan.ICLoader malware.
- Uninstall any suspicious programs or applications that may be related to the malware infection.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any malicious extensions or add-ons.
- Reboot your computer and perform a follow-up scan to ensure that all components of the malware have been removed.
Conclusion
Removing Trojan.ICLoader from your system requires careful attention to detail and the use of reputable security software. By following the steps outlined in this report, you can help to ensure that your system is free from the malware and that your personal data is protected. Remember to always be cautious when downloading and installing software, and to use strong antivirus protection to prevent future infections. If you are unsure about any aspect of the removal process, consider seeking the assistance of a qualified security professional to ensure that your system is fully cleaned and secured.
SpyHunter Detects & Remove Trojan.ICLoader
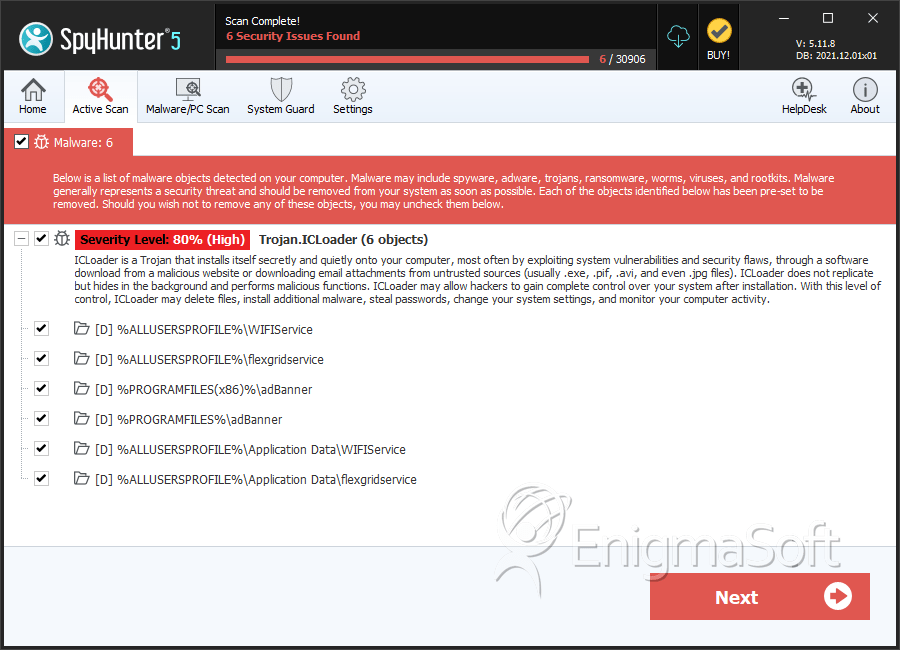
Directories
Trojan.ICLoader may create the following directory or directories:
| %ALLUSERSPROFILE%\Application Data\WIFIService |
| %ALLUSERSPROFILE%\Application Data\flexgridservice |
| %ALLUSERSPROFILE%\WIFIService |
| %ALLUSERSPROFILE%\flexgridservice |
| %PROGRAMFILES%\adBanner |
| %PROGRAMFILES(x86)%\adBanner |
Analysis Report
General information
| Family Name: | Trojan.ICLoader |
|---|---|
| Signature status: | Root Not Trusted |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
3af6e48ce973aedf0f6ac900e9af9759
SHA1:
65266a204d1bbe1a0b29ffc45dfed2060ef55222
SHA256:
C3288D2FFE1F80ACD995F58878A4216C76D4930506DDA47A59F756740C358637
File Size:
421.89 KB, 421888 bytes
|
|
MD5:
18c7f0b8f79b1ebfaec8e2590ea3a66d
SHA1:
4e066e50734fb6b03241cbd5731eb56bd96d5042
SHA256:
B612F9744E517B01A13FF1CEEC85174C46451033ED2748F44FDCB9C256E8B24A
File Size:
2.00 MB, 2001584 bytes
|
|
MD5:
ef67831a3bce429196a78e58308f256b
SHA1:
d5438eabb5bcd0d6686fd4deb5bc332f9a29b44e
SHA256:
26C75C7997C3D9C504A244C74C70DB445C4FDA2A455B6F2D5A0859F4CACE57C2
File Size:
3.67 MB, 3673272 bytes
|
|
MD5:
fc7d203a1fbf856f5dd7827622ed49f5
SHA1:
79f34bb504883ef39585d0e76c3f9c754dc35cb1
SHA256:
89D51989150F4EFF05A111BE2595ABB5396838ED514D65046FDFC6A583021166
File Size:
368.13 KB, 368128 bytes
|
|
MD5:
a1026d1dcd8eb19feabddfd8cc0e0d6c
SHA1:
b32b98153db5a2de8d622ca8556c66615cb4c226
SHA256:
A27D0DF924FA4E15EB2FC8C86069672CA93A9AAB304CCCA75B8626B4ED594988
File Size:
982.28 KB, 982280 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have resources
- File doesn't have security information
- File has been packed
- File has exports table
- File has TLS information
- File is 32-bit executable
Show More
- File is console application (IMAGE_SUBSYSTEM_WINDOWS_CUI)
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup. |
| Company Name | Nopani |
| File Description | Midak Setup |
| File Version | 2.8.5.8 |
| Legal Copyright | Internet Wizard |
| Product Name | Midak |
| Product Version | 5.7 |
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| LLC "YURYDYCHNA KOMPANIYA AYTI-LEKS" | COMODO RSA Certification Authority | Root Not Trusted |
| Torgovy Dom UKMB Ta Evropa, LLC | COMODO RSA Certification Authority | Root Not Trusted |
| FINANSINVEST, OOO | COMODO RSA Code Signing CA | Self Signed |
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\is-o15pe.tmp\b32b98153db5a2de8d622ca8556c66615cb4c226_0000982280.tmp | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Syscall Use |
Show More
|
| Process Manipulation Evasion |
|
| Process Shell Execute |
|
| Anti Debug |
|
| User Data Access |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\4e066e50734fb6b03241cbd5731eb56bd96d5042_0002001584.,LiQMAxHB
|
"C:\Users\Fkvlhjhy\AppData\Local\Temp\is-O15PE.tmp\b32b98153db5a2de8d622ca8556c66615cb4c226_0000982280.tmp" /SL5="$E026A,724874,56832,c:\users\user\downloads\b32b98153db5a2de8d622ca8556c66615cb4c226_0000982280"
|


