PUP.Navegaki
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 6,691 |
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 36,698 |
| First Seen: | August 27, 2015 |
| Last Seen: | September 29, 2026 |
| OS(es) Affected: | Windows |
The detection of PUP.Navegaki on your system indicates the presence of a potentially unwanted program (PUP) that may be causing issues with your computer's performance and security. It's essential to understand the nature of this threat and take immediate action to remove it and prevent further damage.
Table of Contents
What Is PUP.Navegaki?
PUP.Navegaki is a type of malware that is classified as a potentially unwanted program. This means that it is not necessarily a virus or a trojan, but rather a program that may be installed on your system without your knowledge or consent. PUPs can be bundled with other software or downloaded from the internet, and they often exhibit behaviors that are annoying or malicious.
How PUP.Navegaki Operates
PUP.Navegaki, like other PUPs, operates by installing itself on your system and then performing various actions that can compromise your security and privacy. It may collect your personal data, such as browsing history and search queries, and use it for advertising or other malicious purposes. It may also display unwanted ads, pop-ups, or banners, and even redirect your browser to suspicious websites.
In addition, PUP.Navegaki may also install other malicious programs or toolbars on your system, which can further compromise your security. It may also modify your system settings, such as changing your default search engine or homepage, without your consent.
Symptoms of Infection
If your system is infected with PUP.Navegaki, you may experience a range of symptoms, including slow system performance, unwanted ads and pop-ups, and suspicious browser behavior. You may also notice that your system is crashing or freezing frequently, or that your browser is being redirected to unknown websites.
Other symptoms of PUP.Navegaki infection include the appearance of suspicious toolbars or extensions on your browser, and the collection of your personal data without your consent. If you notice any of these symptoms, it's essential to take immediate action to remove the malware and prevent further damage.
How to Remove PUP.Navegaki
- Boot your system in Safe Mode with Networking to prevent the malware from loading and to allow you to download and install removal tools.
- Download and install a reputable anti-malware tool, such as SpyHunter, and perform a full scan of your system to detect and remove PUP.Navegaki and any other malicious programs.
- Uninstall any suspicious programs or applications that may be related to PUP.Navegaki, and remove any unwanted toolbars or extensions from your browser.
- Reset your browser settings to their default values, including Chrome, Firefox, and Edge, to remove any malicious changes made by the malware.
- Reboot your system and perform another scan with your anti-malware tool to ensure that PUP.Navegaki has been completely removed.
Conclusion
Removing PUP.Navegaki from your system requires careful attention to detail and a thorough understanding of the malware's behavior. By following the steps outlined above, you can effectively remove the malware and prevent further damage to your system. It's also essential to take preventive measures, such as installing anti-malware software and being cautious when downloading software or clicking on links, to avoid future infections.
Remember, PUPs like PUP.Navegaki can be tricky to remove, and it's essential to be patient and persistent in your efforts to eliminate the malware. If you're unsure about any aspect of the removal process, consider seeking the help of a professional or contacting a reputable anti-malware vendor for assistance.
Aliases
9 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| AVG | Generic6.KSM |
| Fortinet | Riskware/Navegaki |
| Panda | Trj/CI.A |
| McAfee-GW-Edition | Artemis |
| Comodo | ApplicUnwnt |
| Kaspersky | not-a-virus:AdWare.Win32.Amonetize.aafo |
| K7AntiVirus | Adware ( 004b48a71 ) |
| McAfee | Artemis!2F44459746DF |
| CAT-QuickHeal | AdWare.Amonetize.r5 (Not a Virus) |
SpyHunter Detects & Remove PUP.Navegaki
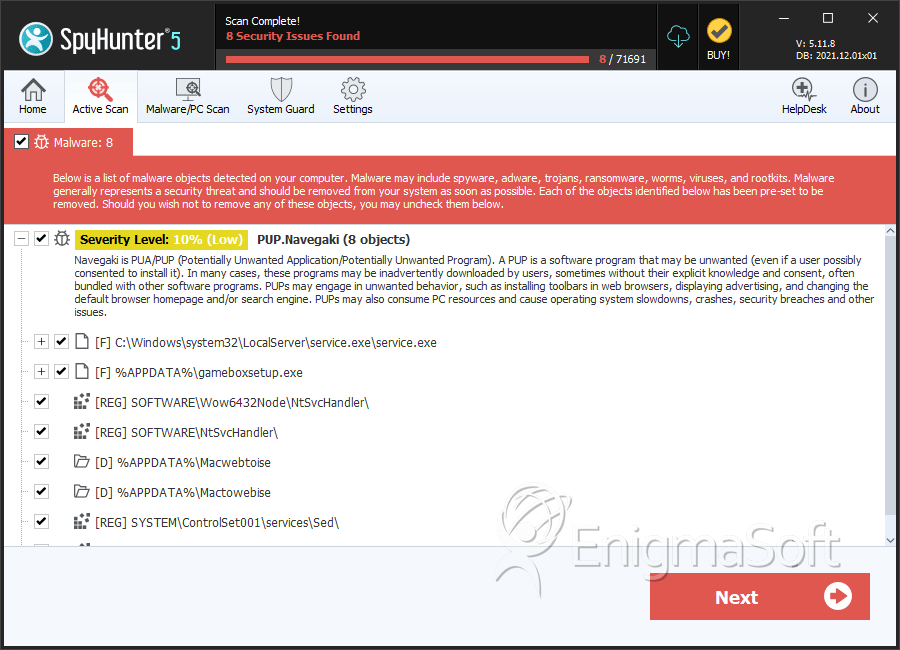
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | service.exe | a6ccd2e757c35b16a1a0dc5d9dc3fb84 | 3,927 |
| 2. | gameboxsetup.exe | 3d4259bfde5e834f4acc5889be8f7097 | 2,155 |
| 3. | ntsvc.exe | 1a5376165bbada36ef84928404b419e7 | 91 |
Registry Details
Directories
PUP.Navegaki may create the following directory or directories:
| %APPDATA%\Mactowebise |
| %APPDATA%\Macwebtoise |
| %APPDATA%\NetworkService |
| %PROGRAMFILES%\navegaki |
Analysis Report
General information
| Family Name: | PUP.Navegaki |
|---|---|
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
73faddc3d835fb5995f7471bcca23111
SHA1:
562fa6ff629d2c807ab39437fb6bf886b433c5ae
SHA256:
04970DDD7CEC7D8F64A33DBF75C084D2535341DFA646DDF4FA052197001BD8CE
File Size:
497.02 KB, 497016 bytes
|
|
MD5:
ea595631c5866fcecd86b90a93187042
SHA1:
dd8096e208fc5517fa4026d7d2c81b59030c623f
SHA256:
FDF951ABD38C3F51AD1E10C5561443D77A522482C690429820CE97D7C2A1CC21
File Size:
690.83 KB, 690832 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
Show More
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Company Name | Navigation |
| File Description |
|
| File Version |
|
| Internal Name |
|
| Legal Copyright |
|
| Original Filename | Navigation.exe |
| Product Name |
|
| Product Version |
|
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| OASIS GAMES LIMITED | Symantec Class 3 SHA256 Code Signing CA | Self Signed |
| Navigation network co.,limited | VeriSign Class 3 Code Signing 2010 CA | Self Signed |
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| \device\harddisk0\dr0 | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| \device\namedpipe\gmdasllogger | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsv633.tmp\findprocdll.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsv633.tmp\langdll.dll | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Network Winhttp |
|
| Network Winsock2 |
|
| Network Winsock |
|
| Process Manipulation Evasion |
|
| Anti Debug |
|
| User Data Access |
|


