Enigma Ransomware
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 100 % (High) |
| Infected Computers: | 3,349 |
| First Seen: | May 11, 2016 |
| Last Seen: | November 24, 2021 |
| OS(es) Affected: | Windows |
The Enigma Ransomware is a ransomware Trojan that is designed to attack computer users located in Russian-speaking countries. The Enigma Ransomware was first observed in late April of 2016. The Enigma Ransomware encrypts the victim's data using an AES encryption algorithm and then demands the payment of 0.4291 BitCoin, which is about $200 USD in exchange for the decryption key. This is a common approach linked to most ransomware Trojans. What makes the Enigma Ransomware unique is that its ransom note and attack are in Russian and seem to target specific countries where this language is spoken. The Enigma Ransomware also uses an installer based on HTML and JavaSCript, which contains a corrupted executable file that is embedded inside. Some versions of the Enigma Ransomware are unsuccessful in deleting Shadow Volume Copies of encrypted files, giving computer users the possibility of recording their files through that method.
Table of Contents
The Enigma that can be Solved with Money
The Enigma Ransomware may be distributed using a compromised JavaScript installer that contains an embedded executable file. The Enigma Ransomware may be distributed through HTML malicious attachments that launch the victim's Web browser so that it will execute this threatening JavaScript, which in turn delivers the corrupted executable code. The JavaScript will create a file with a Russian name: Свидетельство о регистрации частного предприятия.js, which translation means 'The certificate of registration of private predpriyatiya.js.' After creating this file, the HTML file will download it and claim that the victim should execute it. When executed, this JavaScript creates an executable file called 3b788cd6389faa6a3d14c17153f5ce86.exe, which is executed automatically. This executable file encrypts the files on the victim's computer, changing their extension to '.the Enigma' and delivers a ransom note to the victim. The ransom note instructs the victim on how to pay using TOR and informs the victims about what has happened to their files. The text of the Enigma Ransomware ransom note in the original Russian reads as follows:
Мы зашифровали важные файлы на вашем компьютере: документы, базы данных, фото, видео, ключи.
Файлы зашифрованны алгоритмом AES 128(https://ru.wikipedia.org/wiki/Advanced_Encryption_Standard) с приватным ключем,который знаем только мы.
Зашифрованные файлы имеют расширение .the Enigma . Расшифровать файлы без приватного ключа НЕВОЗМОЖНО.
Если хотите получить файлы обратно:
1)Установите Tor Browser https://www.torproject.org/
2)Найдите на рабочем столе ключ для доступа на сайт the Enigma_(номер вашего ключа).RSA
3)Перейдите на сайт http://f6lohswy737xq34e.onion в тор-браузере и авторизуйтесь с помощью the Enigma_(номер вашего ключа).RSA
4)Следуйте инструкциям на сайте и скачайте дешифратор
Если основной сайт будет недоступен попробуйте http://ohj63tmbsod42v3d.onion/
Which can be translated as:
We encrypt sensitive files on your computer: documents, databases, photos, videos and keys.
Files encryption algorithm AES 128 (https://ru.wikipedia.org/wiki/Advanced_Encryption_Standard) with a private key that only we know.
Encrypted files have .the Enigma extension. It decrypts files without the private key IMPOSSIBLE.
If you want to get the files back:
1) Install the Tor Browser https://www.torproject.org/
2) Locate the desktop key to access the site the Enigma_ (your room key) .RSA
3) Go to the website http: //f6lohswy737xq34e.onion into a torus-browser and log in using the Enigma_ (your room key) .RSA
4) Follow the instructions on the website and download the decoder
If the primary site is unavailable, try http: //ohj63tmbsod42v3d.onion/
Paying the Enigma Ransomware Ransom
Computer users are advised against paying the Enigma Ransomware ransom. The best method for preventing and dealing with the Enigma Ransomware attacks is to backup all files on an external drive. This way, these files can be recovered from the backup after they have been encrypted. When computer users connect to the Enigma Ransomware payment site, they will be presented with the amount of BitCoins that must be paid as a ransom, as well as the additional payment information. Victims will be allowed to decrypt one file for free as proof that the con artists do hold the decryption key. The payment site also includes a chat box where threat developers can communicate directly with the victim.
SpyHunter Detects & Remove Enigma Ransomware
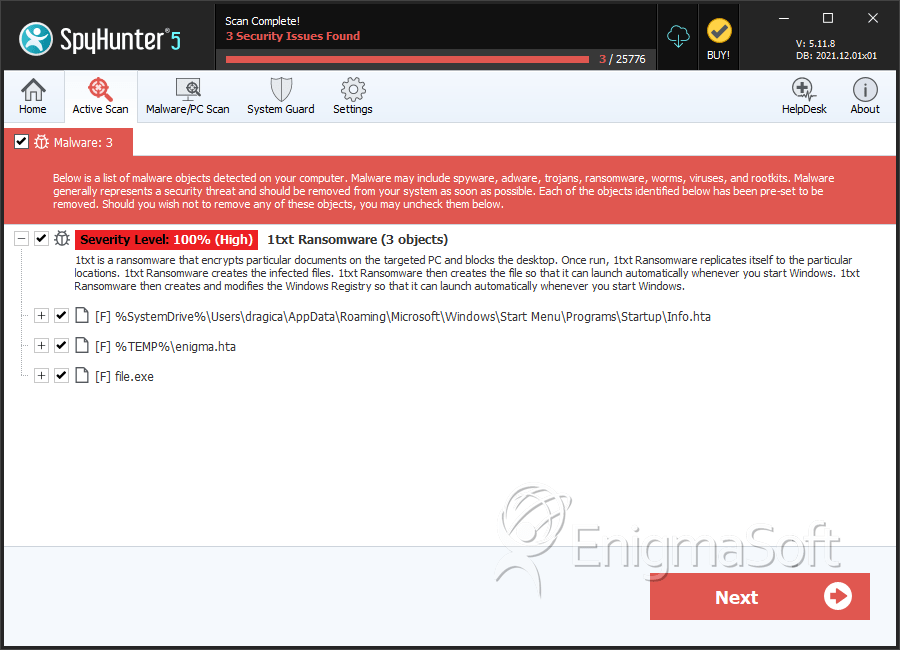
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | enigma.hta | 49834055020adf056f86bd6b786bc698 | 19 |
| 2. | Info.hta | 9a8f9782336bd1a4c1877c190badee78 | 8 |
| 3. | file.exe | c458e0d8d4818d0890ce0e34f6dc32aa | 0 |


