Adware.Hotbar
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 16,814 |
| Threat Level: | 20 % (Normal) |
| Infected Computers: | 2,268 |
| First Seen: | July 24, 2009 |
| Last Seen: | October 19, 2026 |
| OS(es) Affected: | Windows |
Adware.Hotbar (also known as W32.Adware.Hotbar) is a simple form of adware, that uses graphical skins added onto Internet Explorer, Microsoft Outlook and Outlook Express toolbars to get the user to trust it. Adware.Hotbar targets specific advertising to specific users depending on search terms typed into the fake toolbar.
Adware.Hotbar appears to be a legitimate toolbar for web browser applications. Several of the Hotbar buttons redirect users to pages that advertise products or services. Many times these pages are designed to obtain personal data from the user in addition to enticing clicks onto contextual adverts.
Adware.Hotbar is known to bombard computer users with annoying messages basically interrupting internet surfing. Adware.Hotbar may also gather personal information from the websites that a computer user visits. If left on a PC, Adware.Hotbar may be updated through the internet causing other malware to be installed without the knowledge of the computer user. When booting Windows on an infected PC, Adware.Hotbar will load into memory making it difficult to manually remove.
It may be necessary to utilize an updated spyware removal tool to automatically and completely remove Adware.Hotbar. Simply reinstalling a web browser or even Windows may not resolve the issue.
Table of Contents
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Fortinet | W32/SPNR.0BCP13!tr |
| AntiVir | Adware/Hotbar.A.1221 |
| McAfee | Artemis!A92F3018CC2C |
| AntiVir | Adware/Agent.274944.3 |
| AntiVir | Adware/Hotbar.A.25 |
| BitDefender | Gen:Adware.Heur.Um1@RCcgnZk |
| Symantec | Adware.ADH |
| McAfee | Artemis!D992252ABECC |
| AhnLab-V3 | Win-Adware/ToolBar.HotBar.472368.C |
| AntiVir | ADSPY/Hotbar.427368 |
| BitDefender | Application.Generic.286616 |
| McAfee | Artemis!7125C71F4984 |
| AVG | Generic4.ALIR |
| AhnLab-V3 | Win-Adware/ToolBar.Hotbar.472368 |
| AntiVir | ADSPY/Hotbar.CY.2 |
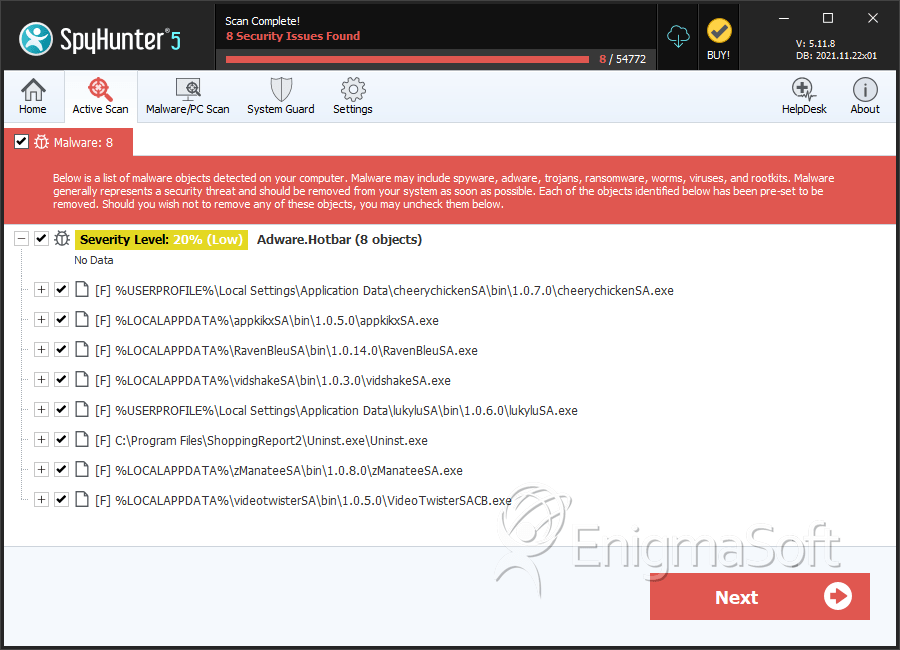
SpyHunter Detects & Remove Adware.Hotbar
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | FREEzeFrogSA.exe | 244005eb6e54efe3833f38d25c5be2e5 | 59 |
| 2. | vidshakeSA.exe | 68195663c8c175e0d8000ad0beebf581 | 54 |
| 3. | zManateeSA.exe | e302e22f2207e4c6aeb1c15a86001732 | 24 |
| 4. | VooMuuSA.exe | 8aada0afb11dab5cc771ecd8dea62d6b | 24 |
| 5. | VideoTwisterSACB.exe | 24305f098ddc36a74bbe3f2f78b179a3 | 21 |
| 6. | blueturtlegamesSA.exe | 12dd61cfc30222cfd2a184888a7ac2eb | 18 |
| 7. | snappydeeSA.exe | 01fdafb26eebc4b5a87459f160f6c507 | 17 |
| 8. | RavenBleuSA.exe | a92f3018cc2cacd28e0fc2a242d6b2c6 | 13 |
| 9. | cheerychickenSA.exe | c0aaba23a297ec9b69a4e97429df9c48 | 9 |
| 10. | appkikxSA.exe | 2d5b1b6b1700fcbaa54ec2a832db0a46 | 8 |
| 11. | ZeeDipSA.exe | 1a61860cc93e32fe35c1d2576c7a6f65 | 7 |
| 12. | SeekmoSA.exe | c63289dca87eff0be0edf537fc2163cc | 6 |
| 13. | GamesLeapSACB.exe | 84e2e1e838a9241a38f0281a677e87c0 | 6 |
| 14. | KangoBoxSA.exe | 51429f3c8630d11a405bcf34696e2294 | 5 |
| 15. | ClickPotatoLiteSA.exe | 677fe7fe101460a2acf62ceb400245ed | 3 |
| 16. | BlueTurtleGamesSACB.exe | 22f2a3ef9f8083e0b697aae6fb73ca61 | 2 |
| 17. | MossySkySA.exe | 674df9308a749b68fb403334816e4e3d | 2 |
| 18. | lukyluSA.exe | d42881537b6dc0b706fb0bbe112cb745 | 2 |
| 19. | LhootSA.exe | 63aa4c4388a3d3b979f6214435a82f9b | 2 |
| 20. | CheeryChickenSACB.exe | fdc8f05190b57abedc02990ef1d7e4f0 | 2 |
| 21. | HBLiteSA.exe | d992252abecc6df326aefb2d69ae7375 | 2 |
| 22. | _te1AD.exe | a9cb620e4374c4e19b629ccb3d9c0432 | 1 |
| 23. | seeqdoSA.exe | 3de5cfdb1f3d3becf987bbfe04dc5089 | 1 |
| 24. | VidShakeSACB.exe | c66ed83993d3c94921d805a252a19c16 | 1 |
| 25. | Weather.exe | 646e21f22e9c2c7eb0f8c60b4dc845ef | 1 |
| 26. | Srv.exe | 7125c71f4984f8563c3fd3bc6b78bfdd | 1 |
Analysis Report
General information
| Family Name: | Adware.Hotbar |
|---|---|
| Packers: | UPX |
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
27121cde4a66a393196a4cec3dc32938
SHA1:
4ee1c74ad1bd1b259c8a1d297dbe32280b8c7b72
SHA256:
1542EC25BA9CFA80EC060E2B029FA34826C4E829043F5682D1916EB85543A0AD
File Size:
172.68 KB, 172680 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has been packed
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| LI Impact | VeriSign Class 3 Code Signing 2010 CA | Self Signed |
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 521 |
|---|---|
| Potentially Malicious Blocks: | 60 |
| Whitelisted Blocks: | 461 |
| Unknown Blocks: | 0 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\microsoft\windows\usrclass.dat{dba6b5ef-640a-11ed-9bcb-f677369d361c}.txr.1.regtrans-ms | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\microsoft\windows\usrclass.dat{dba6b5ef-640a-11ed-9bcb-f677369d361c}.txr.2.regtrans-ms | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\.tm3a90.tmp | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Anti Debug |
|
| User Data Access |
|
| Network Urlomon |
|