PUP.Funshion
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 5,063 |
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 73,694 |
| First Seen: | September 18, 2014 |
| Last Seen: | October 1, 2026 |
| OS(es) Affected: | Windows |
The detection of PUP.Funshion on your system indicates the presence of a potentially unwanted program (PUP) that may be causing issues with your computer's performance and security. It is essential to understand the nature of this threat and take appropriate steps to remove it and prevent future infections.
Table of Contents
What Is PUP.Funshion?
PUP.Funshion is a type of malware that is classified as a potentially unwanted program. This category of threats includes software that may not be malicious in the classical sense but can still cause problems for users. PUPs often install themselves on a system without the user's full knowledge or consent, and they may exhibit behaviors such as displaying unwanted advertisements, collecting user data, or modifying system settings.
How PUP.Funshion Operates
Like other PUPs, PUP.Funshion likely operates by installing itself on a system through various means, such as bundled software installations, deceptive downloads, or exploits. Once installed, it may start displaying unwanted content, such as pop-ups, banners, or redirects to suspicious websites. It may also collect user data, including browsing history, search queries, or other sensitive information, which can be used for targeted advertising or other malicious purposes.
Symptoms of Infection
Systems infected with PUP.Funshion may exhibit a range of symptoms, including slow system performance, frequent crashes, or freezes. Users may also notice an increase in unwanted advertisements, suspicious search results, or unfamiliar programs installed on their system. Additionally, some users may experience issues with their browser settings, such as changed home pages, default search engines, or the presence of unwanted toolbars or extensions.
- Unwanted advertisements or pop-ups
- Suspicious search results or redirects
- System crashes or freezes
- Slow system performance
- Unfamiliar programs or toolbars installed
How to Remove PUP.Funshion
To remove PUP.Funshion from your system, follow these steps:
- Boot your system in Safe Mode with Networking to prevent the malware from interfering with the removal process.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system and detect any malicious components.
- Uninstall any suspicious programs or applications that may be related to the PUP.
- Reset your browser settings to their default values, including Chrome, Firefox, and Edge, to remove any unwanted extensions or add-ons.
- Reboot your system and perform another scan with your anti-malware tool to ensure that all malicious components have been removed.
Conclusion
Removing PUP.Funshion from your system requires a combination of technical knowledge and the right tools. By following the steps outlined above and using reputable anti-malware software, you can effectively remove this potentially unwanted program and prevent future infections. It is essential to remain vigilant and take proactive measures to protect your system and personal data from malware threats. Regularly updating your software, avoiding suspicious downloads, and using robust security tools can help you stay safe online and prevent the installation of unwanted programs like PUP.Funshion.
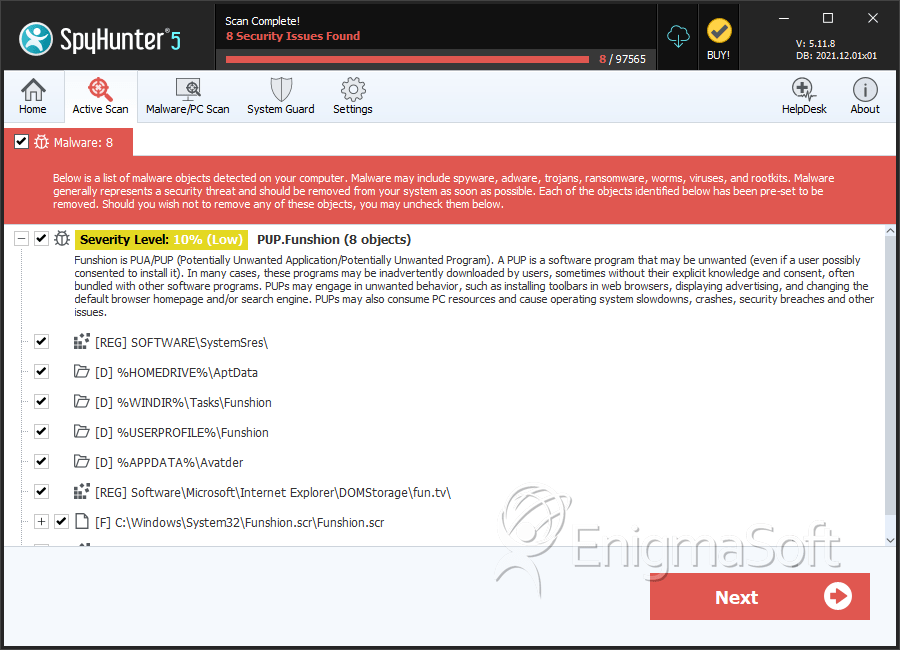
SpyHunter Detects & Remove PUP.Funshion
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | Funshion.scr | 03b881a55e1400de892d59e664f06620 | 3,489 |
| 2. | FunPierides_c7137_s.exe | bfaccfabb42ba9bb0d100ede917cd250 | 3 |
Registry Details
Directories
PUP.Funshion may create the following directory or directories:
| %ALLUSERSPROFILE%\Application Data\Funshion |
| %ALLUSERSPROFILE%\Funshion |
| %ALLUSERSPROFILE%\Microsoft\Windows\Start Menu\Programs\Funshion |
| %APPDATA%\Avatder |
| %APPDATA%\FunTemp |
| %APPDATA%\Funshion |
| %APPDATA%\FunshionV |
| %HOMEDRIVE%\AptData |
| %HOMEDRIVE%\FunshionMedia |
| %PROGRAMFILES%\Funshion Online |
| %PROGRAMFILES%\FunshionV |
| %PROGRAMFILES(x86)%\Funshion Online |
| %PROGRAMFILES(x86)%\FunshionV |
| %PUBLIC%\FunAcce |
| %PUBLIC%\Fundata |
| %USERPROFILE%\Documents\Funshion HD Media |
| %USERPROFILE%\Funshion |
| %WINDIR%\System32\Tasks\Funshion |
| %WINDIR%\Tasks\Funshion |
| %appdata%\Acceclient |
| %appdata%\Arefresh |
| %appdata%\FunUninst |
| %appdata%\funspeed |
| %temp%\funshiontmp |
Analysis Report
General information
| Family Name: | PUP.Funshion |
|---|---|
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
f21350e00e605b7b6ddce435475e57d5
SHA1:
b8194508b27734b63cfee4f5da37c63f91fdd4fd
SHA256:
2D0972E743683D2394B6086A009D03BE25B3022B2EFE1E565B4CEE0D99EA79DA
File Size:
238.03 KB, 238032 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
Show More
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Beijing Funshion Online Technologies Ltd. | Thawte Code Signing CA - G2 | Self Signed |
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\nsi3882.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete |


