Backdoor.Orcus
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 12,188 |
| Threat Level: | 60 % (Medium) |
| Infected Computers: | 4,096 |
| First Seen: | July 6, 2016 |
| Last Seen: | October 17, 2026 |
| OS(es) Affected: | Windows |
Backdoor.MoSucker (also known as Backdoor.Orcus) is a generic Trojan that threat actors deploy to users via exploit kits and spam emails. The Backdoor.MoSucker Trojan features the same capabilities you can find in remote access tools like TeamViewer and LogMeIn with added functionality. The Backdoor.MoSucker program can be used by threat actors to kill, run and modify processes on the infected system. Backdoor.MoSucker can move, rename and delete files on the local disk. The Trojan can log the user's activity and change the desktop background image. Also, the malware can be instructed to show message boxes, change data & time properties, restart the PC and modify the Windows Registry.
The Backdoor.MoSucker Trojan is configured to maintain a constant connection to its 'Command and Control' servers as long as the infected machine is turned on. Compromised users may notice strange movements of their mouse cursor and keyboard input that is not consistent with their commands. Backdoor.MoSucker can restrict the user's ability to issue commands to the compromised system and transform the device into a proxy for a remote user's advantage. Infected machines may be used to hide the network traffic of threat actors and even execute DDoS (Distributed Denial of Service) attacks. It is advised to remove the Backdoor.MoSucker Trojan in offline mode using a trusted anti-malware scanner.
Detection names for Backdoor.MoSucker by AVs:
BKDR_MOSUCK.A
BackDoor.Mosu
Backdoor.Generic.180860
Backdoor.Win32.MoSucker.dd!IK
Backdoor.Win32.Mocbot.bn
Heuristic.LooksLike.Win32.Spypro.B
Packer.Morphine.Gen (v)
TR/Crypt.Morphine.Gen
TrojWare.Win32.PkdMorphine.~AN
W32/Troj_Obfusc.Z.gen!Eldorado
Win-Trojan/Mosucker.75506
Win32:MoSucker-N [Trj]
Table of Contents
SpyHunter Detects & Remove Backdoor.Orcus
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | file.exe | 956098914ea294ef80ed87da2dae7eda | 0 |
Registry Details
Directories
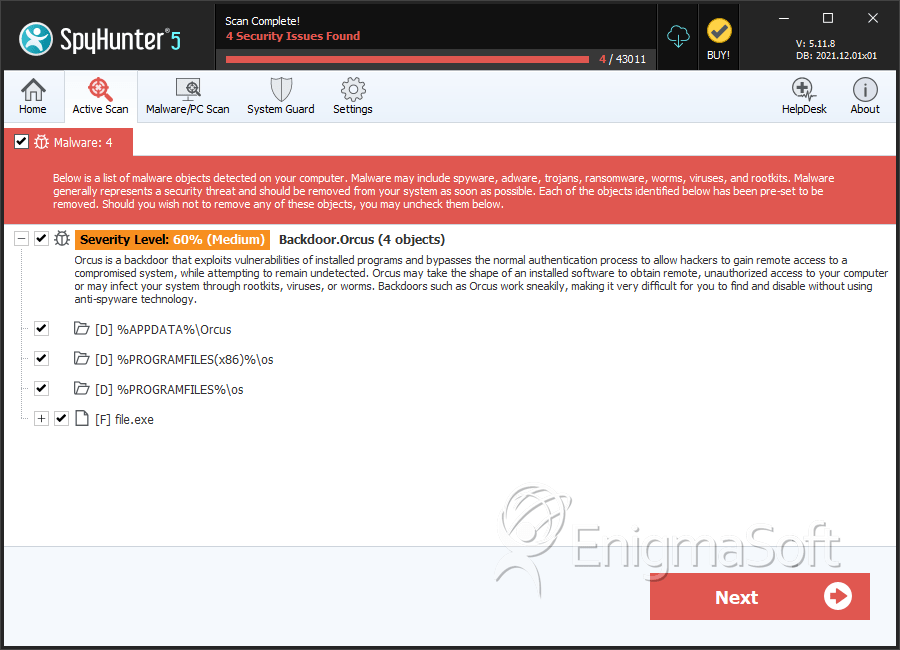
Backdoor.Orcus may create the following directory or directories:
| %APPDATA%\Orcus |
| %PROGRAMFILES%\os |
| %PROGRAMFILES(x86)%\os |
Analysis Report
General information
| Family Name: | Backdoor.Orcus |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
82bb7f2ddf5178516c0024593f35d023
SHA1:
144e815d6ab2f26d085b2ec99c2ddeebc844ba0f
SHA256:
CB485BF43A0C082E3172D8F6DEEBA2777D602BEC91970D379E587D1C4C85EFB4
File Size:
2.62 MB, 2619904 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have exports table
- File doesn't have security information
- File is .NET application
- File is 32-bit executable
- File is console application (IMAGE_SUBSYSTEM_WINDOWS_CUI)
- File is either console or GUI application
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Assembly Version | 1.0.0.0 |
| Company Name | CandideServer |
| File Description | CandideServer |
| File Version | 1.0.0.0 |
| Internal Name | CandideServer.dll |
| Original Filename | CandideServer.dll |
| Product Name | CandideServer |
| Product Version | 1.0.0 |
File Traits
- .NET
- dll
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 6,145 |
|---|---|
| Potentially Malicious Blocks: | 36 |
| Whitelisted Blocks: | 1,433 |
| Unknown Blocks: | 4,676 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Syscall Use |
Show More
|