Trojan.Snoozer
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 80 % (High) |
| Infected Computers: | 84,185 |
| First Seen: | March 24, 2016 |
| Last Seen: | May 24, 2026 |
| OS(es) Affected: | Windows |
The detection of Trojan.Snoozer on your system indicates a potential security threat that requires immediate attention. Trojans are a type of malware that can cause significant harm to your computer and compromise your personal data. It is essential to understand the nature of this threat and take prompt action to remove it and prevent future infections.
Table of Contents
What Is Trojan.Snoozer?
Trojan.Snoozer is a type of Trojan horse malware that can infiltrate your system without your knowledge or consent. Trojans are often disguised as legitimate software or attachments, making them difficult to detect. Once installed, they can create backdoors for remote access, allowing hackers to steal sensitive information, install additional malware, or use your system for malicious activities.
How Trojan.Snoozer Operates
Trojan.Snoozer, like other Trojans, operates by exploiting vulnerabilities in your system or using social engineering tactics to trick you into installing it. Once inside, it can communicate with its command and control servers to receive instructions and transmit stolen data. It may also attempt to disable security software, create fake system files, or modify registry settings to maintain its presence on your system.
Symptoms of Infection
Identifying a Trojan infection can be challenging, as it may not always exhibit obvious symptoms. However, you may notice unusual system behavior, such as slow performance, frequent crashes, or unfamiliar programs running in the background. You may also receive unexpected pop-ups, experience data loss, or find unfamiliar files and folders on your system. If you suspect that your system is infected with Trojan.Snoozer, it is crucial to take immediate action to remove it.
How to Remove Trojan.Snoozer
- Boot your system in Safe Mode with Networking to prevent the malware from loading and to allow for a more effective removal process.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system and detect any malware, including Trojan.Snoozer.
- Uninstall any suspicious programs or applications that you do not recognize or that were installed without your consent.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any malicious extensions or add-ons.
- Reboot your system and perform another full scan with your anti-malware tool to ensure that all malware has been removed.
Conclusion
Removing Trojan.Snoozer from your system requires a combination of technical expertise and caution. By following the steps outlined above and maintaining good security practices, such as keeping your operating system and software up-to-date, using strong passwords, and avoiding suspicious attachments and links, you can minimize the risk of future infections. Remember to always use reputable anti-malware tools and to regularly scan your system for any signs of malware to ensure your system remains secure and protected.
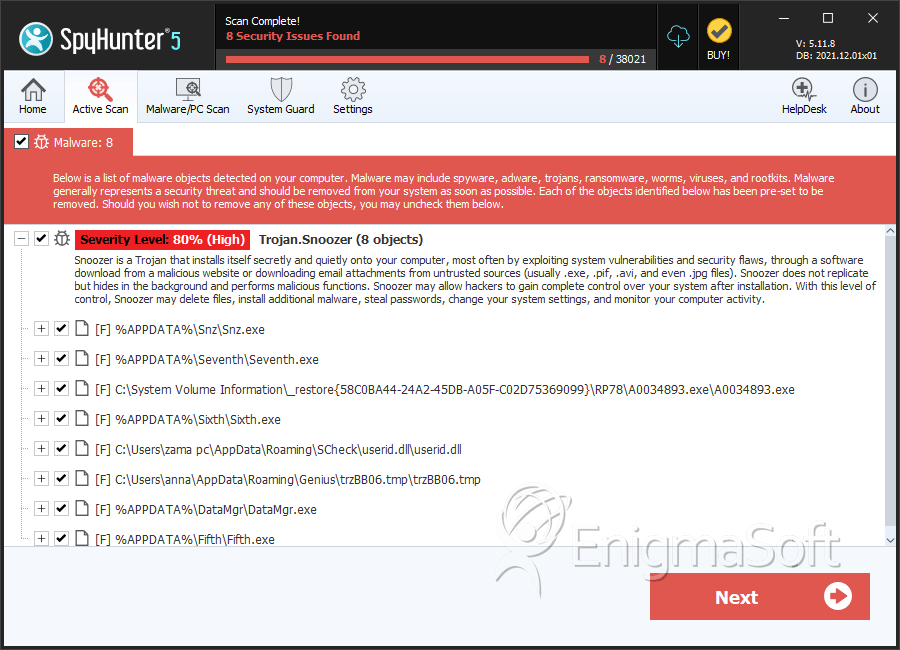
SpyHunter Detects & Remove Trojan.Snoozer
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | Sixth.exe | d2f6958ca8412960b7824da111e7c1ed | 2,594 |
| 2. | Snz.exe | 3f5c7472188a9a5f09e482365b3a5c41 | 245 |
| 3. | userid.dll | 067e9ac67923a2cad1d67b2cefa0254e | 187 |
| 4. | A0034893.exe | 4a00a689d1b572505d5bb2eed97e6ea7 | 151 |
| 5. | Fifth.exe | a0456346290d7cf65d029eaf7d960975 | 69 |
| 6. | Seventh.exe | 8b9b1fc858047a530e5b9bea45bcda16 | 27 |
| 7. | trzBB06.tmp | d26580a8d2ab3abac6dd5c9f06b66533 | 19 |
| 8. | Genius.exe | f542c923bcd0fbb77ddf2791ceda1d4d | 4 |
| 9. | DataMgr.exe | d0a9e04130815a1d00f4077a535bbd52 | 3 |
Registry Details
Analysis Report
General information
| Family Name: | Trojan.Snoozer |
|---|---|
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
62bf2ce05348019bbe7ff22cb3b90047
SHA1:
93a75418fb4f54233cb32003e9baa644e9a2e86f
SHA256:
21529004BBC59672B13C64CED20273866BBB1C1C83D92C7A8FABC75726508871
File Size:
137.54 KB, 137536 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
Show More
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| HTTO GROUP Ltd | GlobalSign CodeSigning CA - G2 | Self Signed |
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 77 |
|---|---|
| Potentially Malicious Blocks: | 0 |
| Whitelisted Blocks: | 77 |
| Unknown Blocks: | 0 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Agent.M
- Agent.MH
- Agent.MI
- Agent.MU
- Autorun.LA
Show More
- FakeAV.AU
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\nsj4795.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete |
| c:\users\user\appdata\local\temp\nsy46ba.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete |
| c:\users\user\appdata\local\temp\~nsu.tmp\au_.exe | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete,LEFT 262144 |
Registry Modifications
Registry Modifications
This section lists registry keys and values that were created, modified and/or deleted by samples in this family. Windows Registry activity can provide valuable insight into malware functionality. Additionally, malware often creates registry values to allow itself to automatically start and indefinitely persist after an initial infection has compromised the system.| Key::Value | Data | API Name |
|---|---|---|
| HKLM\system\controlset001\control\session manager::pendingfilerenameoperations | \??\C:\Users\Zsxfeidy\AppData\Local\Temp\~nsu.tmp\Au_.exe | RegNtPreCreateKey |
| HKLM\system\controlset001\control\session manager::pendingfilerenameoperations | \??\C:\Users\Zsxfeidy\AppData\Local\Temp\~nsu.tmp\Au_.exe\??\C:\Users\Zsxfeidy\AppData\Local\Temp\~nsu.tmp | RegNtPreCreateKey |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Process Shell Execute |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
"C:\Users\Zsxfeidy\AppData\Local\Temp\~nsu.tmp\Au_.exe" _?=c:\users\user\downloads\
|


