Trojan.OxyPumper
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 3,542 |
| Threat Level: | 80 % (High) |
| Infected Computers: | 144,552 |
| First Seen: | April 23, 2016 |
| Last Seen: | September 22, 2026 |
| OS(es) Affected: | Windows |
The detection of Trojan.OxyPumper on your system indicates a potential security threat that requires immediate attention. This type of malware can compromise your computer's integrity and put your personal data at risk. It is essential to understand the nature of this threat and take prompt action to remove it and prevent future infections.
Table of Contents
What Is Trojan.OxyPumper?
Trojan.OxyPumper is a type of malware that can infiltrate your system without your knowledge or consent. The name "Trojan" refers to the method of infection, which often involves disguising itself as a legitimate program or attachment. Once inside, it can cause a range of problems, from stealing sensitive information to disrupting system performance. The specific characteristics of Trojan.OxyPumper are not well-documented, but its detection suggests that your system has been compromised.
How Trojan.OxyPumper Operates
Malware like Trojan.OxyPumper typically operates by exploiting vulnerabilities in your system or using social engineering tactics to trick you into installing it. Once installed, it can communicate with its creators, allowing them to control your system remotely. This can lead to unauthorized access to your files, passwords, and other sensitive data. The malware may also install additional components, such as keyloggers or ransomware, to further compromise your system.
Symptoms of Infection
The symptoms of a Trojan.OxyPumper infection can vary, but common signs include slow system performance, unexpected pop-ups or advertisements, and unfamiliar programs or icons on your desktop. You may also notice that your browser settings have been changed or that your system is crashing frequently. In some cases, the malware may not exhibit any noticeable symptoms, making it difficult to detect without the aid of security software.
How to Remove Trojan.OxyPumper
- Restart your system in Safe Mode with Networking to prevent the malware from loading and to allow for a more effective removal process.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system and detect any malicious components.
- Uninstall any suspicious programs or applications that may be related to the infection.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any malicious extensions or add-ons.
- Reboot your system and perform another scan with your anti-malware tool to ensure that all remnants of the malware have been removed.
Conclusion
Removing Trojan.OxyPumper from your system requires a combination of technical expertise and caution. By following the steps outlined above and using reputable security software, you can help to eliminate the threat and prevent future infections. It is essential to remain vigilant and take proactive measures to protect your system, such as keeping your operating system and software up-to-date, using strong passwords, and avoiding suspicious attachments or links. By taking these steps, you can help to ensure the integrity of your system and safeguard your personal data.
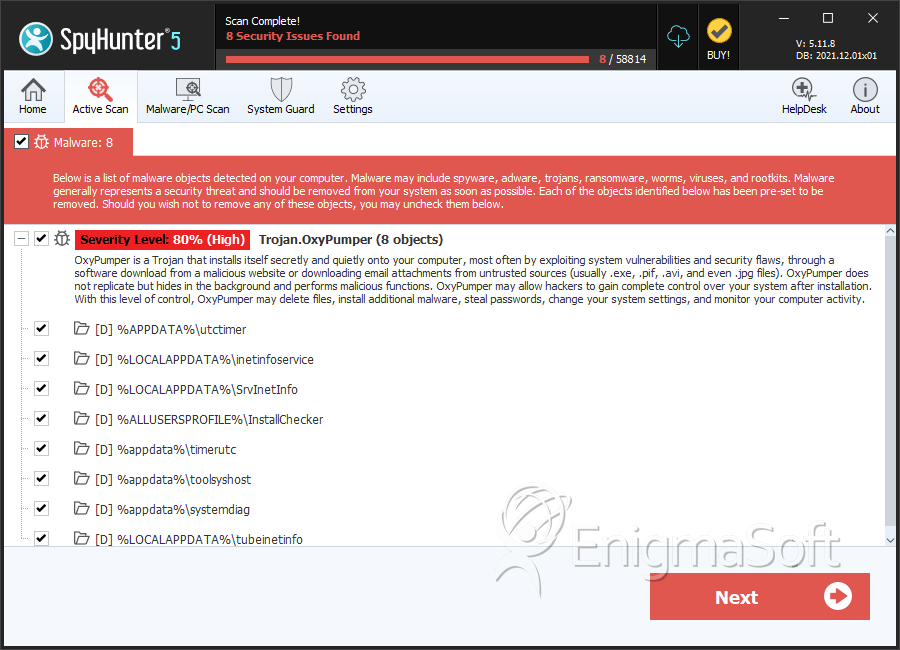
SpyHunter Detects & Remove Trojan.OxyPumper
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | Updater.exe | ad5790070d459c64b1a6353979b570e1 | 196 |
| 2. | utcwatcher.exe | 059fd9d60ee47bc6b266a4fe7a9da1b5 | 138 |
| 3. | updater[1].exe | 9c9cec8413f429aa121c7238be78898d | 112 |
| 4. | ReportSender.exe | 4ad090268af0a45317126f2dae8c4a7e | 50 |
| 5. | ermgr.exe | ccb2406905986e0bc7ab7e8025932d72 | 31 |
| 6. | wizardguid.exe | 80c1c53ce63cba93572b31f02ec92f5a | 31 |
Registry Details
Directories
Trojan.OxyPumper may create the following directory or directories:
| %ALLUSERSPROFILE%\EDSUpdSrv |
| %ALLUSERSPROFILE%\InstallChecker |
| %ALLUSERSPROFILE%\RegisterObject |
| %ALLUSERSPROFILE%\RenewalService |
| %ALLUSERSPROFILE%\UpService |
| %ALLUSERSPROFILE%\VideoMemoryDiagnostic |
| %APPDATA%\KeyCreator |
| %APPDATA%\ReportErr |
| %APPDATA%\perftrack |
| %APPDATA%\threatdatabase |
| %APPDATA%\utctimer |
| %LOCALAPPDATA%\InetInfo |
| %LOCALAPPDATA%\SrvInetInfo |
| %LOCALAPPDATA%\inetinfoservice |
| %LOCALAPPDATA%\inst |
| %LOCALAPPDATA%\instopch |
| %LOCALAPPDATA%\netinfokit |
| %LOCALAPPDATA%\netinformapp |
| %LOCALAPPDATA%\tubeinetinfo |
| %UserProfile%\Local Settings\Application Data\netinformapp |
| %UserProfile%\SoundProvider |
| %appdata%\SysInfoTool |
| %appdata%\syshost |
| %appdata%\systemdiag |
| %appdata%\timerutc |
| %appdata%\toolsyshost |
| %appdata%\videoappriser |
Analysis Report
General information
| Family Name: | Trojan.OxyPumper |
|---|---|
| Signature status: | Root Not Trusted |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
54d855c8c2f1e7e0dffb29867c7b7bbd
SHA1:
6d14bf4894ab2ecd59dee8ca7fd06db3d9dee9c1
SHA256:
55F741231E1D4B4CE74D315098975C7C1B7A32BA3E82811263592C86DECA9DEB
File Size:
3.08 MB, 3081160 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| File Description | iPumper |
| File Version | 1,0,1,708 |
| Internal Name | iPumper |
| Legal Copyright | Copyright 2012 |
| Original Filename | iPumper.exe |
| Product Name | iPumper |
| Product Version | 1,0,1,708 |
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Escolade Solutions LTD. | AddTrust External CA Root | Root Not Trusted |
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 1,476 |
|---|---|
| Potentially Malicious Blocks: | 267 |
| Whitelisted Blocks: | 1,157 |
| Unknown Blocks: | 52 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\6d14bf4894ab2ecd59dee8ca7fd06db3d9dee9c1_0003081160_006984.log | Read Attributes,Synchronize,Write Data |
| c:\users\user\appdata\local\temp\htmlayout.dll | Read Attributes,Synchronize,Write Data |


