Trojan.Farfli.M
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 14,892 |
| Threat Level: | 90 % (High) |
| Infected Computers: | 1,013 |
| First Seen: | July 24, 2009 |
| Last Seen: | August 1, 2026 |
| OS(es) Affected: | Windows |
The detection of Trojan.Farfli.M on your system indicates a potential security threat that requires immediate attention. This report aims to provide you with a comprehensive understanding of the threat, its operational methods, symptoms of infection, and most importantly, steps to remove it from your system.
Table of Contents
What Is Trojan.Farfli.M?
Trojan.Farfli.M is identified as a Trojan-type threat, which is a broad category of malware designed to deceive users into installing it on their systems. Unlike viruses, Trojans do not replicate themselves but can cause significant harm by stealing data, installing additional malware, or providing unauthorized access to the infected system. The name itself does not directly indicate a specific malware family, but its classification as a Trojan suggests it operates by disguising itself as legitimate software to gain unauthorized access to a computer system.
How Trojan.Farfli.M Operates
Trojan.Farfli.M, like other Trojans, is likely to operate by exploiting vulnerabilities in software or tricking users into executing it. Once installed, it can create backdoors for remote access, allowing attackers to control the infected system, steal sensitive information, or use the system for malicious activities such as spamming or distributing malware. The exact operational methods can vary, but the primary goal is to remain undetected while maximizing the damage or profit for the attackers.
Symptoms of Infection
Symptoms of a Trojan.Farfli.M infection can be subtle and may not be immediately noticeable. Common indicators include unusual system behavior, such as unexpected crashes, slow performance, or unfamiliar programs running in the background. Users might also notice changes in their browser settings, unexpected pop-ups, or suspicious network activity. Since Trojans can be designed to evade detection, some infections might only be discovered through regular security scans or when the malware executes a noticeable malicious action.
How to Remove Trojan.Farfli.M
- Boot into Safe Mode with Networking: This will help prevent the malware from loading and give you a cleaner environment to perform removal steps.
- Perform a Full Scan with a Reputable Tool: Utilize a trusted anti-malware tool, such as SpyHunter, to scan your system thoroughly. These tools are designed to detect and remove malware, including Trojans like Trojan.Farfli.M.
- Uninstall Suspicious Programs: Go through your installed programs and remove any that you don't recognize or that were installed around the time you suspect the infection occurred.
- Reset Your Browser: If you use Chrome, Firefox, or Edge, reset the browser to its default settings. This can help remove any malicious extensions or settings changes made by the Trojan.
- Reboot and Re-scan: After completing the above steps, restart your computer and perform another full scan with your anti-malware tool to ensure that all traces of the malware have been removed.
Conclusion
Removing Trojan.Farfli.M requires careful and systematic steps to ensure that all components of the malware are eliminated from your system. It's crucial to stay vigilant and maintain good security practices to prevent future infections, including keeping your operating system and software up to date, using strong antivirus protection, and being cautious when opening email attachments or downloading software from the internet. By following the removal steps outlined and maintaining a proactive security stance, you can protect your system and data from threats like Trojan.Farfli.M.
Aliases
11 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Sophos | Mal/Banker-E |
| NOD32 | Win32/Spy.Banker.QNJ |
| McAfee-GW-Edition | Trojan.Dropper.Gen |
| Ikarus | Trojan-Downloader.Win32.Banload |
| Fortinet | W32/Banker.AHUM!tr |
| F-Secure | Trojan-Banker.Win32.Banker.ahum |
| BitDefender | Trojan.Spy.Delf.NUJ |
| AVG | PSW.Banker5.LES |
| Authentium | W32/SuspPack.M.gen!Eldorado |
| AntiVir | TR/Dropper.Gen |
| a-squared | Trojan-Downloader.Win32.Banload!IK |
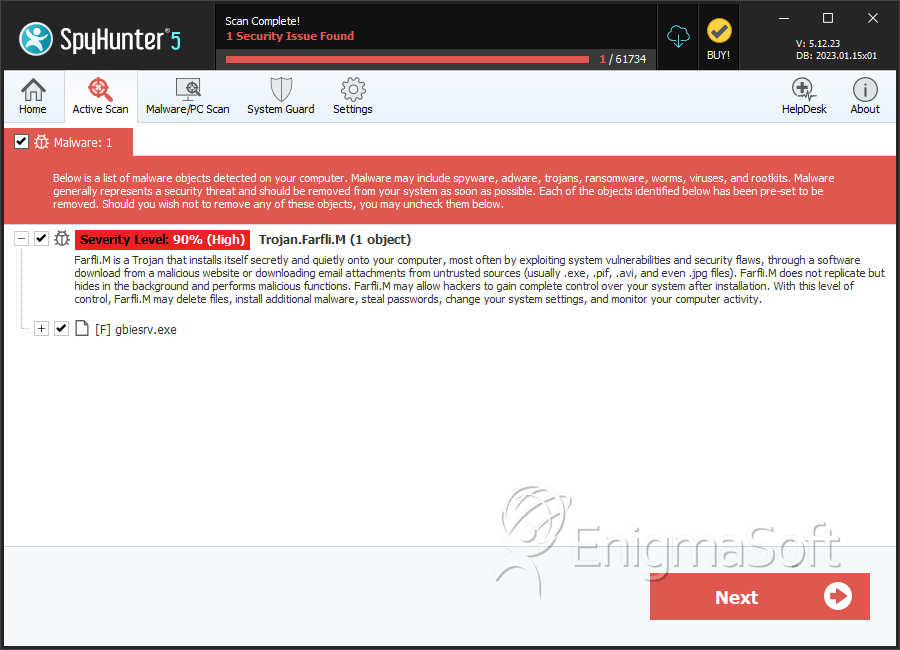
SpyHunter Detects & Remove Trojan.Farfli.M
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | gbiesrv.exe | 83d97fff4b8c730dbd22286b48ab50af | 0 |
Analysis Report
General information
| Family Name: | Trojan.Farfli.M |
|---|---|
| Packers: | UPX |
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
e3ff2e1f38477b0ed9308268cf8ee9ef
SHA1:
fda39646b52f2e5cd6ff598c1ab1f50a82a2de12
SHA256:
EAFD32A144A4BF7D15C3FA3F3B390DEA349C72E85B76F1CC33CBC388E5738C93
File Size:
340.04 KB, 340044 bytes
|
|
MD5:
e4c264cc4846043c30f2d487d580d9a0
SHA1:
36582072f0d824a7281bff1d033647ebe717d715
SHA256:
AF3CF7261DFCDFABBC932F07A18F2724694DE0B7AF0B85EDB8E7F2895529EA7A
File Size:
581.70 KB, 581701 bytes
|
|
MD5:
464859672cc32fe42fae3e5a03d6f8bd
SHA1:
8bf030ad3967477e095f054d959282bd16d66d5e
SHA256:
C00BF46DA49EB900D865C0C301BACDC2A1734CF7664F97CE2B0FC10B7262D12A
File Size:
751.62 KB, 751616 bytes
|
|
MD5:
b2a316ea11ecd8edf26697e38f3636db
SHA1:
8b8608745a4f0417960b2a03fcc8049fd65a2a81
SHA256:
77CDA2ED920FAEB719F62D189A723D06F95B1D875EE3CD0B5849B53DF1D2CD4E
File Size:
1.04 MB, 1036800 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has been packed
- File has exports table
- File is 32-bit executable
- File is console application (IMAGE_SUBSYSTEM_WINDOWS_CUI)
- File is either console or GUI application
Show More
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | Tachyon Anti-Virus Engine. |
| Company Name |
|
| File Description |
|
| File Version |
|
| Internal Name | TyAv32 |
| Legal Copyright |
|
| Original Filename | TyAv32.dll |
| Product Name |
|
| Product Version |
|
File Traits
- dll
- HighEntropy
- packed
- WriteProcessMemory
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 844 |
|---|---|
| Potentially Malicious Blocks: | 3 |
| Whitelisted Blocks: | 454 |
| Unknown Blocks: | 387 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Syscall Use |
Show More
|
| Process Shell Execute |
|
| Anti Debug |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\fda39646b52f2e5cd6ff598c1ab1f50a82a2de12_0000340044.,LiQMAxHB
|
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\36582072f0d824a7281bff1d033647ebe717d715_0000581701.,LiQMAxHB
|


