Trojan.ArchSMS
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 80 % (High) |
| Infected Computers: | 1,018 |
| First Seen: | September 21, 2011 |
| Last Seen: | October 24, 2025 |
| OS(es) Affected: | Windows |
The detection of Trojan.ArchSMS on your system indicates a potential security threat that requires immediate attention. This report aims to provide you with a comprehensive understanding of the threat, its operations, symptoms, and most importantly, steps to remove it from your system.
Table of Contents
What Is Trojan.ArchSMS?
Trojan.ArchSMS is identified as a Trojan-type threat, which is a broad category of malware designed to deceive users into installing it on their systems. Unlike viruses, Trojans do not replicate themselves but can cause significant harm by stealing sensitive information, installing additional malware, or allowing unauthorized access to the infected system. The name "Trojan.ArchSMS" suggests it may have capabilities related to SMS or text messaging, but without specific details, it's crucial to approach its removal with a general understanding of Trojan threats.
How Trojan.ArchSMS Operates
Trojan.ArchSMS, like other Trojans, operates by disguising itself as legitimate software or piggybacking on legitimate programs to gain entry into a system. Once installed, it can perform a variety of malicious activities, including but not limited to, data theft, spyware functionalities, or acting as a backdoor for other malware. The exact operations of Trojan.ArchSMS can vary, but its primary goal is to compromise the security and integrity of the infected system for the benefit of the attackers.
Symptoms of Infection
Symptoms of a Trojan infection can be subtle and may not always be immediately apparent. Common indicators include unexpected changes to system settings, appearance of unfamiliar programs or icons, unusual network activity, slowed system performance, or frequent crashes. In some cases, Trojans may also trigger security software alerts, though they are designed to evade detection. Being vigilant about these symptoms can help in early detection and removal of the threat.
How to Remove Trojan.ArchSMS
- Boot your system into Safe Mode with Networking to limit the malware's ability to interfere with the removal process. This mode allows you to use the internet to download removal tools if necessary.
- Perform a full scan of your system using a reputable anti-malware tool such as SpyHunter. Ensure your anti-malware software is updated to the latest version for the best detection and removal capabilities.
- Uninstall suspicious programs that you do not recognize or that were installed around the time the malware was detected. Be cautious and only remove programs you are certain are not needed.
- Reset your web browsers (Chrome, Firefox, Edge, etc.) to their default settings. This can help remove any malicious extensions or settings changes made by the Trojan.
- After completing the above steps, reboot your system and then perform another full scan with your anti-malware tool to ensure that all traces of the malware have been removed.
Conclusion
Removing Trojan.ArchSMS requires a methodical approach to ensure all components of the malware are eliminated from your system. By following the steps outlined above, you can effectively remove the threat and restore your system's security. Remember, prevention is key; always be cautious when downloading software, avoid suspicious links or emails, and keep your security software up to date to protect against future infections.
SpyHunter Detects & Remove Trojan.ArchSMS
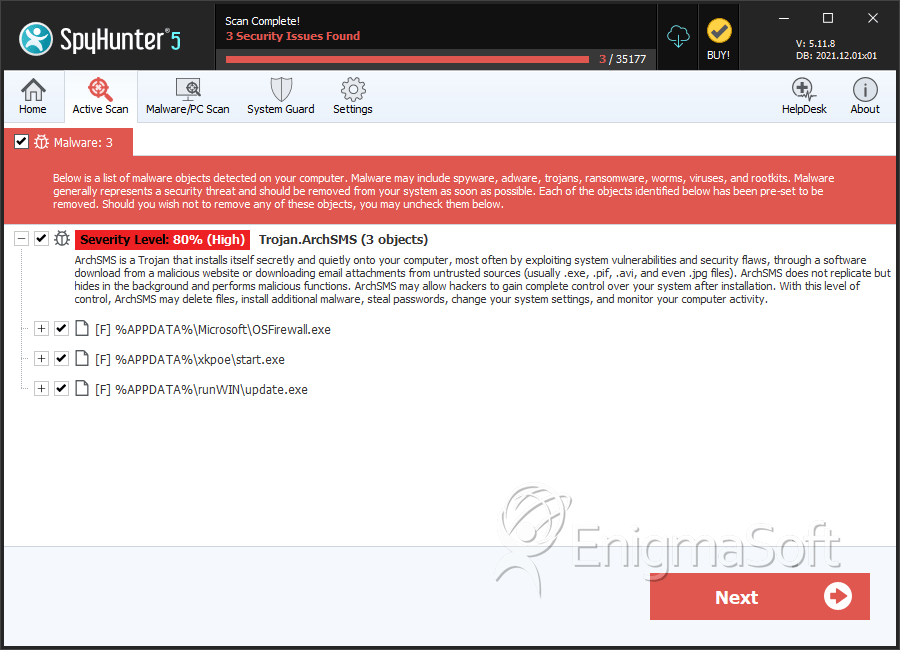
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | start.exe | 262bea6bc12282cde3fb4010dc9b31f2 | 26 |
| 2. | OSFirewall.exe | 494cc484233a807b4fd93bf2c90a2741 | 13 |
| 3. | update.exe | 045578eb6f48410a93e040ecc0908c2e | 1 |
Registry Details
Analysis Report
General information
| Family Name: | Trojan.ArchSMS |
|---|---|
| Signature status: | Root Not Trusted |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
977cb302f626cec8c61597e651345820
SHA1:
527689778406f5db5b5eb92aa2ce0d46346f601a
SHA256:
7F37FFB54F6CA3501834D517CF513890B528BF2C90830250469B23F7AEC3AB03
File Size:
277.98 KB, 277976 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
Show More
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| BERNEX APLICACIONES SL | Go Daddy Class 2 Certification Authority | Root Not Trusted |
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\nsc5f49.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsk59ba.tmp\logo.bmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsk59ba.tmp\modern-wizard.bmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsk59ba.tmp\nsdialogs.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsk59ba.tmp\nsisdl.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsk59ba.tmp\system.dll | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Network Winsock2 |
|
| Network Winsock |
|


