Stop.G Ransomware
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 100 % (High) |
| Infected Computers: | 825 |
| First Seen: | July 24, 2009 |
| Last Seen: | October 24, 2025 |
| OS(es) Affected: | Windows |
The detection of Stop.G Ransomware on your system indicates a serious security threat that requires immediate attention. Ransomware is a type of malware designed to encrypt and hold hostage the data on a victim's computer, demanding payment in exchange for the decryption key. In this report, we will provide an overview of the Stop.G Ransomware threat, its operational methods, symptoms of infection, and steps to remove it from your system.
Table of Contents
What Is Stop.G Ransomware?
Ransomware, like Stop.G Ransomware, is a malicious software that uses encryption to deny access to a victim's data. The primary goal of ransomware is to extort money from the victim by demanding a ransom in exchange for the decryption key. The name Stop.G Ransomware itself does not provide specific information about its origin or the malware family it belongs to, but its detection signifies a ransomware threat that needs to be addressed.
How Stop.G Ransomware Operates
Stop.G Ransomware, like other ransomware, typically operates by first gaining access to a victim's system. This can happen through various means, such as exploiting vulnerabilities in software, phishing emails, or infected software downloads. Once inside, it scans the system for target files, which can include documents, images, videos, and other data types. It then encrypts these files, making them inaccessible to the user. The ransomware usually leaves a ransom note, demanding payment in cryptocurrency for the decryption key. The operators of the ransomware may also threaten to delete the decryption key or publish the encrypted data if the ransom is not paid within a specified timeframe.
Symptoms of Infection
Symptoms of a Stop.G Ransomware infection can include the inability to access files, files having unusual extensions appended to their names, and the presence of a ransom note or demands for payment. The system may also exhibit slower performance, and in some cases, the ransomware may attempt to spread to other connected devices or networks. It's crucial to act quickly upon noticing any of these symptoms to minimize the damage.
How to Remove Stop.G Ransomware
- Boot your computer in Safe Mode with Networking. This will allow you to use the internet to download removal tools without the malware interfering.
- Download and install a reputable anti-malware tool, such as SpyHunter. Perform a full scan of your system to detect and remove the Stop.G Ransomware and any other malware that may be present.
- Uninstall any suspicious programs that you have installed recently. These could be potentially malicious and connected to the ransomware infection.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings. This can help remove any malicious extensions or settings that the ransomware may have altered.
- Reboot your computer and perform another full scan with your anti-malware tool to ensure that all traces of the malware have been removed.
Conclusion
The detection and removal of Stop.G Ransomware require a combination of immediate action and careful system cleaning. It's essential to follow the steps outlined above and consider seeking professional help if you're not comfortable with the removal process. Preventing future infections involves keeping your operating system and software up to date, using strong antivirus software, avoiding suspicious downloads and emails, and regularly backing up your important data. By taking these precautions and being vigilant, you can significantly reduce the risk of falling victim to ransomware and other cyber threats.
Aliases
5 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Sophos | Mal/FakeVirPk-A |
| Prevx1 | Malicious Software |
| NOD32 | a variant of Win32/Kryptik.DL |
| Ikarus | Rootkit.Win32.TDSS |
| CAT-QuickHeal | (Suspicious) - DNAScan |
SpyHunter Detects & Remove Stop.G Ransomware
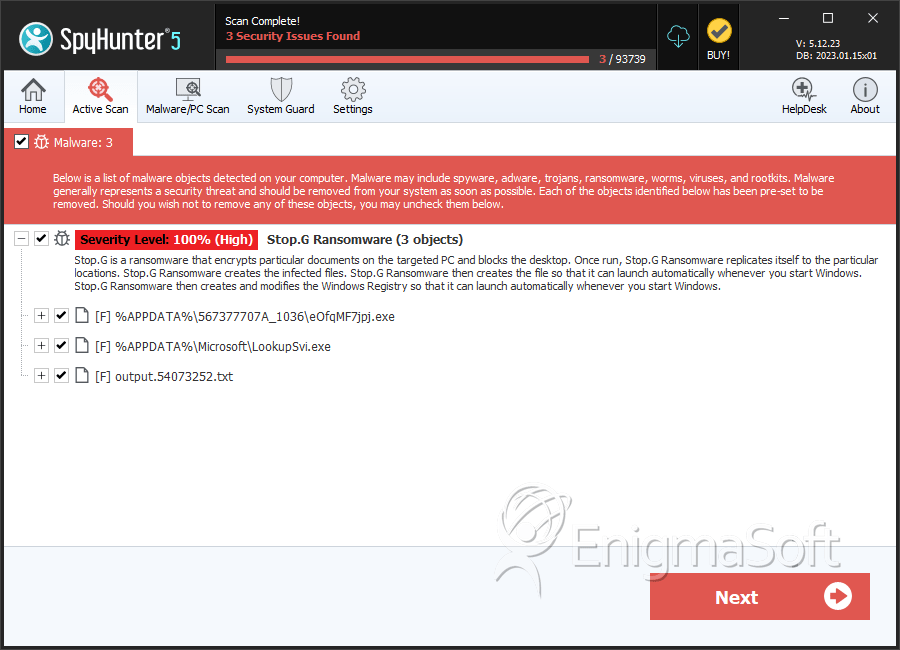
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | eOfqMF7jpj.exe | eb62ea587f3dffc8dd3414c3a786854d | 334 |
| 2. | LookupSvi.exe | bc61e848984ec98f66479d18562f6745 | 16 |
| 3. | output.54073252.txt | 77f85005063ba0e6579649b51236c2f9 | 0 |


