PUP.Patcher.F
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 20,449 |
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 1,290 |
| First Seen: | July 24, 2009 |
| Last Seen: | October 5, 2026 |
| OS(es) Affected: | Windows |
The detection of PUP.Patcher.F on your system indicates the presence of a potentially unwanted program (PUP) that may compromise your computer's security and performance. It is essential to understand the nature of this threat and take immediate action to remove it and prevent future infections.
Table of Contents
What Is PUP.Patcher.F?
PUP.Patcher.F is a type of malicious software that is designed to evade detection and persist on a compromised system. While it may not be as overtly destructive as other types of malware, PUPs can still cause significant problems, including slowing down your computer, displaying unwanted advertisements, and potentially leading to more severe infections. PUPs often exploit vulnerabilities in software or trick users into installing them through deceptive means.
How PUP.Patcher.F Operates
PUP.Patcher.F, like other PUPs, typically operates by installing itself on a system without the user's knowledge or consent. It may do this by bundling itself with legitimate software, exploiting vulnerabilities in operating systems or applications, or using social engineering tactics to trick users into installing it. Once installed, PUP.Patcher.F can modify system settings, create unwanted registry entries, and communicate with its command and control servers to receive updates or transmit stolen data.
Symptoms of Infection
Identifying a PUP.Patcher.F infection can be challenging, as it may not exhibit obvious symptoms. However, some common signs of a PUP infection include unexpected pop-ups or advertisements, slow system performance, unfamiliar programs or icons, and changes to browser settings or homepage. If you notice any of these symptoms, it is crucial to take immediate action to scan your system and remove any detected threats.
- Unwanted advertisements or pop-ups
- Slow system performance or crashes
- Unfamiliar programs or icons
- Changes to browser settings or homepage
How to Remove PUP.Patcher.F
- Boot your computer in Safe Mode with Networking to prevent PUP.Patcher.F from loading and to allow for a more effective removal process.
- Perform a full scan of your system using a reputable anti-malware tool, such as SpyHunter, to detect and remove PUP.Patcher.F and any related files or registry entries.
- Uninstall any suspicious programs or applications that may be related to the PUP infection.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any unwanted extensions or add-ons.
- Reboot your computer and perform another full scan to ensure that PUP.Patcher.F has been completely removed.
Conclusion
Removing PUP.Patcher.F from your system requires a combination of technical knowledge and caution. By following the steps outlined above and using reputable anti-malware tools, you can effectively remove this potentially unwanted program and prevent future infections. It is essential to remain vigilant and take proactive measures to protect your system, including keeping your operating system and software up to date, using strong antivirus software, and avoiding suspicious downloads or links.
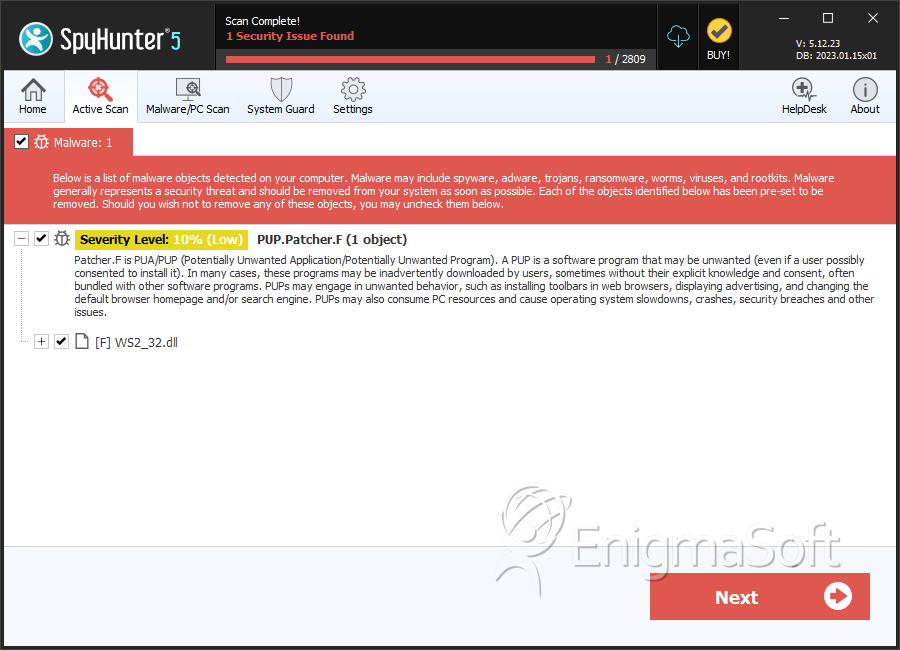
SpyHunter Detects & Remove PUP.Patcher.F
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | WS2_32.dll | 9aa547e810f181a8f32e49198bfadd2c | 0 |
Analysis Report
General information
| Family Name: | PUP.Patcher.F |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
3696f7a6724f532dd93e39e418f98709
SHA1:
5b57fc7e336e4ce49961d3c25817b0924ed9e051
SHA256:
0DE021FF8632459A81AB987628973B467C6FEF5C86F13C7CB5274A21429287C1
File Size:
65.02 KB, 65024 bytes
|
|
MD5:
635e5ea39fd78cf645b0de694e485c76
SHA1:
3a152abc557e767758db429b4bd16b789b38b9b6
SHA256:
6377EC011C79C16C9364328BF3C689A511A6CC70F451A55A199CB55FCC5B6075
File Size:
32.26 KB, 32256 bytes
|
|
MD5:
4cf8f6b4d7bdc25aae15987ffc375eba
SHA1:
76971a24361f6a885bc8dd9b21dffc4ac64ebea1
SHA256:
90CB3CE602A3FF547E77D6F0E8F60CF91335780A56F64A765F9C089FBEDE48DB
File Size:
7.17 KB, 7168 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has been packed
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
Show More
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


File Traits
- HighEntropy
- No Version Info
- packed
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 16 |
|---|---|
| Potentially Malicious Blocks: | 11 |
| Whitelisted Blocks: | 3 |
| Unknown Blocks: | 2 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Patcher.F
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Anti Debug |
|
| User Data Access |
|