HackTool:Win32/Appcrack
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 274 |
| First Seen: | December 24, 2012 |
| Last Seen: | January 12, 2026 |
| OS(es) Affected: | Windows |
The detection of HackTool:Win32/Appcrack on your system indicates the presence of a potentially malicious tool that could be used to compromise your computer's security. This type of detection is often associated with software that can be used to bypass security mechanisms or crack passwords, which can lead to unauthorized access to your system or data.
Table of Contents
What Is HackTool:Win32/Appcrack?
HackTool:Win32/Appcrack is a type of threat that has been identified as a hacktool, which is a category of malicious software designed to help attackers gain unauthorized access to systems or data. The name itself suggests that it is related to cracking or bypassing security mechanisms, but without more specific information, it's difficult to determine the exact nature or capabilities of this particular threat.
How HackTool:Win32/Appcrack Operates
Generally, hacktools like HackTool:Win32/Appcrack are designed to exploit vulnerabilities in software or operate in a way that evades detection by traditional security measures. They can be used for a variety of malicious purposes, including but not limited to, cracking passwords, bypassing activation mechanisms for software, or even creating backdoors for future access. The exact operation of HackTool:Win32/Appcrack would depend on its specific design and the intentions of its creators or users.
Symptoms of Infection
Symptoms of an infection can vary widely depending on the nature of the threat and how it is being used. Common indicators of a problem might include unexpected changes to your system, such as new programs or icons appearing, unusual network activity, or system crashes. However, some malicious tools are designed to operate stealthily and may not exhibit obvious symptoms, making them harder to detect without the aid of security software.
- Unexplained changes to system settings or files
- Appearance of unknown programs or processes
- Increased network activity without a clear cause
- Frequent system crashes or instability
How to Remove HackTool:Win32/Appcrack
- Boot your computer in Safe Mode with Networking to limit the malware's ability to interfere with the removal process.
- Perform a full scan of your system using a reputable anti-malware tool, such as SpyHunter, to detect and remove all related files and entries.
- Uninstall any suspicious programs that were installed around the time of the infection. Be cautious and only remove programs you are certain are malicious or unnecessary.
- Reset your web browsers (Chrome, Firefox, Edge, etc.) to their default settings to remove any malicious extensions or settings changes.
- Reboot your computer and perform another full scan to ensure that all remnants of the malware have been removed.
Conclusion
The detection and removal of HackTool:Win32/Appcrack require careful attention to ensure that all components of the malware are eliminated from your system. By following the steps outlined above and maintaining vigilance with regular system scans and updates, you can help protect your computer from future infections. It's also crucial to practice safe computing habits, such as avoiding suspicious downloads and being cautious with email attachments, to minimize the risk of encountering malicious software.
Aliases
4 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Panda | Trj/CI.A |
| Ikarus | Win32.SuspectCrc |
| Microsoft | HackTool:Win32/Appcrack |
| AntiVir | SPR/Tool.Appcrack.2 |
SpyHunter Detects & Remove HackTool:Win32/Appcrack
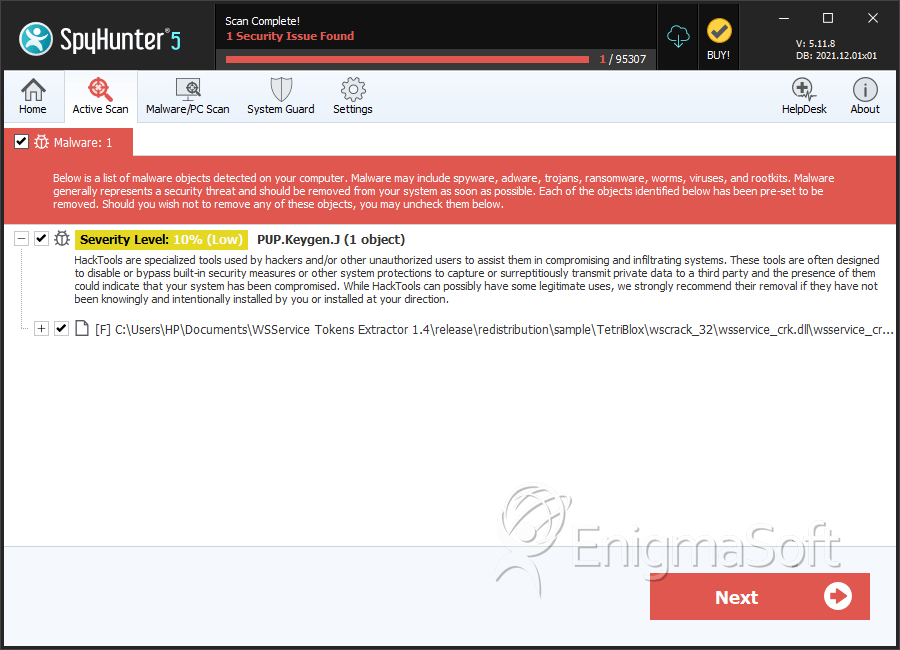
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | wsservice_crk.dll | 396cb1827e7c4bfc0384360ef4acf4f8 | 80 |
Analysis Report
General information
| Family Name: | PUP.Keygen.J |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
16190159b3322884323acb7fb0c216de
SHA1:
e2701ea5c0c7f358ad307096ed0a0f7e18a14463
SHA256:
7DB7C09B47C566513F39F751CFC2847B612084AF6339A518B0D5C7E0825B6D5C
File Size:
23.04 KB, 23040 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.
File Traits
- 2+ executable sections
- HighEntropy
- No Version Info
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 2 |
|---|---|
| Potentially Malicious Blocks: | 2 |
| Whitelisted Blocks: | 0 |
| Unknown Blocks: | 0 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Keygen.J
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Anti Debug |
|
| User Data Access |
|