Adware.SurfeLan
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 20 % (Normal) |
| Infected Computers: | 70 |
| First Seen: | August 5, 2016 |
| Last Seen: | February 28, 2026 |
| OS(es) Affected: | Windows |
The detection of Adware.SurfeLan on your system indicates the presence of unwanted software that may be compromising your online experience and potentially exposing you to more severe threats. Understanding what this detection means and how to address it is crucial for maintaining the security and performance of your computer.
Table of Contents
What Is Adware.SurfeLan?
Adware.SurfeLan refers to a type of adware, which is software designed to display unwanted advertisements on your computer, often in the form of pop-ups, banners, or sponsored content within websites. Unlike viruses or Trojans, adware is typically not malicious in the sense that it does not directly damage your system or steal sensitive information. However, it can significantly disrupt your browsing experience, slow down your computer, and in some cases, lead to more dangerous malware infections by redirecting you to malicious websites or downloading additional unwanted software.
How Adware.SurfeLan Operates
Adware.SurfeLan, like other adware programs, operates by infiltrating your system, often through bundled software downloads, infected email attachments, or exploited vulnerabilities in your browser or operating system. Once installed, it can modify your browser settings, alter your homepage, or change your default search engine to display advertisements. These advertisements can be based on your browsing history, suggesting that the adware may be tracking your online activities to some extent. The primary goal of adware is to generate revenue for its developers through pay-per-click advertising models or by selling your browsing data to third parties.
Symptoms of Infection
The symptoms of an Adware.SurfeLan infection can vary but commonly include an increase in unwanted advertisements appearing on your screen, unexpected changes to your browser settings, slow performance of your computer or browser, and in some cases, the appearance of unwanted toolbars or extensions in your browser. You might also notice that your search results are being redirected to unfamiliar websites or that pop-ups appear even when you're not browsing the internet.
- Increased number of pop-ups and advertisements
- Unexplained changes to your browser's homepage or search engine
- Slow computer or browser performance
- Appearance of unwanted browser toolbars or extensions
How to Remove Adware.SurfeLan
- Boot your computer in Safe Mode with Networking to prevent the adware from loading and to give you a cleaner environment to work in.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system. This can help identify and remove the adware and any other malware that might be present.
- Uninstall any suspicious programs that you do not recognize or that were recently installed. Be cautious and only remove programs that you are sure are not essential to your system's operation.
- Reset your browsers (Chrome, Firefox, Edge, etc.) to their default settings. This can help remove any changes made by the adware, such as unwanted extensions or modified settings.
- Reboot your computer and perform another scan with your anti-malware tool to ensure that all traces of the adware have been removed.
Conclusion
Removing Adware.SurfeLan requires a combination of technical knowledge and the right tools. By following the steps outlined above and maintaining good computing practices, such as regularly updating your software, avoiding suspicious downloads, and using strong, unique passwords, you can protect your system from future infections. Remember, the key to dealing with adware and other types of malware is vigilance and prompt action. If you're unsure about any part of the removal process, consider seeking help from a professional to ensure your system is completely clean and secure.
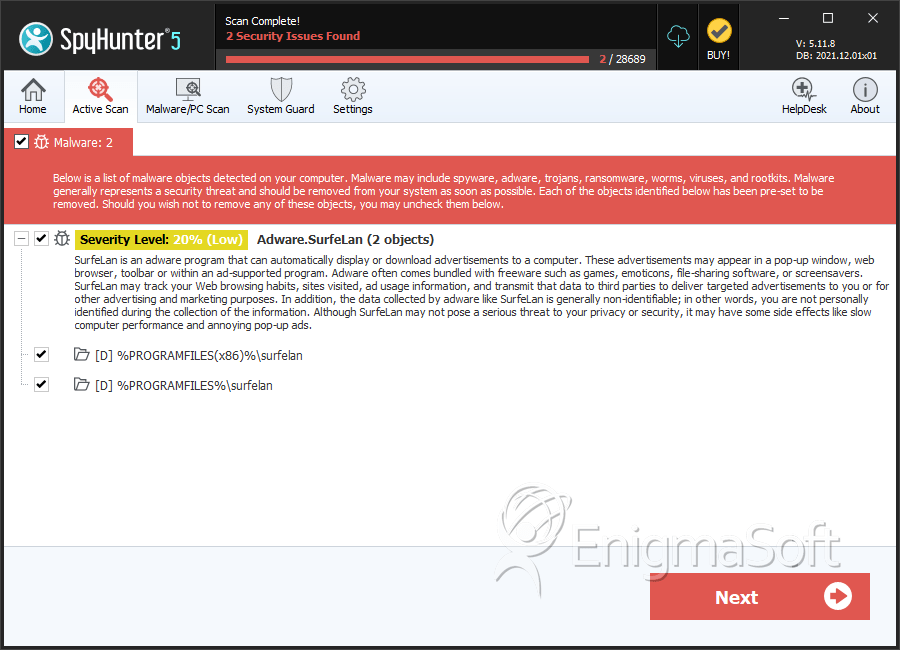
SpyHunter Detects & Remove Adware.SurfeLan
Directories
Adware.SurfeLan may create the following directory or directories:
| %PROGRAMFILES%\surfelan |
| %PROGRAMFILES(x86)%\surfelan |
Analysis Report
General information
| Family Name: | Adware.SurfeLan |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
cb31bf3892737006e81a7bce8c0bd07c
SHA1:
2fa6ce72a982ac61c47c9199addae6bb8166ccc0
SHA256:
6C1C2E9F609AB3E874F747EB4709A442C57AE853B832095A7C0F0C376444E202
File Size:
819.20 KB, 819200 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have security information
- File is .NET application
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
Show More
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.
Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Assembly Version | 2.0.0.117 |
| Company Name | JetSwap Inc. |
| File Description | SafeSurf |
| File Version | 2.0 |
| Internal Name | SafeSurf.exe |
| Legal Copyright | Copyright © JetSwap 2005-2024 |
| Original Filename | SafeSurf.exe |
| Product Name | SafeSurf |
| Product Version | 2.0 |
File Traits
- .NET
- NewLateBinding
- RijndaelManaged
- SmartAssembly
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 1,893 |
|---|---|
| Potentially Malicious Blocks: | 18 |
| Whitelisted Blocks: | 1,121 |
| Unknown Blocks: | 754 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\downloads\log.txt | Generic Write,Read Attributes |
| c:\windows\assembly | Synchronize,Write Attributes |
Registry Modifications
Registry Modifications
This section lists registry keys and values that were created, modified and/or deleted by samples in this family. Windows Registry activity can provide valuable insight into malware functionality. Additionally, malware often creates registry values to allow itself to automatically start and indefinitely persist after an initial infection has compromised the system.| Key::Value | Data | API Name |
|---|---|---|
| HKLM\software\wow6432node\jetswap::tmpregval | 123 | RegNtPreCreateKey |
| HKLM\software\wow6432node\jetswap::tmpregval | RegNtPreCreateKey |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| User Data Access |
|
| Anti Debug |
|
| Encryption Used |
|