Adware.PriceFountain.A
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 12,123 |
| Threat Level: | 20 % (Normal) |
| Infected Computers: | 779 |
| First Seen: | July 24, 2009 |
| Last Seen: | September 25, 2026 |
| OS(es) Affected: | Windows |
The detection of Adware.PriceFountain.A on your system indicates the presence of a potentially unwanted program that may be causing unwanted advertisements and potentially collecting your personal data. It is essential to understand the nature of this threat and take immediate action to remove it from your system to prevent further damage.
Table of Contents
What Is Adware.PriceFountain.A?
Adware.PriceFountain.A is a type of adware program that is designed to display unwanted advertisements on your system, often in the form of pop-ups, banners, or sponsored links. The primary goal of adware is to generate revenue for its creators by displaying advertisements and collecting user data. Adware programs like Adware.PriceFountain.A can be bundled with other software, downloaded from the internet, or installed through exploit kits.
How Adware.PriceFountain.A Operates
Adware.PriceFountain.A operates by installing itself on your system and then connecting to a remote server to download and display advertisements. It may also collect your personal data, such as browsing history, search queries, and other information, to deliver targeted advertisements. In some cases, adware programs can also install additional malware or potentially unwanted programs on your system, which can further compromise your security and privacy.
Symptoms of Infection
The symptoms of Adware.PriceFountain.A infection can vary, but common signs include an increase in unwanted advertisements, slow system performance, and suspicious program installations. You may also notice that your browser homepage or search engine has been changed, or that you are being redirected to unwanted websites. Additionally, you may experience pop-ups, banners, or sponsored links that appear on your screen, even when you are not browsing the internet.
- Unwanted advertisements and pop-ups
- Slow system performance
- Suspicious program installations
- Changed browser homepage or search engine
- Redirects to unwanted websites
How to Remove Adware.PriceFountain.A
- Boot your system in Safe Mode with Networking to prevent the adware from loading and to allow you to download and install removal tools.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system and detect and remove the adware and any other malware that may be present.
- Uninstall any suspicious programs that you have installed recently, as they may be related to the adware infection.
- Reset your browsers, such as Chrome, Firefox, or Edge, to their default settings to remove any changes made by the adware.
- Reboot your system and perform another scan with your anti-malware tool to ensure that the adware has been completely removed.
Conclusion
Removing Adware.PriceFountain.A from your system requires a combination of technical knowledge and the right tools. By following the steps outlined above, you can help to ensure that your system is free from this potentially unwanted program and any other malware that may be present. It is essential to be vigilant and to take immediate action when you detect any suspicious activity on your system to prevent further damage and protect your personal data.
Aliases
6 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Symantec | WinXDefender |
| Ikarus | not-a-virus:AdWare.Win32.Agent.aft |
| CAT-QuickHeal | AdWare.Agent.aft (Not a Virus) |
| AVG | Adware Generic2.ACLG |
| AntiVir | ADSPY/Agent.aft.1 |
| AhnLab-V3 | Win-AppCare/Agent.84992 |
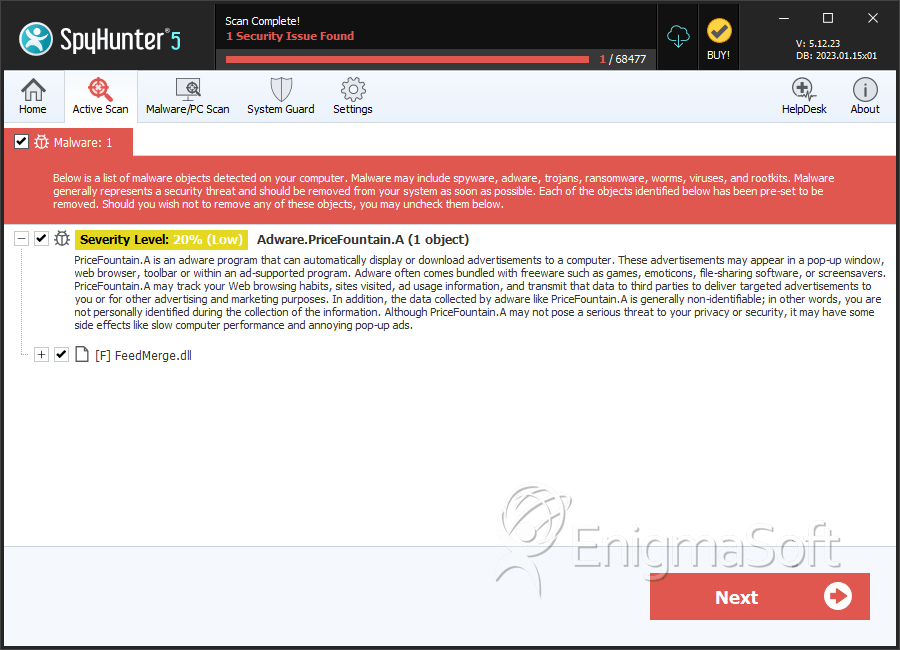
SpyHunter Detects & Remove Adware.PriceFountain.A
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | FeedMerge.dll | 314e1621e8d1a01db19552ece3ac8043 | 0 |
Analysis Report
General information
| Family Name: | Adware.PriceFountain.A |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
dc82a94d8dedad0555a631a1dcbab93a
SHA1:
a6f6380d932b6b310a1e997dee640668db3f7fb3
SHA256:
751EED60328C1552DA1324FB3659075E14526BA3752C13BE817875AC08D1E50A
File Size:
400.38 KB, 400384 bytes
|
|
MD5:
097eef6a357376483b34b721dd3edd45
SHA1:
ce617623e7ae910c67e269db4117d7d364cb99ce
SHA256:
AE07F1027F51D0CEB86308F98AB5FC1FD4456CA13CF54E4C7263D87DCE900E16
File Size:
400.38 KB, 400384 bytes
|
|
MD5:
52260be2bba925e3ca7013ebf64be32c
SHA1:
a676867dcdea026acff6d0f434c8e5fba0b95981
SHA256:
139C30ADC21271AB040D8100113C7C2D80AC55ABBB294EAEF2050E3C7B28508E
File Size:
356.86 KB, 356864 bytes
|
|
MD5:
ae01be8377e963bd26a13c795b787c9e
SHA1:
d162d538e431b5f3477c95d084e51ce629ef7942
SHA256:
DCDC15A600C754B2C31762F806EEB683D2348936F091F25C8BF5FA785A03293D
File Size:
356.86 KB, 356864 bytes
|
|
MD5:
ad8445574f26a336b068d494b28c3e51
SHA1:
9f97ae7735f3deeda11db7a39eeff50da8580207
SHA256:
EE14BEE7D59C9D71E6A4D33A6B82C19CE3CB19758ABF1E56A72A40BE555C1BC2
File Size:
399.87 KB, 399872 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have security information
- File has exports table
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| F I L E Version |
|
| I N T E R N A L Name |
|
| L E G A L Copyright |
|
| O R I G I N A L Filename |
|
| P R O D U C T Version |
|
File Traits
- dll
- HighEntropy
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 1,253 |
|---|---|
| Potentially Malicious Blocks: | 125 |
| Whitelisted Blocks: | 933 |
| Unknown Blocks: | 195 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Syscall Use |
Show More
|
| Process Manipulation Evasion |
|
| Process Shell Execute |
|
| Anti Debug |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\a6f6380d932b6b310a1e997dee640668db3f7fb3_0000400384.,LiQMAxHB
|
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\ce617623e7ae910c67e269db4117d7d364cb99ce_0000400384.,LiQMAxHB
|
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\a676867dcdea026acff6d0f434c8e5fba0b95981_0000356864.,LiQMAxHB
|
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\d162d538e431b5f3477c95d084e51ce629ef7942_0000356864.,LiQMAxHB
|
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\9f97ae7735f3deeda11db7a39eeff50da8580207_0000399872.,LiQMAxHB
|


