Adware.DirectDownloader
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 1,464 |
| Threat Level: | 20 % (Normal) |
| Infected Computers: | 3,436 |
| First Seen: | December 7, 2012 |
| Last Seen: | October 4, 2026 |
| OS(es) Affected: | Windows |
The detection of Adware.DirectDownloader on your system indicates the presence of unwanted software that could be compromising your computer's security and performance. Adware, short for advertising-supported software, is designed to display unwanted advertisements, collect user data, and sometimes redirect users to malicious websites. Understanding the nature of this threat and how it operates is crucial for effective removal and prevention of future infections.
Table of Contents
What Is Adware.DirectDownloader?
Adware.DirectDownloader is identified as a type of adware, a category of malware that prioritizes generating revenue for its developers through advertisements. Unlike viruses or Trojans that aim to cause direct harm or steal sensitive information, adware focuses on disrupting the user experience with pop-ups, banners, and other forms of advertisements. However, its presence can still lead to significant issues, including slowed system performance, increased risk of other malware infections, and potential data breaches due to the collection of user data.
How Adware.DirectDownloader Operates
Adware like Adware.DirectDownloader typically operates by infiltrating a system through bundled software downloads, deceptive links, or exploited vulnerabilities. Once installed, it can manipulate browser settings, install additional software without consent, and monitor user activity to deliver targeted advertisements. This adware may also connect to remote servers to download additional components or update its advertising payload, further compromising system security and user privacy.
Symptoms of Infection
Symptoms of an Adware.DirectDownloader infection can vary but commonly include an unexpected increase in pop-up advertisements, new tabs or windows opening without user initiation, changes in browser homepage or search engine, and overall system slowdown. Users may also notice unfamiliar programs or toolbars installed on their browsers or desktops. These indicators suggest that the adware has successfully embedded itself within the system and is actively working to generate revenue for its creators.
How to Remove Adware.DirectDownloader
- Boot your computer in Safe Mode with Networking to prevent the adware from loading and to gain better control over the removal process.
- Perform a full scan of your system using a reputable anti-malware tool, such as SpyHunter, to detect and remove all components of the adware.
- Uninstall any suspicious programs that were installed around the time the adware was detected. Be cautious and only remove programs you are certain are not needed.
- Reset your web browsers (Chrome, Firefox, Edge, etc.) to their default settings to remove any changes made by the adware, such as altered homepage settings or installed extensions.
- Reboot your computer and run another scan with your anti-malware tool to ensure all components of the adware have been removed. This step is crucial to confirm the effectiveness of the removal process.
Conclusion
Removing Adware.DirectDownloader requires a systematic approach to ensure all its components are eliminated from the system. By following the steps outlined above and maintaining vigilance through regular system scans and safe browsing practices, users can protect their computers from similar threats. It's also essential to keep software up to date, avoid suspicious downloads, and use reputable security software to safeguard against a wide range of malware, including adware. Remember, prevention and prompt action are key to minimizing the impact of malware infections and maintaining a secure computing environment.
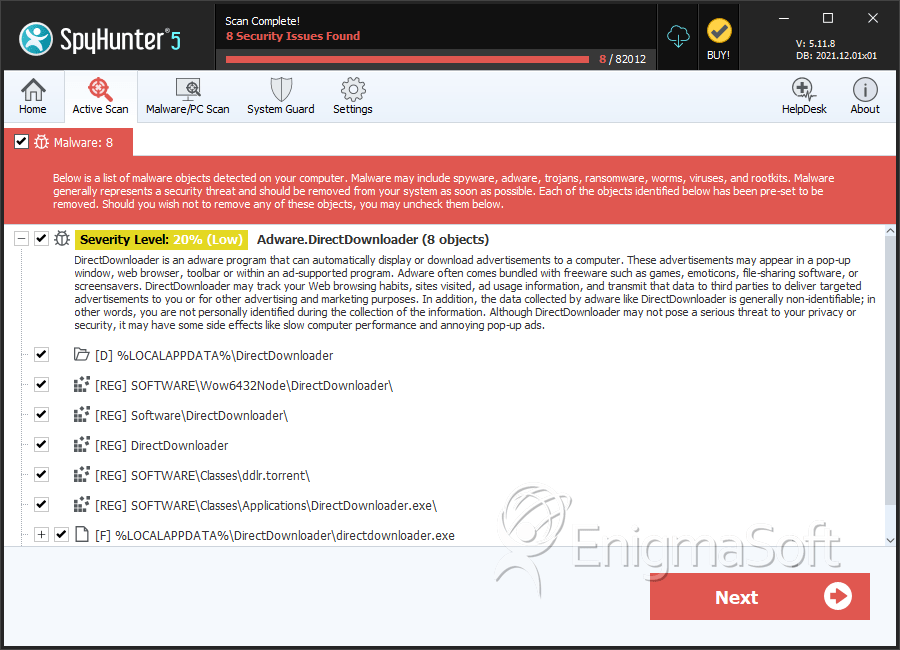
SpyHunter Detects & Remove Adware.DirectDownloader
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | DirectDownloader.exe | de163f6c43314b0162b5364bbae63a3f | 2 |
Registry Details
Directories
Adware.DirectDownloader may create the following directory or directories:
| %LOCALAPPDATA%\DirectDownloader |
| %UserProfile%\Local Settings\Application Data\DirectDownloader |
Analysis Report
General information
| Family Name: | Adware.DirectDownloader |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
fb017baec208e018cd8bc30e04020d81
SHA1:
647648b0ce1deba10189841a02336d6b7489408e
SHA256:
8F5C9335F8E5C273F4F510DCBF94E6BC41340027ECC79D178738D55DD897E73A
File Size:
1.99 MB, 1991680 bytes
|
|
MD5:
845d1f2b72a8eb6156358c2ce43e9ca8
SHA1:
4d2dfa153c79e8994608374d632f90837130f212
SHA256:
33392ADD18B6DFAD26755FC78BCE38D5B7AA7ADF6215B18F36106623E4A8359F
File Size:
347.14 KB, 347136 bytes
|
|
MD5:
cff80e321288a79c74a1260cd53b5162
SHA1:
5f05942a4d0d98cc52fe29e24e5939fcb7ee8da4
SHA256:
3A0B68C09AC2F5E2254B0BE4D5CC2CB238707DE7E288F69C31DCA4A1B4C3A772
File Size:
347.14 KB, 347136 bytes
|
|
MD5:
be03e046e56f9b5a2e35f5fbef1b10d0
SHA1:
618e200f4973635abd0a2412d0ccba565a350366
SHA256:
07EDDEF8D503A8E72A075A00095B4638516B45EE46BEF7DC1A58533EB9EF5B38
File Size:
184.32 KB, 184320 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have security information
- File has TLS information
- File is .NET application
- File is 32-bit executable
- File is 64-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
Show More
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Company Name | izzy |
| File Description | Stoat |
| File Version |
|
| Internal Name | Stoat |
| Legal Copyright | Copyright (C) 2015 GitHub, Inc. All rights reserved. |
| Original Filename | stoat-desktop.exe |
| Product Name | Stoat |
| Product Version |
|
| Squirrel Aware Version | 1 |
File Traits
- .NET
- CreateThread
- HighEntropy
- No Version Info
- ntdll
- x64
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 70 |
|---|---|
| Potentially Malicious Blocks: | 0 |
| Whitelisted Blocks: | 63 |
| Unknown Blocks: | 7 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Trojan.Downloader.Gen.S
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\downloads\squirrel-unset.log | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Syscall Use |
Show More
|
| User Data Access |
|
| Encryption Used |
|