Adware.Dealply.FB
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 10,330 |
| Threat Level: | 20 % (Normal) |
| Infected Computers: | 2,894 |
| First Seen: | July 24, 2009 |
| Last Seen: | August 21, 2026 |
| OS(es) Affected: | Windows |
The detection of Adware.Dealply.FB on your system indicates the presence of a potentially unwanted program that may be causing unwanted advertisements and potentially collecting user data without consent. Adware, short for advertising-supported software, is a type of software that displays advertisements on your computer, often in the form of pop-ups, banners, or sponsored content. In this report, we will provide an overview of what Adware.Dealply.FB is, how it operates, its symptoms, and most importantly, how to remove it from your system.
Table of Contents
What Is Adware.Dealply.FB?
Adware.Dealply.FB is a type of adware program designed to display unwanted advertisements on a user's computer. The name itself does not specify a known malware family but indicates it is adware-related. Adware programs like Adware.Dealply.FB are often bundled with free software downloads or installed through deceptive means, such as fake updates or infected email attachments. Once installed, adware can significantly disrupt the user experience by displaying unwanted ads, slowing down the system, and potentially collecting user data for targeted advertising.
How Adware.Dealply.FB Operates
Adware.Dealply.FB operates by integrating itself into the system and modifying browser settings or installing additional components that facilitate the display of advertisements. It may also communicate with its command and control servers to report user activity and receive updates or new advertising content. This communication can lead to the collection of user data, which is then used for targeted advertising, potentially infringing on user privacy. The adware may also redirect users to suspicious websites or prompt them to download additional, potentially malicious software.
Symptoms of Infection
Symptoms of Adware.Dealply.FB infection can include an increase in unwanted pop-ups, banners, and sponsored content while browsing the internet. Users may also notice their browsers are redirected to unwanted websites, or they are prompted to download and install additional software. Furthermore, the system may become slower due to the adware consuming system resources to display advertisements and communicate with its servers. In some cases, users might notice changes in their browser settings, such as a new homepage or default search engine, that they did not authorize.
How to Remove Adware.Dealply.FB
- Start your computer in Safe Mode with Networking to prevent Adware.Dealply.FB from loading and to make it easier to remove. This can usually be done by pressing a specific key (such as F8) during boot-up, though this may vary depending on your computer's manufacturer.
- Perform a full scan of your computer using a reputable anti-malware tool, such as SpyHunter. Ensure your anti-malware software is updated to the latest version to improve detection and removal capabilities.
- Uninstall suspicious programs from your computer. Go through the list of installed programs on your computer and uninstall any that you do not recognize or that were installed around the time you first noticed the symptoms of the adware infection.
- Reset your browsers (Chrome, Firefox, Edge, etc.) to their default settings. This can often be done from within the browser's settings menu and will remove any changes made by the adware, such as unwanted extensions or modified homepage and search engine settings.
- After completing the above steps, reboot your computer and perform another scan with your anti-malware software to ensure that Adware.Dealply.FB has been completely removed. Repeat the scanning process until no more threats are detected.
Conclusion
Removing Adware.Dealply.FB from your system requires careful attention to detail and the use of reputable anti-malware tools. By following the steps outlined above, you should be able to successfully remove the adware and restore your system to a clean state. It's also important to practice safe computing habits, such as avoiding suspicious downloads and keeping your software up to date, to prevent future infections. Regularly scanning your system for malware and being cautious with email attachments and links can also help protect against adware and other types of malware. Remember, prevention is key, but with the right tools and knowledge, removal of unwanted programs like Adware.Dealply.FB is entirely possible.
Aliases
3 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Sophos | Troj/Zlobie-Gen |
| Panda | Suspicious file |
| AntiVir | ADSPY/Toolbar.A.2 |
SpyHunter Detects & Remove Adware.Dealply.FB
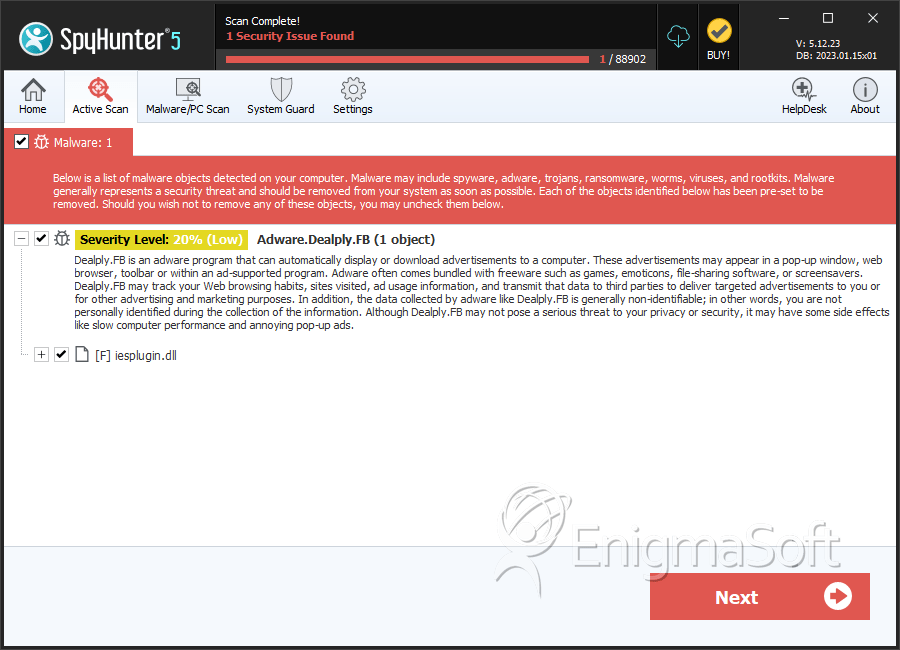
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | iesplugin.dll | 9dbf91dee96498efd8f25fd78ff500e8 | 0 |
Analysis Report
General information
| Family Name: | Adware.Dealply.FB |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
ec304a9f0ac27bf041085f41c9fbdf0e
SHA1:
d7a73fa9e8a7a95e68a4cfd74824ec7a13685671
File Size:
633.86 KB, 633856 bytes
|
|
MD5:
a0a8a8cadeaac08a191081f4b50e9786
SHA1:
cd45b81f10ca3bfc637832158e21e1d1b812ff29
File Size:
291.84 KB, 291840 bytes
|
|
MD5:
5e805c7cb29a3d360ab90c95aeb564e9
SHA1:
62c66f57c8466fdc333a8657f89771a8957f42fe
SHA256:
D00A22ECDBA35D0D8BCFEEE260077F61B95A6004541AA3A38A162A06C222EAB9
File Size:
284.16 KB, 284160 bytes
|
|
MD5:
67c928cee09608f6597dec40437ad732
SHA1:
eb88a24d5787306330f25c097f0242d05fa8aab9
SHA256:
A613E986EAE81872681152F2A2E18F6F14B1210C6E14AA07C26A6ECEC82DB000
File Size:
852.48 KB, 852480 bytes
|
|
MD5:
4cc8a12f4c545923f61bf7497b498344
SHA1:
48ea087dd52918ed861670ef073b4902352a374d
SHA256:
C864224BE6D21867C8A64E6337FF18ED6564831464A72B95D6DFA7DA637CF7A7
File Size:
344.58 KB, 344576 bytes
|
Show More
|
MD5:
5af8006d3313b8ae89e55b06d3e0365c
SHA1:
6980aa8cce72678c2962566953fc58f7742d13a5
SHA256:
EC0A78B2926D915BBA410E5434944340AC1E333D29D6F329E985C6D36AA09184
File Size:
601.09 KB, 601088 bytes
|
|
MD5:
6a808c6aa34674ee845f071ff2b9ffc8
SHA1:
5d969b121b0b95254a4793c594cf643c6ab83f95
SHA256:
A1E3B056025FEA4F47225CC0E0C5EE9B3CE785590F6D939E2EE47D25988ADE11
File Size:
288.26 KB, 288256 bytes
|
|
MD5:
3e5b1cd37314a70d74561f33917534c1
SHA1:
6697cf344a8cc705ae79ec61e3bda41b3a447394
SHA256:
93B1980FB058FF4F2CC6E0B35C34C9A7F0C79265A3D90C37DC05D39B787424A9
File Size:
529.92 KB, 529920 bytes
|
|
MD5:
3eddc5e638324c31be411f95a6118a3b
SHA1:
1696b26c7bc94276d929c1ab570e2e34f54966ce
SHA256:
F87B83C5A8B53778375093573909F8B38872839DEAB571C44572172F198A5247
File Size:
537.09 KB, 537088 bytes
|
|
MD5:
85b322022d29afde8c3d37f55ac80d63
SHA1:
bd27fbcbc913de9076dc8635997118727dbaf08d
SHA256:
8A8E4E0A79E5456769D16DE22F01A0FF7EB73B5D8B5104C3F7A80272FB2132C6
File Size:
365.57 KB, 365568 bytes
|
|
MD5:
24f14bdab325046ac1f74eb42eca7944
SHA1:
15aca6ec11e9a0b02a59e056362f68cfeb22861e
SHA256:
F25F05FF0FF68E037B55721AF582A72842B9F5E278CBD49DFF5FD7D6F882CBA6
File Size:
489.47 KB, 489472 bytes
|
|
MD5:
3fb9232eaf9c0d9b4186127b8d7977c7
SHA1:
5ad8f06fce6a60ba8c9694ec0b703e6dc6e70de6
SHA256:
485B980BB0B9DFF1BE0E32024A4D1F3FDE8927BAC25F12BC92C07A0156E7C9A3
File Size:
177.66 KB, 177664 bytes
|
|
MD5:
238e6141244ed9e62f4f87be71789ada
SHA1:
e43f6956c6f0912d971f46d2cf177e7e1a7ced14
SHA256:
93CAD1F3D7178ECF42D9395D003C025946AF6777CC6609CE8E0A3991B19E1329
File Size:
184.83 KB, 184832 bytes
|
|
MD5:
310f87fc3adb66d83b057aabc1c893e6
SHA1:
e6dc989a7d20e1d38a2823560643622f32b406ea
SHA256:
BFDF29D2A6A2A4A314F107E161C987B045793A5486D9C05E9A0AF85B5AC16C0D
File Size:
288.26 KB, 288256 bytes
|
|
MD5:
cfcbdd5dba75d37d1cc0190c85c9a5eb
SHA1:
9713312e973c2c6d84925be06005d6890ed35f14
SHA256:
F76AE185FCF5A2C5EE0F0CF88C2C45A4DC12007062583DCC199E1C9E14E1CAEE
File Size:
293.89 KB, 293888 bytes
|
|
MD5:
7152db0526aebbfc131d2e12f6b4e1af
SHA1:
97860999bbfd43b1f86a682104f9791b5e35e0a8
SHA256:
F58B77EF1DF8D9F979F9D2D5316F3C7B9EAA1C0813ABCC0007C963B36853328B
File Size:
496.13 KB, 496128 bytes
|
|
MD5:
6c3009481b244cb8f0e7a698b526d3cc
SHA1:
5637649d51635b0cb02d2a2d0420e59155f1413c
SHA256:
B4CABBC97D1569051BFFE226F97B0603628EA366F775408C5044B02B71B8A8BE
File Size:
481.79 KB, 481792 bytes
|
|
MD5:
4699e62166414338064330b3b071fc96
SHA1:
d529bdca4d7ff38aac21fc12b893cda2fba5e631
SHA256:
2363A44033E17E40B12800496333D15356514A65316627AAB166056F9D1FBE1A
File Size:
373.25 KB, 373248 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has been packed
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
Show More
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Company Name |
|
| File Description |
|
| File Version |
|
| Internal Name |
|
| Legal Copyright |
|
| Legal Trademarks |
|
| Original Filename |
|
| Product Name |
|
| Product Version |
|
File Traits
- HighEntropy
- No Version Info
- packed
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 1,811 |
|---|---|
| Potentially Malicious Blocks: | 3 |
| Whitelisted Blocks: | 1,796 |
| Unknown Blocks: | 12 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Agent.HJG
- BadJoke.RSA
- BadJoke.TH
- BadJoke.XA
- Banker.GF
Show More
- Banload.NB
- Banload.XA
- Banload.XN
- Banload.XR
- Banload.XT
- Gamehack.PDFA
- Injector.DFF
- Injector.FGGA
- Injector.FHBA
- Injector.GDSA
- Injector.KFE
- Injector.KS
- Kagee.A
- Lamer.B
- Nanobot.MB
- Proleeg.A
- ScriptExpert.A
- Sirefef.X
- Trojan.Downloader.Gen.FD
- Trojan.Downloader.Gen.KL
- Trojan.Downloader.Gen.MK
- Trojan.Filecoder.Gen.BM
- Trojan.Injector.Gen.IDM
- Trojan.Kryptik.Gen.FJ
- Trojan.Kryptik.Gen.GOE
- Trojan.Kryptik.Gen.MM
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| \device\namedpipe\gmdasllogger | Generic Write,Read Attributes |
| c:\users\user\appdata\local\microsoft\windows\usrclass.dat{dba6b5ef-640a-11ed-9bcb-f677369d361c}.txr.0.regtrans-ms | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\microsoft\windows\usrclass.dat{dba6b5ef-640a-11ed-9bcb-f677369d361c}.txr.1.regtrans-ms | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\microsoft\windows\usrclass.dat{dba6b5ef-640a-11ed-9bcb-f677369d361c}.txr.2.regtrans-ms | Generic Read,Write Data,Write Attributes,Write extended,Append data |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Anti Debug |
|
| User Data Access |
|