Trojan.Stealer
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 6,668 |
| Threat Level: | 80 % (High) |
| Infected Computers: | 24,473 |
| First Seen: | May 24, 2012 |
| Last Seen: | September 10, 2026 |
| OS(es) Affected: | Windows |
The detection of Trojan.Stealer on your system indicates a potential security threat that requires immediate attention. This type of malware is designed to compromise your computer's security and steal sensitive information, making it essential to understand its nature and take prompt action to remove it.
Table of Contents
What Is Trojan.Stealer?
Trojan.Stealer is a type of malware that falls under the broader category of Trojans, which are malicious programs that disguise themselves as legitimate software. The primary goal of Trojan.Stealer is to infiltrate your system and gather sensitive data, such as login credentials, financial information, or personal details, without your knowledge or consent. This malware can be particularly dangerous because it can lead to identity theft, financial loss, and unauthorized access to your computer and online accounts.
How Trojan.Stealer Operates
Trojan.Stealer operates by exploiting vulnerabilities in your system's security or by deceiving you into installing it voluntarily. Once installed, it can communicate with its command and control servers to receive instructions and transmit stolen data. This malware can also install additional malicious components, modify system settings, and disrupt the normal functioning of your computer. Its stealthy nature makes it challenging to detect without the aid of antivirus software or other security tools.
Symptoms of Infection
Identifying a Trojan.Stealer infection can be difficult, as it often runs in the background without visible symptoms. However, you might notice unusual system behavior, such as slow performance, frequent crashes, or unexpected pop-ups and advertisements. Additionally, you might observe unauthorized changes to your system settings, suspicious network activity, or unexplained data usage. If you suspect that your system has been compromised, it's crucial to take immediate action to mitigate the damage.
How to Remove Trojan.Stealer
- Boot your computer in Safe Mode with Networking to prevent the malware from loading and to allow for internet access. This will make it easier to download and install removal tools.
- Download and install a reputable anti-malware tool, such as SpyHunter, which can detect and remove Trojan.Stealer and other malicious software. Perform a full scan of your system to identify all infected files and components.
- Uninstall any suspicious programs or applications that you don't recognize or that were installed around the time the malware was detected. Be cautious and only remove programs that you are certain are malicious or unnecessary.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings. This can help remove any malicious extensions or settings that the malware might have installed.
- Reboot your computer and perform another full scan with your anti-malware tool to ensure that all remnants of the malware have been removed. This step is crucial to confirm that your system is clean and secure.
Conclusion
Removing Trojan.Stealer from your system requires careful and systematic steps to ensure that all components of the malware are eliminated. By following the guidance provided and using reputable security tools, you can restore your system's security and protect your sensitive information from theft. Remember, prevention is key; always be cautious when downloading software, opening email attachments, or clicking on links from unknown sources to minimize the risk of future infections.
SpyHunter Detects & Remove Trojan.Stealer
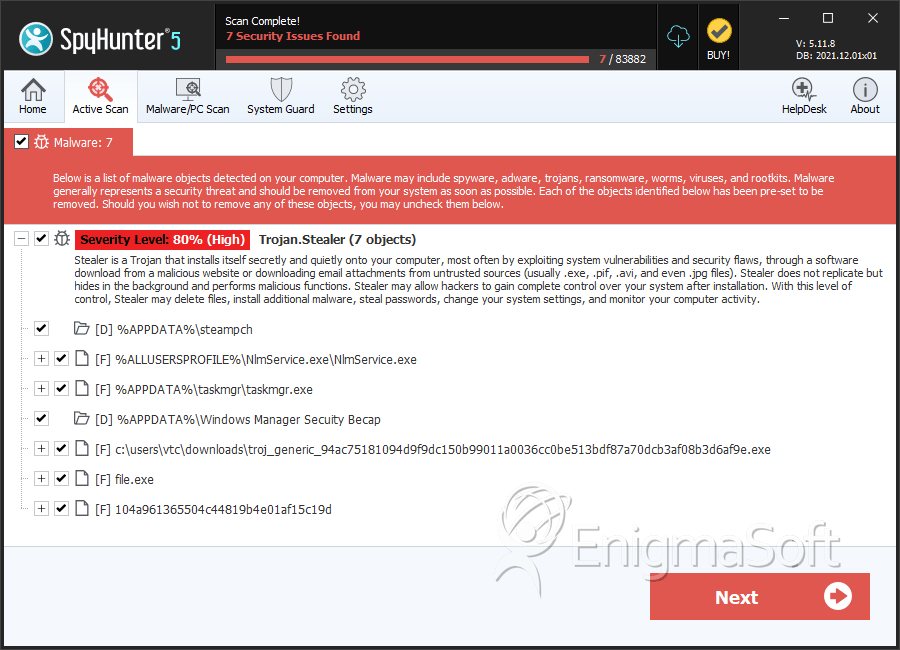
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | taskmgr.exe | f6f44d774e1cdeb8ff75c6314a99d548 | 465 |
| 2. | NlmService.exe | 1b440d416103418759155fbdbd314721 | 39 |
| 3. | troj_generic_94ac75181094d9f9dc150b99011a0036cc0be513bdf87a70dcb3af08b3d6af9e.exe | 8015e25459aa214bcd1697ab722a7ec9 | 1 |
| 4. | file.exe | 1a6455ff63137466cf365df239a43901 | 0 |
| 5. | 104a961365504c44819b4e01af15c19d | 104a961365504c44819b4e01af15c19d | 0 |
Registry Details
Directories
Trojan.Stealer may create the following directory or directories:
| %APPDATA%\Windows Manager Secuity Becap |
| %APPDATA%\steampch |
Analysis Report
General information
| Family Name: | Trojan.Stealer |
|---|---|
| Packers: | UPX! |
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
21858b4cb2dcb0fc005bb4221af6d1d5
SHA1:
822035faa84c50a4d22925dda183d395908333ed
SHA256:
1CC831645D2D6C7E87962E9D8EE0C697A6E60277ACFC71C10F5FA7501881C42D
File Size:
189.10 KB, 189096 bytes
|
|
MD5:
6203a9caa5ecb581227c43c194c5a2c7
SHA1:
a8958001961665b99b6c35a16eb81bf2ef672875
SHA256:
9586520FC101D730A127361E16C46DF9EBF62B93B5C92A57DF7403460136CCA9
File Size:
83.97 KB, 83968 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have security information
- File has been packed
- File has exports table
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | http://www.bpsoft.com |
| Company Name | BreakPoint Software, Inc. |
| File Description | bpsregwd.dll |
| File Version |
|
| Internal Name | bpsregwd |
| Legal Copyright |
|
| Original Filename | bpsregwd.dll |
| Product Name | bpsregwd |
| Product Version |
|
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| BreakPoint Software, Inc. | Thawte Code Signing CA | Hash Mismatch |
File Traits
- dll
- HighEntropy
- packed
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 843 |
|---|---|
| Potentially Malicious Blocks: | 0 |
| Whitelisted Blocks: | 807 |
| Unknown Blocks: | 36 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Syscall Use |
Show More
|
| Process Manipulation Evasion |
|
| Process Shell Execute |
|
| Anti Debug |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\822035faa84c50a4d22925dda183d395908333ed_0000189096.,LiQMAxHB
|
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\a8958001961665b99b6c35a16eb81bf2ef672875_0000083968.,LiQMAxHB
|


