System hijack!
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 90 % (High) |
| Infected Computers: | 0 |
| First Seen: | July 24, 2009 |
| OS(es) Affected: | Windows |
'System hijack!' is a fake pop-up warning message that is displayed on an infected machine by the rogueware called XP Antispyware 2010. 'System hijack!' pops up from the Windows task bar and displays a message claiming that the system is infected and in need of a solution in the form of rogueware. If displayed on your PC, do not believe the fake 'System hijack!' pop-up warning and have your PC scanned for malware.
Table of Contents
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Sunbelt | BehavesLike.Win32.Malware (v) |
| Sophos | Sus/Behav-1021 |
| Panda | Trj/CI.A |
| McAfee-GW-Edition | Heuristic.BehavesLike.Win32.Downloader.A |
| McAfee | Suspect-02!51FDB6F5CFD6 |
| BitDefender | Generic.Malware.SFMg.6A9CD88F |
| TrendMicro | TROJ_DNSCHANG.GH |
| Symantec | Trojan.Zlob |
| Sophos | Mal/Generic-A |
| Panda | Trj/DNSChanger.NY |
| NOD32 | Win32/TrojanDownloader.Agent.OAW |
| McAfee-GW-Edition | Trojan.Spy.Agent.dcp.1 |
| McAfee | FakeAlert-D.dldr |
| Ikarus | Trojan.Win32.DNSChanger |
| Fortinet | Heuri.D!tr.dldr |
SpyHunter Detects & Remove System hijack!
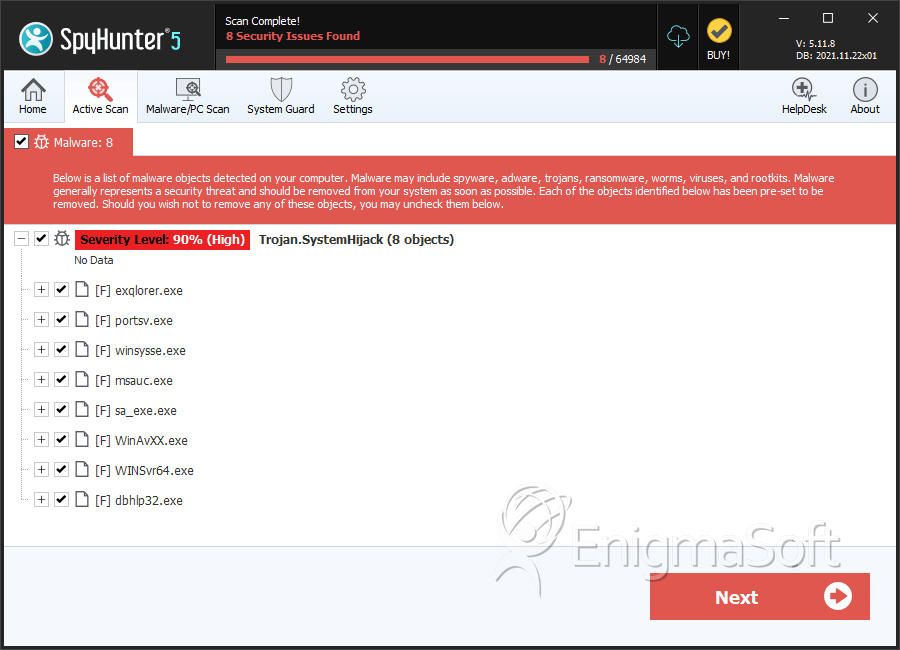
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | exqlorer.exe | 51fdb6f5cfd621e031f930588a49218d | 0 |
| 2. | portsv.exe | 1475039797dc40bd2d7f10ac7ac3187f | 0 |
| 3. | winsysse.exe | db5987e5705c595b8636297a0dbad864 | 0 |
| 4. | msauc.exe | 831f67dd7419482811737da8a2867423 | 0 |
| 5. | sa_exe.exe | 906a8b50c8b0be2a914fedbb10ce6d90 | 0 |
| 6. | WinAvXX.exe | 1ef1058dfb0a196270f3d3ac45d7afce | 0 |
| 7. | dbhlp32.exe | 0fee31a4d5a306f99e4c3200a5627868 | 0 |
| 8. | huifitc.exe | b51530cc316b1a0ce24f4f9627a0083e | 0 |
| 9. | anistio.exE | ee54bde18ce2aab9ffc6ca91ee0ab91c | 0 |
| 10. | WINSvr64.exe | 8f206fc7911654c972195236fe3855cf | 0 |
| 11. | regsv.exe | 28cfa16ce39187fbef8163e32dc52834 | 0 |
| 12. | netcomms.exe | 581e38c2dda4546ed6ce9fcc12b65e7e | 0 |
| 13. | nsysrunex.exe | 7df180908d31265bd158efa0c778b0f0 | 0 |
| 14. | daudi.exe | 5a6f0ca8e39dce64b366c220d01cce7d | 0 |
| 15. | mciservice.exe | 16452b5329a97431e62a26f1a298d005 | 0 |


