PUP.RemoveIT Pro
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 11 |
| First Seen: | March 27, 2019 |
| Last Seen: | March 1, 2026 |
| OS(es) Affected: | Windows |
The detection of PUP.RemoveIT Pro on your system indicates the presence of a potentially unwanted program (PUP) that may be causing issues with your computer's performance and security. It's essential to understand what this detection means and how to properly remove the threat to prevent further problems.
Table of Contents
What Is PUP.RemoveIT Pro?
PUP.RemoveIT Pro is a type of potentially unwanted program that may have been installed on your system without your knowledge or consent. PUPs are software applications that may not be malicious in nature but can still cause problems, such as displaying unwanted advertisements, collecting user data, or modifying system settings. The name PUP.RemoveIT Pro suggests that it may be related to a program that claims to provide removal or protection services, but its actual behavior may be different from its advertised purpose.
How PUP.RemoveIT Pro Operates
Once installed, PUP.RemoveIT Pro may operate in various ways, including running background processes, modifying system files, or interacting with other software applications. It may also communicate with remote servers to send or receive data, which could potentially compromise your system's security. PUPs like PUP.RemoveIT Pro can be challenging to detect and remove, as they may not exhibit obvious malicious behavior and may be disguised as legitimate programs.
Symptoms of Infection
If your system is infected with PUP.RemoveIT Pro, you may notice various symptoms, including unwanted pop-ups or advertisements, slower system performance, or unexpected changes to your browser settings or homepage. You may also experience issues with other software applications or system crashes. However, some PUPs can remain dormant or hide their activities, making it difficult to detect their presence without proper scanning and detection tools.
How to Remove PUP.RemoveIT Pro
To remove PUP.RemoveIT Pro from your system, follow these steps:
- Boot your system in Safe Mode with Networking to prevent the PUP from loading and to allow for internet access.
- Run a full scan using a reputable anti-malware tool, such as SpyHunter, to detect and remove all related files and components.
- Uninstall any suspicious programs or applications that may be related to PUP.RemoveIT Pro.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any modifications made by the PUP.
- Reboot your system and run another scan to ensure that all remnants of PUP.RemoveIT Pro have been removed.
It's crucial to be thorough and patient during the removal process to ensure that all components of the PUP are eliminated.
Conclusion
The detection of PUP.RemoveIT Pro on your system is a serious issue that requires prompt attention. By understanding what this detection means and following the proper removal steps, you can help protect your system from potential security risks and performance issues. Remember to always be cautious when installing software applications, and make sure to use reputable anti-malware tools to scan your system regularly. By taking these precautions, you can help keep your system safe and secure.
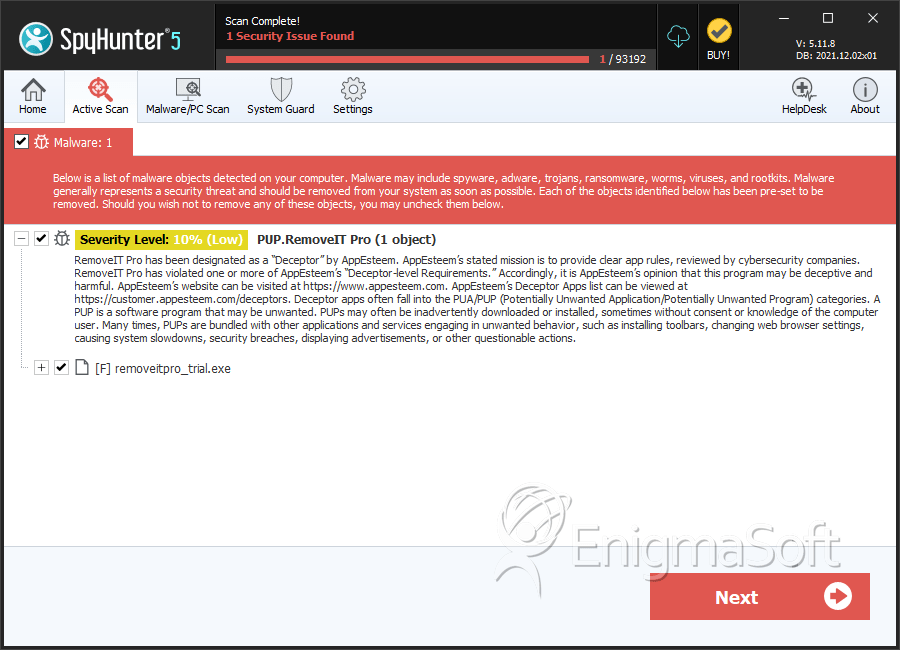
SpyHunter Detects & Remove PUP.RemoveIT Pro
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | removeitpro_trial.exe | dea0949a2d65189e059f5360e58e26b9 | 0 |
Analysis Report
General information
| Family Name: | PUP.RemoveIT Pro |
|---|---|
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
8c09b5fa6465d028d267ef1d6316b567
SHA1:
b2b07f46c110ca2915e6dde0fa9765ac3967ab60
SHA256:
9F483E88806DF7D7E40AD66358DEFA0C469F53ADBAF38D954E9D9C47720A2623
File Size:
5.72 MB, 5718032 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup. |
| Company Name | InCode Solutions |
| File Description | Installation |
| Legal Copyright | InCode Solutions |
| Product Version | 16.18 |
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Damjan Irgolic | COMODO RSA Code Signing CA | Self Signed |
| Damjan Irgolic | COMODO RSA Code Signing CA | Self Signed |