PUP.Plumbytes Anti-Malware
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 13,589 |
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 7,684 |
| First Seen: | March 27, 2019 |
| Last Seen: | September 21, 2026 |
| OS(es) Affected: | Windows |
The detection of PUP.Plumbytes Anti-Malware on your system indicates the presence of a potentially unwanted program (PUP) that may be causing issues with your computer's performance and security. It is essential to understand the nature of this threat and take necessary steps to remove it to prevent any potential harm.
Table of Contents
What Is PUP.Plumbytes Anti-Malware?
PUP.Plumbytes Anti-Malware is a type of potentially unwanted program that may have been installed on your system without your knowledge or consent. This type of software is often bundled with other programs or downloaded from untrusted sources, and it can cause a range of problems, including slowing down your computer, displaying unwanted advertisements, and potentially compromising your personal data.
How PUP.Plumbytes Anti-Malware Operates
PUPs like PUP.Plumbytes Anti-Malware typically operate by installing themselves on your system and then running in the background, often without your knowledge or consent. They may collect data about your browsing habits, search history, and other personal information, which can be used for targeted advertising or other malicious purposes. In some cases, PUPs may also install additional software or malware on your system, which can further compromise your security and performance.
Symptoms of Infection
If your system is infected with PUP.Plumbytes Anti-Malware, you may notice a range of symptoms, including slow system performance, unwanted advertisements or pop-ups, and unexpected changes to your browser settings or homepage. You may also notice that your system is running more slowly than usual, or that your browser is crashing or freezing frequently. In some cases, you may also receive fake alerts or warnings about supposed security threats on your system, which are actually just attempts to scare you into purchasing unnecessary software or services.
How to Remove PUP.Plumbytes Anti-Malware
- Boot your system in Safe Mode with Networking to prevent the PUP from running and to allow you to remove it more easily.
- Run a full scan of your system using a reputable anti-malware tool, such as SpyHunter, to detect and remove any malicious software that may be present.
- Uninstall any suspicious programs or software that you do not recognize or that you did not intentionally install.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any changes that the PUP may have made.
- Reboot your system and run another scan with your anti-malware tool to ensure that the PUP has been completely removed.
Conclusion
Removing PUP.Plumbytes Anti-Malware from your system is an essential step in protecting your security and performance. By following the steps outlined above, you can help to ensure that your system is free from this potentially unwanted program and any other malicious software that may be present. It is also important to be vigilant when downloading software and to always read the terms and conditions carefully to avoid installing unwanted programs in the future. By taking these precautions, you can help to keep your system safe and secure.
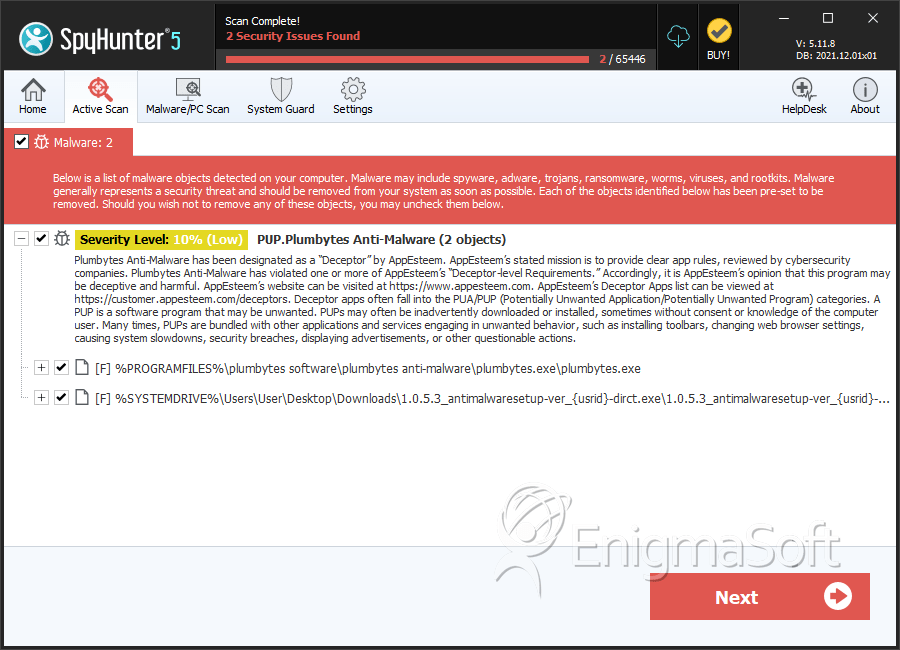
SpyHunter Detects & Remove PUP.Plumbytes Anti-Malware
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | plumbytes.exe | 1f26138424b1635b1a47254168a162fb | 5,383 |
| 2. | 1.0.5.3_antimalwaresetup-ver_{usrid}-dirct.exe | 7e9b5f41d8478c9897631b72b1af2666 | 79 |
Analysis Report
General information
| Family Name: | PUP.Plumbytes Anti-Malware |
|---|---|
| Packers: | UPX! |
| Signature status: | Modified signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
96f16e7a948339e38905e07c84fc1d52
SHA1:
5e0a5e78fbe876e6df0d0662fdee738db63ff965
SHA256:
D633A1CF7900F400D235765FBE91CEB758C8DD7798286DF9EDCB57B45CB69030
File Size:
881.90 KB, 881904 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have relocations information
- File doesn't have security information
- File has been packed
- File has exports table
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
Show More
- File is Native application (NOT .NET application)
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Company Name | Plumbytes Software |
| File Description | Plumbytes Anti-Malware |
| File Version | 1.0.2.0 |
| Internal Name | Plumbytes Anti-Malware |
| Product Name | Plumbytes Anti-Malware |
| Product Version | 1.0.2.0 |
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 7,049 |
|---|---|
| Potentially Malicious Blocks: | 2 |
| Whitelisted Blocks: | 7,026 |
| Unknown Blocks: | 21 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Agent.DSS
- Banload.XH
- Banload.XJ
- Delf.OD
- Injector.JDA
Show More
- Vadokrist.B