PUP.DriverToolkit
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 4,004 |
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 138,754 |
| First Seen: | March 27, 2019 |
| Last Seen: | October 5, 2026 |
| OS(es) Affected: | Windows |
The detection of PUP.DriverToolkit on your system indicates the presence of a potentially unwanted program (PUP) that may be causing issues with your computer's performance and security. It's essential to understand the nature of this threat and take immediate action to remove it to prevent further problems.
Table of Contents
What Is PUP.DriverToolkit?
PUP.DriverToolkit is a type of malware that is categorized as a potentially unwanted program. This means it is not necessarily malicious in nature but can still cause problems for your system. PUPs are often installed unintentionally by users, usually through bundled software downloads or misleading advertisements. They can consume system resources, display unwanted advertisements, and potentially collect user data without consent.
How PUP.DriverToolkit Operates
PUP.DriverToolkit, like other PUPs, operates by integrating itself into your system, often through legitimate-looking software installations or updates. Once installed, it can start performing various unwanted actions, such as displaying pop-up advertisements, changing browser settings, or running background processes that consume system resources. The primary goal of such programs is usually to generate revenue for their creators through advertising or data collection.
Symptoms of Infection
Symptoms of a PUP.DriverToolkit infection can vary but commonly include an increase in unwanted advertisements, unexpected changes to browser settings or homepage, slow system performance, and the presence of unfamiliar programs or toolbars in your browser or desktop. If you've noticed any of these symptoms, it's crucial to take action to remove the PUP and restore your system to a clean state.
- Increased number of pop-ups or unwanted advertisements
- Changes to your browser's homepage or search engine without your consent
- Slowdown in system performance or frequent crashes
- Appearance of unfamiliar toolbars or programs
How to Remove PUP.DriverToolkit
- Enter Safe Mode with Networking to limit the PUP's ability to interfere with the removal process.
- Perform a full scan of your system using a reputable anti-malware tool, such as SpyHunter, to detect and remove all components of the PUP.
- Uninstall any suspicious programs or applications that were installed around the time the symptoms started.
- Reset your browsers (Chrome, Firefox, Edge) to their default settings to remove any changes made by the PUP.
- Reboot your system and perform another scan with your anti-malware tool to ensure all remnants of the PUP have been removed.
Conclusion
Removing PUP.DriverToolkit from your system is crucial to restoring your computer's performance and securing your personal data. By following the steps outlined above, you can effectively remove this potentially unwanted program and prevent future infections by being more cautious with software downloads and regularly scanning your system for malware. Remember, vigilance and the use of reputable security software are key to maintaining a clean and secure computing environment.
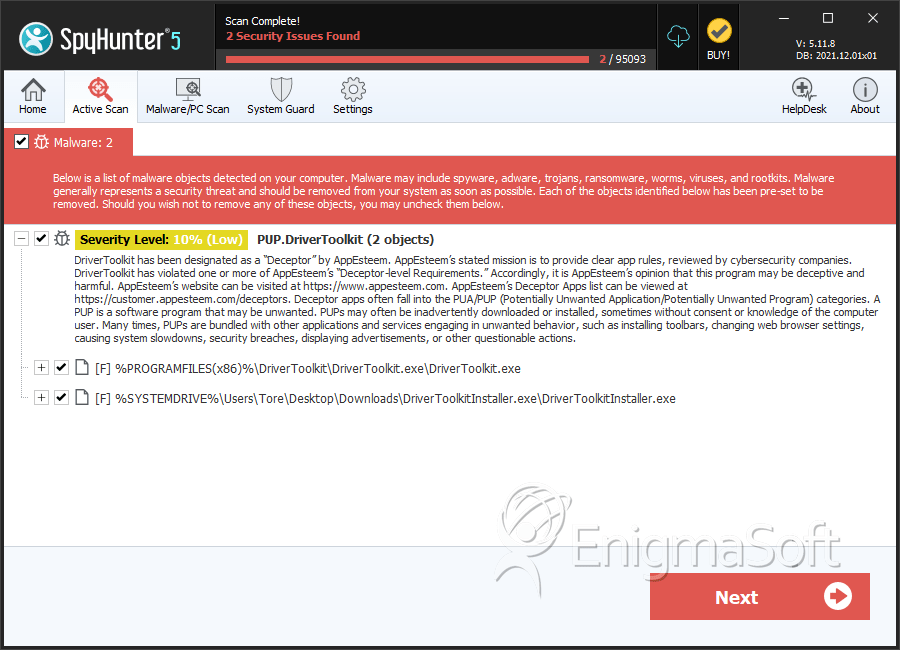
SpyHunter Detects & Remove PUP.DriverToolkit
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | DriverToolkit.exe | b35bcdc8758f44bb092590d92a8e744c | 88,782 |
| 2. | DriverToolkitInstaller.exe | b3df5478760ced4d30910eb8e8b594e2 | 235 |
Analysis Report
General information
| Family Name: | PUP.DriverToolkit |
|---|---|
| Signature status: | Hash Mismatch |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
f5c14b9ad6a9dcf7dc1eb764a6acfe2b
SHA1:
f9c250d70f77fd3f90c0df48fb3eaa27abac09ab
SHA256:
676B5BE997C9E1CABFFDB8DE82B3E58729BFFF90CEA13475D63484A1F397B2A2
File Size:
2.46 MB, 2459530 bytes
|
|
MD5:
fe22a63802f50519964016c03b0864fc
SHA1:
40b57467f18240994ae9d2d4052176eee355a17f
SHA256:
CCF933D199087A469DAD4BE7B90091353EC427BDB0816BEC7F5580DE67305CDE
File Size:
2.46 MB, 2459531 bytes
|
|
MD5:
e09f633164f7897ba39b64b82deb1ac7
SHA1:
1968eb54a2262e25b342aa6e853418d04cc6751c
SHA256:
98C7862FE3158A9FE4EC86E8731829AD785044211CF5E340DECF1F57A6F71D12
File Size:
2.46 MB, 2459530 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup. |
| Company Name | Megaify Software |
| File Description | DriverToolkit Setup |
| File Version | 8.5.1 |
| Product Name | DriverToolkit |
| Product Version | 8.5.1.0 |
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Megaify Software Co.,Ltd. | Symantec Class 3 SHA256 Code Signing CA | Hash Mismatch |
| Megaify Software Co.,Ltd. | Symantec Class 3 SHA256 Code Signing CA | Hash Mismatch |
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\is-1ph83.tmp\_isetup\_setup64.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\is-55i76.tmp\_isetup\_setup64.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\is-62k0b.tmp\f9c250d70f77fd3f90c0df48fb3eaa27abac09ab_0002459530.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\is-83ul6.tmp\_isetup\_setup64.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\is-fbs47.tmp\40b57467f18240994ae9d2d4052176eee355a17f_0002459531.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\is-v7ub3.tmp\1968eb54a2262e25b342aa6e853418d04cc6751c_0002459530.tmp | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Process Shell Execute |
|
| User Data Access |
|
| Keyboard Access |
|
| Process Manipulation Evasion |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
"C:\Users\Okpvlztc\AppData\Local\Temp\is-62K0B.tmp\f9c250d70f77fd3f90c0df48fb3eaa27abac09ab_0002459530.tmp" /SL5="$40040,2034499,136192,c:\users\user\downloads\f9c250d70f77fd3f90c0df48fb3eaa27abac09ab_0002459530"
|
"C:\Users\Pqkmpnpy\AppData\Local\Temp\is-FBS47.tmp\40b57467f18240994ae9d2d4052176eee355a17f_0002459531.tmp" /SL5="$1202BE,2034499,136192,c:\users\user\downloads\40b57467f18240994ae9d2d4052176eee355a17f_0002459531"
|
"C:\Users\Gbopgkjx\AppData\Local\Temp\is-V7UB3.tmp\1968eb54a2262e25b342aa6e853418d04cc6751c_0002459530.tmp" /SL5="$E03DE,2034499,136192,c:\users\user\downloads\1968eb54a2262e25b342aa6e853418d04cc6751c_0002459530"
|


