PUP.DriverHive
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 277 |
| First Seen: | March 27, 2019 |
| Last Seen: | February 25, 2026 |
| OS(es) Affected: | Windows |
The detection of PUP.DriverHive on your system indicates the presence of a potentially unwanted program (PUP) that may be causing issues with your computer's performance and security. It's essential to understand the nature of this threat and take immediate action to remove it and prevent further damage.
Table of Contents
What Is PUP.DriverHive?
PUP.DriverHive is a type of malware that is classified as a potentially unwanted program. This means that it is not necessarily a virus or a Trojan, but rather a program that may be installed on your system without your knowledge or consent. PUPs can be bundled with other software, downloaded from the internet, or installed through exploit kits. They often have legitimate-looking interfaces and may claim to provide useful functions, but in reality, they can cause a range of problems, including slowing down your system, displaying unwanted advertisements, and collecting your personal data.
How PUP.DriverHive Operates
PUP.DriverHive operates by installing itself on your system and then executing its payload. This can happen through various means, such as drive-by downloads, infected software installations, or phishing attacks. Once installed, the PUP can start collecting your data, displaying ads, and slowing down your system. It may also install additional malware or PUPs, creating a complex network of unwanted programs that can be difficult to remove. PUP.DriverHive may also use rootkit techniques to hide its presence and evade detection by security software.
Symptoms of Infection
The symptoms of a PUP.DriverHive infection can vary, but common signs include slow system performance, unwanted advertisements and pop-ups, unfamiliar programs and icons on your desktop, and changes to your browser settings and homepage. You may also notice that your system is crashing or freezing frequently, or that your personal data is being collected and transmitted to unknown servers. If you suspect that your system is infected with PUP.DriverHive, it's essential to take immediate action to remove it and prevent further damage.
How to Remove PUP.DriverHive
- Boot your system in Safe Mode with Networking to prevent the PUP from loading and to allow you to download and install removal tools.
- Download and install a reputable anti-malware tool, such as SpyHunter, and perform a full scan of your system to detect and remove PUP.DriverHive and any other malware that may be present.
- Uninstall any suspicious programs that you don't recognize or that you didn't install intentionally. Be cautious when uninstalling programs, as some may be legitimate or required by your system.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any unwanted extensions or add-ons that may be associated with PUP.DriverHive.
- Reboot your system and perform another scan with your anti-malware tool to ensure that PUP.DriverHive and any other malware have been completely removed.
Conclusion
Removing PUP.DriverHive from your system requires careful attention to detail and a thorough understanding of the removal process. By following the steps outlined above, you can help ensure that your system is free from this potentially unwanted program and any other malware that may be present. Remember to always be cautious when downloading and installing software, and to keep your security software up to date to prevent future infections. If you're unsure about any aspect of the removal process, consider seeking the help of a professional or contacting a reputable security vendor for assistance.
SpyHunter Detects & Remove PUP.DriverHive
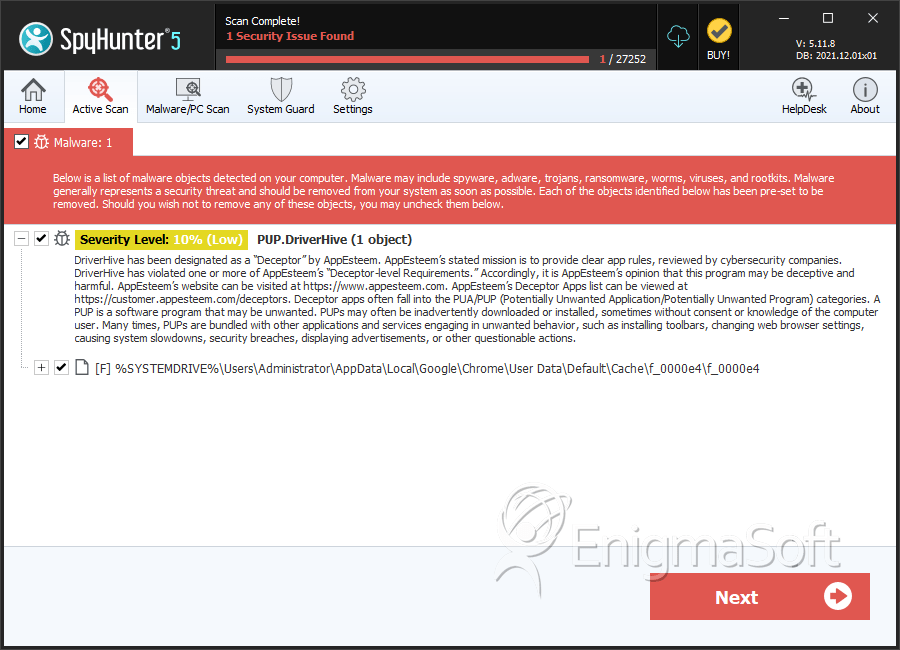
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | f_0000e4 | a85d2642966186d0769963ce46d6b7ae | 132 |
Analysis Report
General information
| Family Name: | PUP.DriverHive |
|---|---|
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
af2a804f19038e58a2d80aaaa8a92828
SHA1:
a1ea52bc96448f7cc92625a81aca1af00098d05c
SHA256:
BBC025BE0479ADDC8C6AC4A94F59802E002264994B24C65B1F63E6AED05CF114
File Size:
4.69 MB, 4687176 bytes
|
|
MD5:
1b01940fb09addbb848b914868068970
SHA1:
64a69f677bfc092719024db62cf36022995497cd
SHA256:
0E5E78A2240EC181D547F573E6D25F6D03377E10F7EF5B9F816CEBAF7E37235A
File Size:
9.85 MB, 9854504 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File has exports table
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
Show More
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup. |
| Company Name |
|
| File Description |
|
| File Version |
|
| Legal Copyright |
|
| Legal Trademarks | DriverHive is a trademark of Bootstrap Development, LLC. |
| Original Filename | DriverHive.exe |
| Product Name |
|
| Product Version |
|
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Bootstrap Development, LLC | Go Daddy Secure Certification Authority | Self Signed |
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\is-mjbdp.tmp\64a69f677bfc092719024db62cf36022995497cd_0009854504.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\roaming\bsd\driverhive\logs\driverhive.log | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\windows\win.ini | Generic Read,Write Data,Write Attributes,Write extended,Append data |
Registry Modifications
Registry Modifications
This section lists registry keys and values that were created, modified and/or deleted by samples in this family. Windows Registry activity can provide valuable insight into malware functionality. Additionally, malware often creates registry values to allow itself to automatically start and indefinitely persist after an initial infection has compromised the system.| Key::Value | Data | API Name |
|---|---|---|
| HKLM\software\wow6432node\bsd\driverhive::driverignorelist | RegNtPreCreateKey | |
| HKLM\software\wow6432node\bsd\driverhive::driveruploadlist | RegNtPreCreateKey |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Network Winsock2 |
|
| Anti Debug |
|
| User Data Access |
|
| Process Manipulation Evasion |
|
| Process Shell Execute |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
"C:\Users\Brzswfpi\AppData\Local\Temp\is-MJBDP.tmp\64a69f677bfc092719024db62cf36022995497cd_0009854504.tmp" /SL5="$50328,9538741,95744,c:\users\user\downloads\64a69f677bfc092719024db62cf36022995497cd_0009854504"
|


