PUP.DownloadMaster
The detection of PUP.DownloadMaster on your system indicates the presence of a potentially unwanted program (PUP) that may be causing issues with your computer's performance and security. It's essential to understand the nature of this threat and take appropriate steps to remove it to prevent potential harm.
Table of Contents
What Is PUP.DownloadMaster?
PUP.DownloadMaster is a type of potentially unwanted program that can be installed on your computer without your knowledge or consent. It may be bundled with other software or downloaded from the internet, often through deceptive or misleading means. PUPs like PUP.DownloadMaster can cause a range of problems, including slowing down your computer, displaying unwanted advertisements, and potentially exposing your personal data to risk.
How PUP.DownloadMaster Operates
PUPs like PUP.DownloadMaster typically operate by installing themselves on your computer and then running in the background, often without your knowledge or consent. They may collect data about your browsing habits, search history, and other online activities, which can be used to display targeted advertisements or sold to third-party companies. In some cases, PUPs can also download and install additional malware or unwanted software on your computer, further compromising your security.
Symptoms of Infection
If your computer is infected with PUP.DownloadMaster, you may notice a range of symptoms, including slowed performance, unwanted advertisements or pop-ups, and changes to your browser settings or homepage. You may also notice that your computer is running more slowly than usual, or that your internet connection is being used for unknown purposes. In some cases, you may not notice any symptoms at all, which is why it's essential to run regular virus scans and monitor your computer's behavior closely.
How to Remove PUP.DownloadMaster
- Boot your computer in Safe Mode with Networking to prevent PUP.DownloadMaster from running and interfering with the removal process.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your computer and detect any malware or unwanted software that may be present.
- Uninstall any suspicious programs or software that you don't recognize or no longer need, as these may be related to the PUP.DownloadMaster infection.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any changes made by the PUP.
- Reboot your computer and run another scan with your anti-malware tool to ensure that the PUP.DownloadMaster has been completely removed.
Conclusion
Removing PUP.DownloadMaster from your computer is an essential step in protecting your security and preventing potential harm. By following the steps outlined above and taking proactive measures to protect your computer, you can help to prevent future infections and keep your personal data safe. Remember to always be cautious when downloading software or clicking on links from unknown sources, and to run regular virus scans to detect and remove any malware or unwanted programs that may be present on your computer.
SpyHunter Detects & Remove PUP.DownloadMaster
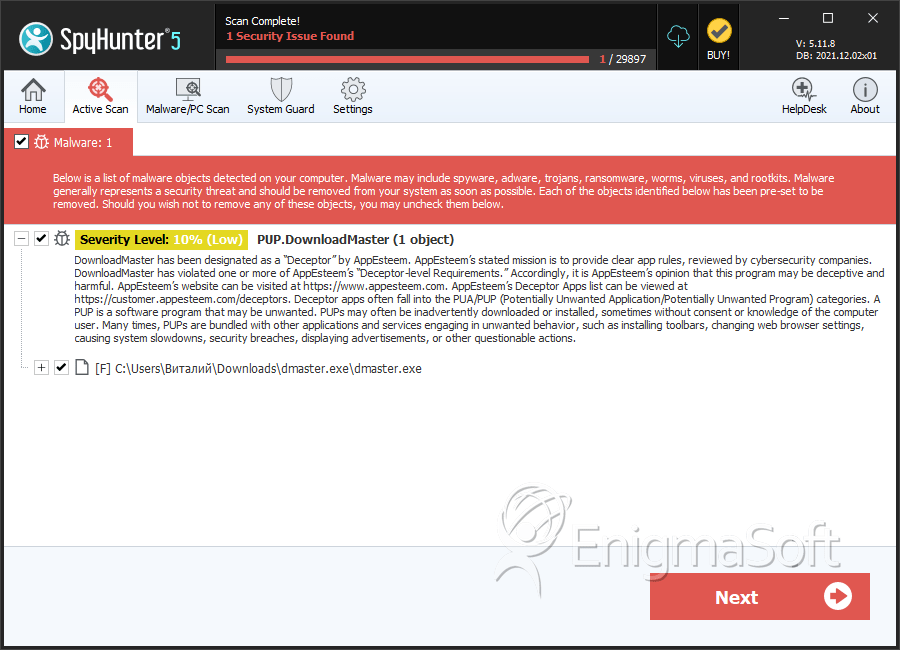
Analysis Report
General information
| Family Name: | PUP.DownloadMaster |
|---|---|
| Signature status: | Root Not Trusted |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
25fd5bbdd27f6a73b59ae99067d4fb9e
SHA1:
6539d3f0727c1c58882f5879df3ca986e6ac8244
SHA256:
23A1056BE6EE8FA1565A7BA07D9DD312C714B38475D96D2516B5A307BCEC09DE
File Size:
5.25 MB, 5246360 bytes
|
|
MD5:
ba05c62d7b779eee1abc5a920061a447
SHA1:
2b89771062d8bfe39b6d5db8241f7fae4375e3ab
SHA256:
4E081A1C493FDD479015FEDB2AE2EEBB831F770FF81547C9F4D01E61A377BA6B
File Size:
3.21 MB, 3211384 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have relocations information
- File has exports table
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup. |
| Company Name | WestByte |
| File Description |
|
| File Version |
|
| Legal Copyright |
|
| Product Name | Internet Download Accelerator |
| Product Version |
|
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Download Master | Sectigo Public Code Signing Root R46 | Root Not Trusted |
File Traits
- 2+ executable sections
- dll
- HighEntropy
- Inno
- InnoSetup Installer
- Installer Manifest
- Installer Version
- packed
- upx
- UPX!
Show More
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 7,700 |
|---|---|
| Potentially Malicious Blocks: | 0 |
| Whitelisted Blocks: | 7,700 |
| Unknown Blocks: | 0 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Agent.FDD
- Injector.AK
- Lumma.GFD
- Rugmi.IA
- Sheloader.A
Show More
- Stealer.KF
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\is-k1udj.tmp\6539d3f0727c1c58882f5879df3ca986e6ac8244_0005246360.tmp | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Process Shell Execute |
|
| User Data Access |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
"C:\Users\Qquifxeh\AppData\Local\Temp\is-K1UDJ.tmp\6539d3f0727c1c58882f5879df3ca986e6ac8244_0005246360.tmp" /SL5="$50054,4294144,832512,c:\users\user\downloads\6539d3f0727c1c58882f5879df3ca986e6ac8244_0005246360"
|


