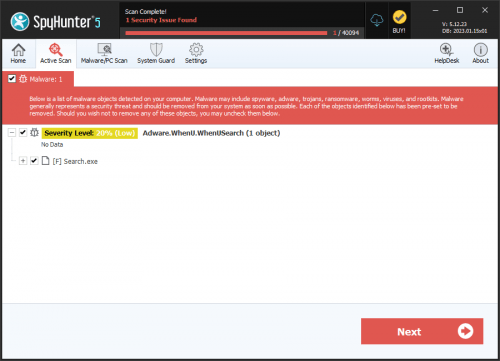
Adware.WhenU
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 12,131 |
| Threat Level: | 20 % (Normal) |
| Infected Computers: | 1,008 |
| First Seen: | July 24, 2009 |
| Last Seen: | October 4, 2026 |
| OS(es) Affected: | Windows |
The detection of Adware.WhenU on your system indicates the presence of unwanted software that may be displaying advertisements, collecting user data, or performing other unwanted actions. Adware, short for advertising-supported software, is a type of software that displays advertisements on a user's computer, often in the form of pop-ups, banners, or sponsored content. While not all adware is malicious, it can still pose a significant nuisance and potential security risk to users.
Table of Contents
What Is Adware.WhenU?
Adware.WhenU refers to a specific detection of adware software that has been identified on your system. The name itself does not provide specific information about the malware family or its characteristics, but rather serves as a general indicator of the presence of adware. Adware can be bundled with other software, downloaded from the internet, or installed through exploits in vulnerable systems. It is essential to understand that adware can come in many forms and may not always be immediately apparent.
How Adware.WhenU Operates
Adware, including Adware.WhenU, typically operates by displaying advertisements to users, often in exchange for "free" software or services. These advertisements can be in the form of pop-ups, banners, or sponsored content, and may be targeted based on user behavior or demographics. Adware may also collect user data, such as browsing history or search queries, to deliver more targeted advertisements. In some cases, adware may also perform other unwanted actions, such as modifying system settings or installing additional software.
Symptoms of Infection
Symptoms of Adware.WhenU infection may include an increase in pop-up advertisements, new toolbars or extensions installed in your web browser, or changes to your system's default search engine or homepage. You may also notice a decrease in system performance or an increase in unwanted software installations. If you suspect that your system has been infected with Adware.WhenU, it is essential to take immediate action to remove the adware and prevent further damage.
How to Remove Adware.WhenU
- Boot your system in Safe Mode with Networking to prevent the adware from loading and to allow for internet access.
- Perform a full scan of your system using a reputable anti-malware tool, such as SpyHunter, to detect and remove any adware or other malicious software.
- Uninstall any suspicious programs or software that may be related to the adware infection.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any unwanted extensions or modifications.
- Reboot your system and perform a follow-up scan to ensure that the adware has been completely removed.
Conclusion
Removing Adware.WhenU from your system requires careful attention to detail and a thorough understanding of the removal process. By following the steps outlined above and using reputable anti-malware tools, you can effectively remove the adware and prevent future infections. It is essential to remain vigilant and to regularly scan your system for any signs of malware or unwanted software. By taking proactive steps to protect your system, you can help to ensure a safe and secure computing experience.
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Panda | Generic Malware |
| AVG | Generic_c.HS |
| Fortinet | Adware/Newdotnet |
| Ikarus | not-a-virus:AdWare.Win32.NewDotNet |
| AhnLab-V3 | Win-Adware/SaveNow.862105 |
| Sophos | WhenU |
| AntiVir | ADSPY/SaveNo.AR.1.A |
| F-Secure | Adware.Whenu.Savenow |
| Comodo | UnclassifiedMalware |
| BitDefender | Adware.Whenu.Savenow.A |
| Kaspersky | not-a-virus:AdWare.Win32.SaveNow.ak |
| ClamAV | Adware.SaveNow-9 |
| Avast | Win32:Adware-gen [Adw] |
| F-Prot | W32/Adware.WQU |
| NOD32 | Win32/Adware.WhenUSave |
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | ss2r2.exe | 411c0dac755c75716225dc491f202da0 | 9 |
| 2. | Save.exe | a1cde69eb9cc64da290e70b6c7702487 | 0 |
Registry Details
Analysis Report
General information
| Family Name: | Adware.WhenU |
|---|---|
| Signature status: | Root Not Trusted |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
32a1f373a6366cf248f74c5d5ef06583
SHA1:
c6ab08c49fbe7021744507913e5146bf3369a07e
SHA256:
A2F20DC63AC9CC6E90C002E25016D73C3D6705111284960047F56040917BEC1E
File Size:
2.06 MB, 2063479 bytes
|
|
MD5:
2a0facf5f9bc5d190540674cb433279c
SHA1:
c48acc17dd575e79f83c29f37e9932e1e93c2460
SHA256:
B660824D3AAC97DF2144FD2F8323B6674F9CC79E21317B2DEA109962291ED62B
File Size:
1.34 MB, 1342013 bytes
|
|
MD5:
1833f646a0eacbf671a2c7790ef64d6a
SHA1:
bd7b38772805e7a37091174f88c17620293f4c6d
SHA256:
CB19CF7E050F62C4DB7F0A7A3A10F948D403DD0280592DE277D506447C5CCE26
File Size:
3.52 MB, 3521888 bytes
|
|
MD5:
2ade4d204b3fef22f087d3165a833099
SHA1:
cac3a0a4f2813ab8c11190fb3d230bc906ca2baf
SHA256:
CD02C93AB8235DCDA76BD14BD4901C8235B0A27A406C12371F11299CF829E51B
File Size:
71.68 KB, 71680 bytes
|
|
MD5:
9d4ca6969ebe91ed876762b6a84068e5
SHA1:
86bae102dabce02ddd33ec738360794aaf944b89
SHA256:
A87CD59684FDE45D396CCD133F1C5F6EA2D642158AFEA3191D2FF0E4059D7561
File Size:
2.62 MB, 2615416 bytes
|
Show More
|
MD5:
867359b24f2e6ad72af1741d8a4c9dc9
SHA1:
9f0ead1988ad6c0807d84592007cb494ea11d8d6
SHA256:
12190BF71EA2D6CDF047530B8074C3B9E8F7AFDFFAE66CA495606E925AB717A4
File Size:
3.40 MB, 3399520 bytes
|
|
MD5:
b322ee4ca04901c46f08e84ed78e0a08
SHA1:
1697248478a10a59193037daece07d222b8e177f
SHA256:
A0008AC317C6EC1C3C108B9D4D04CA6DB1BFD135314971E332ADC76D957D1943
File Size:
15.42 KB, 15416 bytes
|
|
MD5:
82597d5b99529cd939579b78cf4c4b16
SHA1:
2b371a86e30f4266cc50a2f8ea41034a5514e3e2
SHA256:
2BE16C57AB284E67B3868341F0761AEA51979716DE05EB4F25F70CE732E32C3E
File Size:
862.61 KB, 862611 bytes
|
|
MD5:
fc51dade40cff078100cc784d9459f46
SHA1:
cf1c838ec7d14b3be855f7df2d37644be035aae9
SHA256:
A7B21EB10B671403191BFEBDCF9ED6BB6A140210A4A6E57326CC91DA1170E031
File Size:
1.74 MB, 1736392 bytes
|
|
MD5:
e9ea53255864058b16356b8c5828beb7
SHA1:
95224819256f70be411fb5cb72224435767e35d2
SHA256:
7456066D12DB7FFE3D1798014F62207F64A1B6E22EF27EB5336DCAA53E3449A5
File Size:
1.45 MB, 1449368 bytes
|
|
MD5:
c4cb48dd555b6588d6cc2a00e157478c
SHA1:
e9dc2b0f7d0d009ce5d741e0758d9f326ca11f7d
SHA256:
1415CED3F872F10004E2A02FFC740127E24A6CC0778FBFF043F51939F27D6B5F
File Size:
2.38 MB, 2382968 bytes
|
|
MD5:
7ee2cabcf0800fafaeeae83c8e0c46aa
SHA1:
d371c98e477f11eb7a0a2574623659b51b6d7c1b
SHA256:
26DBB0FCA6A481BE1E337AEC91BC8E9DF185D2091ABF189F30EF3446A7550C8B
File Size:
420.76 KB, 420760 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has exports table
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
Show More
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup: http://www.innosetup.com |
| Company Name |
|
| File Description |
|
| File Version |
|
| Internal Name |
|
| Legal Copyright |
|
| Original Filename |
|
| Product Name |
|
| Product Version |
|
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| DAEMON Tools Code Signing Services | Generic Root Trust CA | Root Not Trusted |
| Free Peers Inc. | Thawte Premium Server CA | Root Not Trusted |
| Freeze.com, LLC | VeriSign Class 3 Code Signing 2001 CA | Root Not Trusted |
| WHENU.COM INC | VeriSign Class 3 Code Signing 2001 CA | Root Not Trusted |
| Free Peers, Inc. | VeriSign Class 3 Code Signing 2001-4 CA | Root Not Trusted |
Show More
| Freeze.com, LLC | VeriSign Class 3 Code Signing 2004 CA | Root Not Trusted |
File Traits
- Installer Version
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 26 |
|---|---|
| Potentially Malicious Blocks: | 0 |
| Whitelisted Blocks: | 26 |
| Unknown Blocks: | 0 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- NetBus.A
- Sqwire.AA
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| \device\namedpipe\gmdasllogger | Generic Write,Read Attributes |
| c:\users\user\appdata\local\microsoft\windows\usrclass.dat{dba6b5ef-640a-11ed-9bcb-f677369d361c}.txr.2.regtrans-ms | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\glb4d20.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glb9580.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glbaa83.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glbcecf.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glbf147.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glbf429.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glc4dd5.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\glc4fef.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
Show More
| c:\users\user\appdata\local\temp\glc9726.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\glcac29.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\glcd085.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\glcf2de.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\glcf64c.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\glf536c.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glf536c.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glf538d.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glf538d.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glf538e.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glf538e.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glf9de1.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glf9de1.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glfa18c.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glfa18c.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glfa69d.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glfa69d.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glfa73b.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glfa73b.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glfb2e4.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glfb2e4.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glfb788.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glfb788.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glfdcad.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glfdcad.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glfdcae.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glfdcae.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glff756.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glff756.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glff7a5.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glff7a5.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glff7b6.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glff7b6.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glff8d0.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glff8d0.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glff8f0.tmp | Synchronize,Write Attributes |
| c:\users\user\appdata\local\temp\glff8f0.tmp | Synchronize,Write Data |
| c:\users\user\appdata\local\temp\glg532d.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glgf726.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glgf890.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glk9766.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glkac68.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glkd0c4.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glm99c8.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glmae8c.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glmf31d.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nskdf40.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete |
| c:\users\user\appdata\local\temp\~glh0000.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\~glh0001.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\~glh0002.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\~glh0003.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\~glh0004.tmp | Generic Write,Read Attributes |
| c:\windows\syswow64\glbsinst.%$d | Generic Write,Read Attributes |
| c:\~glhttp1.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Process Manipulation Evasion |
|
| Process Shell Execute |
|
| Anti Debug |
|
| User Data Access |
|
| Network Winsock2 |
|
| Network Wininet |
|
| Network Winsock |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
C:\Users\Ezeweyrd\AppData\Local\Temp\GLB4D20.tmp C:\Users\Ezeweyrd\AppData\Local\Temp\GLB4D20.tmp 4736 c:\users\user\DOWNLO~1\BD7B38~1
|
C:\Users\Qmvtumul\AppData\Local\Temp\GLBAA83.tmp C:\Users\Qmvtumul\AppData\Local\Temp\GLBAA83.tmp 4736 c:\users\user\DOWNLO~1\86BAE1~1
|
C:\Users\Xcivgsfz\AppData\Local\Temp\GLBF147.tmp C:\Users\Xcivgsfz\AppData\Local\Temp\GLBF147.tmp 4736 c:\users\user\DOWNLO~1\9F0EAD~1
|
C:\Users\Rtloievv\AppData\Local\Temp\GLBF429.tmp C:\Users\Rtloievv\AppData\Local\Temp\GLBF429.tmp 4736 c:\users\user\DOWNLO~1\CF1C83~1
|
C:\Users\Pdpmbnfw\AppData\Local\Temp\GLB9580.tmp C:\Users\Pdpmbnfw\AppData\Local\Temp\GLB9580.tmp 4736 c:\users\user\DOWNLO~1\E9DC2B~1
|
Show More
C:\Users\Cxgaiitf\AppData\Local\Temp\GLBCECF.tmp C:\Users\Cxgaiitf\AppData\Local\Temp\GLBCECF.tmp 4736 c:\users\user\DOWNLO~1\D371C9~1
|