Trojan.Downloader.Banload.ARZ
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 80 % (High) |
| Infected Computers: | 102 |
| First Seen: | March 29, 2013 |
| Last Seen: | January 23, 2022 |
| OS(es) Affected: | Windows |
The detection of Trojan.Downloader.Banload.ARZ on your system indicates a potential security threat that requires immediate attention. This Trojan-type threat is designed to download and install additional malware on your computer, which can lead to a range of problems, including data theft, system crashes, and unauthorized access to your personal information.
Table of Contents
What Is Trojan.Downloader.Banload.ARZ?
Trojan.Downloader.Banload.ARZ is a type of malware that uses social engineering tactics or exploits vulnerabilities in software to gain access to your system. Once installed, it can download and execute additional malware, allowing attackers to remotely control your computer, steal sensitive information, or use your system as a botnet to spread spam or launch denial-of-service attacks.
How Trojan.Downloader.Banload.ARZ Operates
Trojan.Downloader.Banload.ARZ typically operates by using stealthy techniques to evade detection by security software. It may use code obfuscation, anti-debugging techniques, or rootkit functionality to hide its presence on your system. The malware may also use legitimate system processes or files to disguise its malicious activities, making it challenging to detect and remove.
- It can create backdoors to allow remote access to your system
- It can modify system settings or registry entries to maintain persistence
- It can communicate with command and control servers to receive updates or instructions
Symptoms of Infection
Infected systems may exhibit a range of symptoms, including slow system performance, frequent crashes, or unfamiliar programs running in the background. You may also notice unusual network activity, such as unexpected outgoing connections or data transfers. In some cases, the malware may display fake alerts or warnings to trick you into installing additional malware or revealing sensitive information.
How to Remove Trojan.Downloader.Banload.ARZ
- Boot your system in Safe Mode with Networking to prevent the malware from loading
- Run a full scan with a reputable anti-malware tool, such as SpyHunter, to detect and remove the malware
- Uninstall any suspicious programs or applications that may be related to the malware
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any malicious extensions or add-ons
- Reboot your system and run another full scan to ensure that the malware has been completely removed
Conclusion
Removing Trojan.Downloader.Banload.ARZ from your system requires a combination of technical expertise and caution. By following the steps outlined above and using reputable security software, you can help to ensure that your system is free from malware and protected against future threats. Remember to always be vigilant when surfing the web, opening email attachments, or installing software, as these are common ways that malware can infect your system. By taking proactive steps to protect your system and staying informed about the latest security threats, you can help to safeguard your personal information and maintain the integrity of your computer.
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Comodo | Heur.Suspicious |
| F-Prot | W32/FakeAlert.FT.gen!Eldorado |
| McAfee | Artemis!57844157AC48 |
| McAfee | RDN/Generic.dx!hc |
| Panda | Trj/Injector.AV |
| AVG | Startpage.TBB |
| Fortinet | W32/VBKrypt.PEJC!tr |
| Ikarus | Trojan.Win32.VBKrypt |
| AntiVir | TR/Graftor.69097.1 |
| Kaspersky | Trojan.Win32.VBKrypt.pejc |
| Symantec | WS.Reputation.1 |
| McAfee | Artemis!B2F23B6591BF |
| AVG | Generic19.AJIJ |
| Ikarus | Trojan.Win32.Refroso |
| AhnLab-V3 | Trojan/Win32.Gen |
SpyHunter Detects & Remove Trojan.Downloader.Banload.ARZ
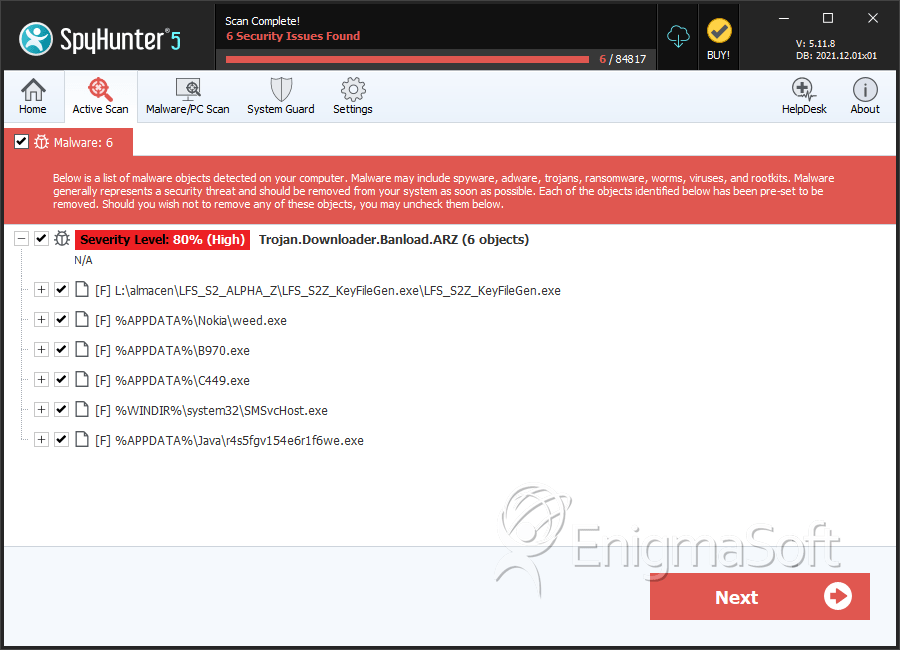
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | LFS_S2Z_KeyFileGen.exe | b6322868f841946ffbe53edd2a8a1cec | 43 |
| 2. | weed.exe | 57844157ac487e4957299ad6f913b244 | 12 |
| 3. | 7D99.exe | b2f23b6591bfee11d224c19e974b9d1b | 5 |
| 4. | 6FB4.exe | df5fa3783d3f69f17e6859f8018b8b6e | 5 |
| 5. | SMSvcHost.exe | 780570b465faf1ff329f15493fa5b946 | 2 |
| 6. | r4s5fgv154e6r1f6we.exe | 8bdb6531c7b03cce7f6357074ed1b664 | 2 |


