Trojan.Delf.G
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 80 % (High) |
| Infected Computers: | 98 |
| First Seen: | July 24, 2009 |
| Last Seen: | June 14, 2026 |
| OS(es) Affected: | Windows |
The detection of Trojan.Delf.G on your system indicates a potential security threat that requires immediate attention. Trojans are a type of malware that can cause significant harm to your computer and compromise your personal data. It is essential to understand the nature of this threat and take appropriate steps to remove it and prevent future infections.
Table of Contents
What Is Trojan.Delf.G?
Trojan.Delf.G is a type of Trojan horse malware that can infect your computer without your knowledge or consent. The name "Trojan" refers to the fact that this type of malware disguises itself as a legitimate program or file, allowing it to bypass security measures and gain access to your system. Once inside, Trojan.Delf.G can cause a range of problems, from stealing sensitive information to disrupting system performance.
How Trojan.Delf.G Operates
Trojan.Delf.G operates by exploiting vulnerabilities in your system or tricking you into installing it. This can happen through various means, such as opening malicious email attachments, visiting compromised websites, or downloading infected software. Once installed, the Trojan can communicate with its creators, allowing them to control your system remotely and steal sensitive information, such as login credentials, financial data, or personal files.
Symptoms of Infection
The symptoms of a Trojan.Delf.G infection can vary, but common signs include slow system performance, unexpected pop-ups or ads, and unexplained changes to your system settings. You may also notice that your browser is being redirected to unfamiliar websites or that your antivirus software is disabled. In some cases, the infection may not exhibit any noticeable symptoms, making it difficult to detect without proper scanning tools.
- Slow system performance or crashes
- Unexplained changes to system settings or files
- Pop-ups or ads that appear unexpectedly
- Browser redirection or unfamiliar websites
- Disabled antivirus software or firewall
How to Remove Trojan.Delf.G
- Boot your system in Safe Mode with Networking to prevent the Trojan from loading and to allow for a clean scan.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system and detect any malware components.
- Uninstall any suspicious programs or applications that may be related to the infection.
- Reset your web browsers, such as Chrome, Firefox, or Edge, to their default settings to remove any malicious extensions or add-ons.
- Reboot your system and perform another scan to ensure that all malware components have been removed.
Conclusion
Removing Trojan.Delf.G from your system requires careful attention to detail and a comprehensive approach to ensure that all malware components are eliminated. By following the steps outlined above and maintaining good security practices, such as keeping your operating system and software up to date, using strong passwords, and being cautious when opening email attachments or downloading software, you can reduce the risk of future infections and protect your personal data. Remember to always use reputable anti-malware tools and to regularly scan your system for any signs of malware activity.
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Panda | Trj/Downloader.MDW |
| NOD32 | probably a variant of Win32/TrojanDownloader.Delf |
| McAfee-GW-Edition | Trojan.Dldr.Delf.gkb |
| McAfee+Artemis | Generic!Artemis |
| Ikarus | Trojan-Downloader.Win32.Delf |
| F-Secure | Trojan-Downloader.Win32.Delf.gkb |
| eSafe | Suspicious File |
| Comodo | TrojWare.Win32.TrojanDownloader.Delf.gkb |
| BitDefender | Trojan.Generic.249612 |
| AVG | Downloader.Generic7.EWA |
| Avast | Win32:Rootkit-gen |
| Authentium | W32/Downldr2.BOTB |
| Antiy-AVL | Trojan/Win32.Delf |
| AntiVir | TR/Dldr.Delf.gkb |
| AhnLab-V3 | Win-Trojan/Xema.variant |
SpyHunter Detects & Remove Trojan.Delf.G
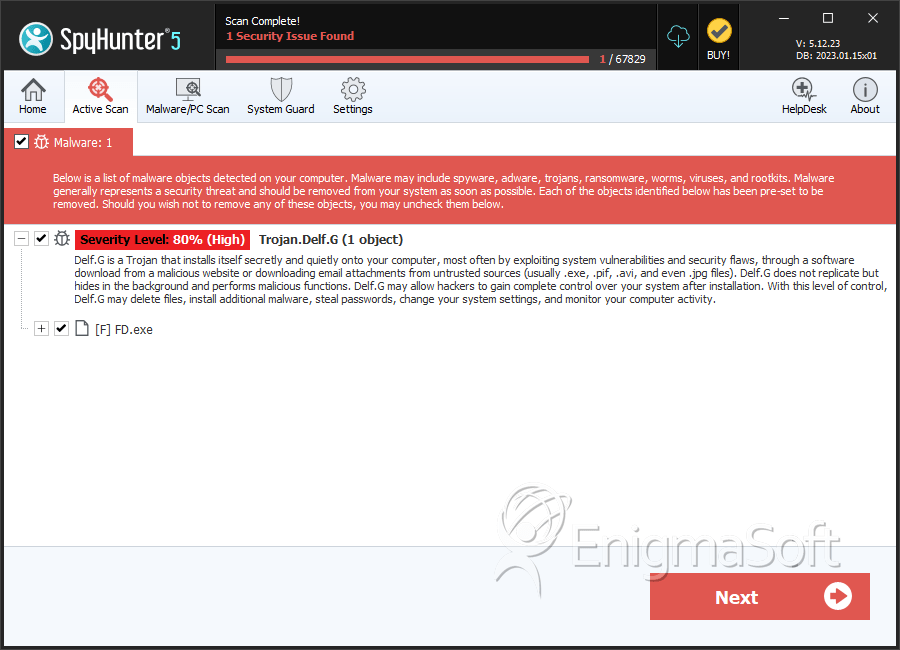
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | FD.exe | 0bea26a93ed61a0ecf9ef9d5db66464d | 0 |
Analysis Report
General information
| Family Name: | Trojan.Delf.G |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
84514c305dab0f4bc28496ac728d60c7
SHA1:
fe68f744ef272013ef6e5ca2b582e69bc576c859
SHA256:
4BF40B298B85472D408D8955191D1E5FFA0514858FB004EFE5BED7AB6CC685A8
File Size:
9.78 MB, 9780484 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
Show More
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup. |
| Company Name | DXsoft |
| File Description | AALog Setup |
| File Version | 3.1.0.1157 |
| Legal Copyright | Copyright © 1998-2011 Alexander Anipkin |
| Product Name | AALog |
| Product Version | 3.1.0.1157 |
File Traits
- HighEntropy
- imgui
- packed
- VirtualQueryEx
- WriteProcessMemory
- x86
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\is-ie66t.tmp\_isetup\_regdll.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\is-ie66t.tmp\_isetup\_setup64.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\is-ie66t.tmp\_isetup\_shfoldr.dll | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\is-rfp93.tmp\fe68f744ef272013ef6e5ca2b582e69bc576c859_0009780484.tmp | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Process Manipulation Evasion |
|
| Process Shell Execute |
|
| User Data Access |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
"C:\Users\Yvgtxgkd\AppData\Local\Temp\is-RFP93.tmp\fe68f744ef272013ef6e5ca2b582e69bc576c859_0009780484.tmp" /SL5="$5030A,9536224,53248,c:\users\user\downloads\fe68f744ef272013ef6e5ca2b582e69bc576c859_0009780484"
|


