PWSteal.Wowsteal.AO
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 80 % (High) |
| Infected Computers: | 1 |
| First Seen: | July 24, 2009 |
| OS(es) Affected: | Windows |
The detection of PWSteal.Wowsteal.AO on your system indicates a potential threat to your security and privacy. This detection name suggests a type of malicious software designed to steal sensitive information, but without more specific details, it's crucial to understand the general implications and how to address them. Malware of this nature can compromise your personal data, including login credentials, which is why prompt action is necessary.
Table of Contents
What Is PWSteal.Wowsteal.AO?
PWSteal.Wowsteal.AO appears to be related to password-stealing malware, which is a category of Trojans. These types of malware are designed to capture and transmit sensitive information, such as passwords, credit card numbers, and other personal data, to unauthorized parties. The exact mechanisms and targets of PWSteal.Wowsteal.AO are not specified, but its classification suggests it is capable of infiltrating systems and remaining hidden while it carries out its malicious activities.
How PWSteal.Wowsteal.AO Operates
Malware like PWSteal.Wowsteal.AO typically operates by exploiting vulnerabilities in software or tricking users into installing it. Once installed, it can use various techniques to evade detection, including disguising itself as legitimate software, hiding in temporary folders, or using encryption to conceal its communications. It may also use keyloggers or screen scrapers to capture sensitive information directly from the user's interactions with the computer.
Symptoms of Infection
Symptoms of an infection can be subtle and may not always be immediately apparent. Users might notice unusual behavior from their computer, such as unexpected pop-ups, slow performance, or unfamiliar programs listed in their startup menu. Sometimes, the only indication of an infection is the detection by antivirus software. Given the stealthy nature of password-stealing malware, it's possible for a system to be infected without showing any overt signs of compromise.
How to Remove PWSteal.Wowsteal.AO
- Boot your computer in Safe Mode with Networking to limit the malware's ability to interfere with the removal process. This mode loads only the essential drivers and services, making it easier to remove malicious software.
- Perform a full scan of your system using a reputable antivirus tool, such as SpyHunter, to detect and remove all traces of the malware. Ensure your antivirus software is updated with the latest definitions before running the scan.
- Uninstall any suspicious programs that you do not recognize or that were installed around the time the malware was detected. Be cautious and only remove programs you are certain are not needed.
- Reset your web browsers (Chrome, Firefox, Edge, etc.) to their default settings. This can help remove any malicious extensions or settings changes made by the malware. For each browser, you can usually find the reset option in the settings or preferences menu.
- After completing the above steps, reboot your computer and run another full scan with your antivirus software to ensure all remnants of the malware have been removed.
Conclusion
The removal of PWSteal.Wowsteal.AO requires careful and thorough steps to ensure your system is completely clean and secure. It's also a reminder of the importance of preventive measures, such as keeping your operating system and software up to date, using strong and unique passwords, and being cautious with emails and downloads from unknown sources. By understanding how malware operates and taking proactive steps, you can significantly reduce the risk of future infections and protect your sensitive information.
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Panda | Trj/CI.A |
| AVG | PSW.OnlineGames3.FA |
| Fortinet | W32/GameThief.DLL!tr.spy |
| Ikarus | Trojan-GameThief.Win32.WOW |
| AhnLab-V3 | Win-Trojan/WowHack.86016.O |
| Antiy-AVL | Trojan/Win32.WOW |
| eTrust-Vet | Win32/Wowpa.GY |
| Sophos | Troj/GamePSW-B |
| McAfee-GW-Edition | Trojan.Hijacker.Gen |
| AntiVir | TR/Hijacker.Gen |
| F-Secure | Trojan-PSW:W32/WOW.ADX |
| BitDefender | Trojan.Generic.1560731 |
| Kaspersky | Trojan-GameThief.Win32.WOW.glt |
| ClamAV | Trojan.Spy-59867 |
| Symantec | Infostealer.Gampass |
SpyHunter Detects & Remove PWSteal.Wowsteal.AO
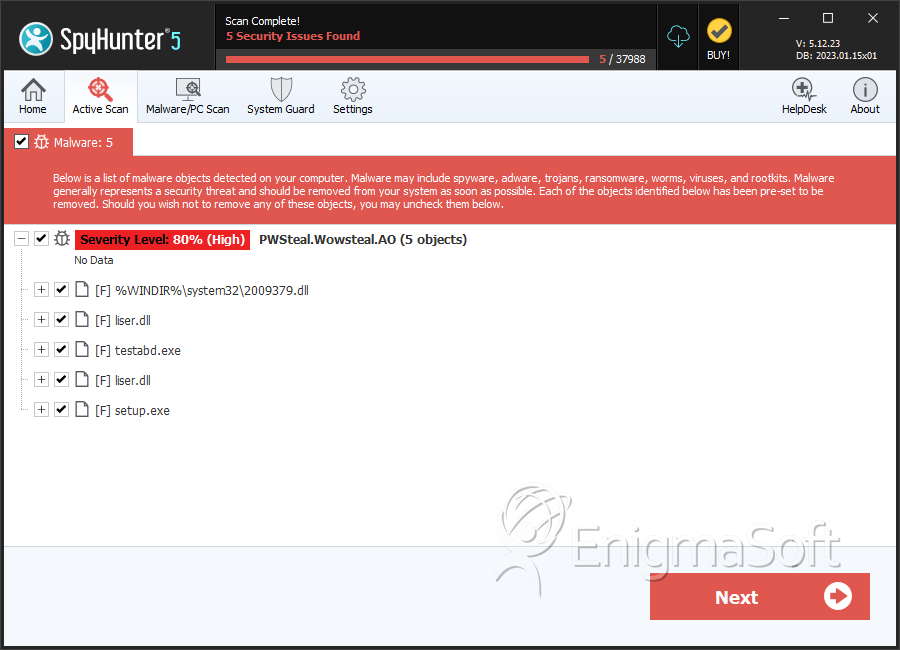
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | 2009379.dll | 4be74b32ef28684779ef11830fa1671c | 1 |
| 2. | liser.exe | d3305754f688a304a18190ecf03aa58c | 0 |
| 3. | testabd.exe | 2aea63d6aaf45b2b7e614d5c803e1322 | 0 |
| 4. | liser.dll | 193cd03784b40a52d21ff9d14d9e3dba | 0 |
| 5. | setup.exe | 5838CC611DE1812E5A3588EBC35D1BB8 | 0 |