PUP.PC Booster
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 22,462 |
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 49 |
| First Seen: | December 23, 2022 |
| Last Seen: | August 10, 2026 |
| OS(es) Affected: | Windows |
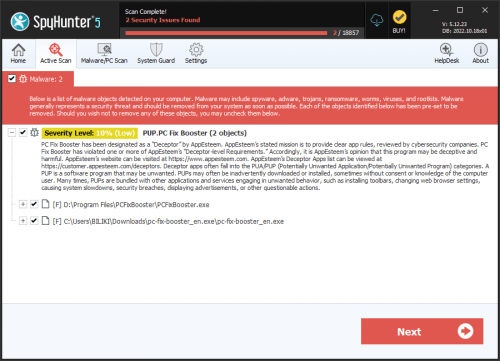
Your system has been detected with PUP.PC Booster, a potentially unwanted program that may have been installed without your knowledge or consent. This type of program can cause a range of issues, from slowing down your computer to potentially exposing your personal data to risk. In this report, we will provide you with information on what PUP.PC Booster is, how it operates, the symptoms of infection, and most importantly, how to remove it from your system.
Table of Contents
What Is PUP.PC Booster?
PUP.PC Booster is a type of potentially unwanted program (PUP) that is designed to appear as a useful tool, but in reality, it can cause more harm than good. PUPs are often bundled with other software or downloaded from the internet, and they can be difficult to remove once they are installed. PUP.PC Booster may promise to improve the performance of your computer or provide other benefits, but it is essential to be cautious when dealing with this type of program.
How PUP.PC Booster Operates
PUP.PC Booster operates by installing itself on your system and then running in the background, often without your knowledge or consent. It may collect data about your browsing habits, search history, and other personal information, which can be used for targeted advertising or other malicious purposes. PUP.PC Booster may also slow down your computer by consuming system resources, causing your browser to freeze or crash, and displaying unwanted ads or pop-ups.
Symptoms of Infection
If your system is infected with PUP.PC Booster, you may notice a range of symptoms, including slow computer performance, unwanted ads or pop-ups, and changes to your browser settings or homepage. You may also notice that your browser is redirecting you to unfamiliar websites or that your search results are being hijacked. Additionally, you may see suspicious programs or toolbars installed on your system, which can be difficult to remove.
How to Remove PUP.PC Booster
- Boot your computer in Safe Mode with Networking to prevent PUP.PC Booster from running and to allow you to access the internet to download removal tools.
- Download and install a reputable anti-malware tool, such as SpyHunter, and run a full scan of your system to detect and remove PUP.PC Booster and any other malware that may be present.
- Uninstall any suspicious programs or toolbars that you do not recognize or that you did not intentionally install. Be careful when uninstalling programs, as some may be legitimate or required by your system.
- Reset your browser settings to their default values, including Google Chrome, Mozilla Firefox, and Microsoft Edge. This will help to remove any changes made by PUP.PC Booster and restore your browser to its original state.
- Reboot your computer and run another scan with your anti-malware tool to ensure that PUP.PC Booster has been completely removed and that your system is clean.
Conclusion
Removing PUP.PC Booster from your system requires careful attention to detail and a thorough understanding of how to remove potentially unwanted programs. By following the steps outlined in this report, you should be able to remove PUP.PC Booster and restore your system to its original state. It is essential to be cautious when downloading software from the internet and to always read the terms and conditions before installing any program. Additionally, keeping your operating system and browser up to date with the latest security patches and using a reputable anti-malware tool can help to protect your system from future infections.
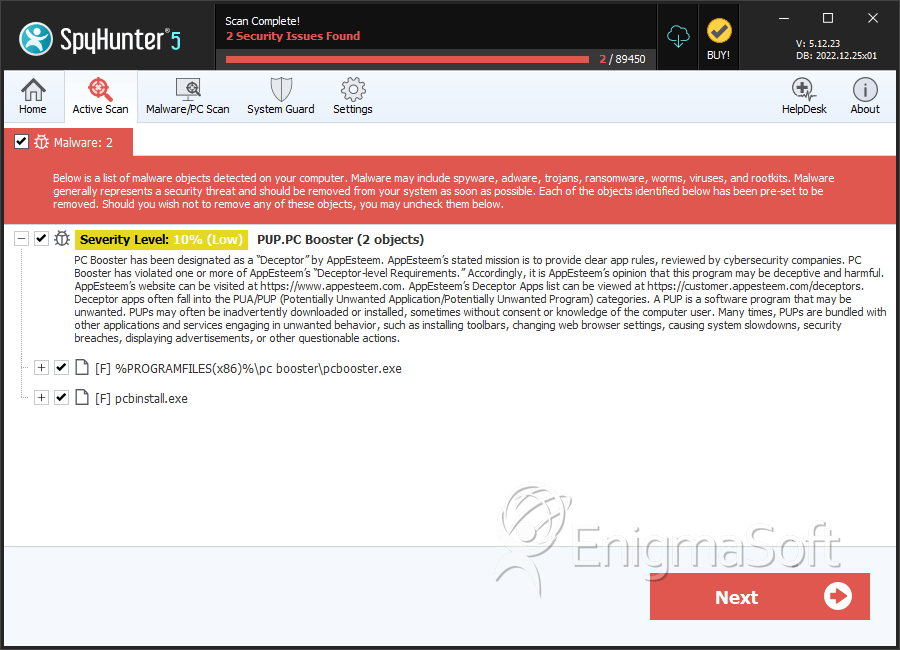
SpyHunter Detects & Remove PUP.PC Booster
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | pcbooster.exe | daffa0f7b409e02d147360340e4b8ae5 | 8 |
| 2. | pcbinstall.exe | 7d56bb2750ff7e8308a5579a7adab90a | 0 |
Analysis Report
General information
| Family Name: | PUP.PC Booster |
|---|---|
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
9a44708543c08a71122e48fceb5b96d3
SHA1:
603b70f4c977a37de5895de6c27c62f70a4ff92a
SHA256:
084C50CC2438A66807D7C87EB7053F9DF48C8509EA31522465DC233951778284
File Size:
2.80 MB, 2801432 bytes
|
|
MD5:
1ca6f2434dba3df11ae92e0c9516d7ca
SHA1:
7e47b074c42dec581dc603163def4829121e5a52
SHA256:
DB31D2BD8E2666FEEBCEDC26B3AB8A428ABD7EBF2C8F1F75FCBB01AFE706E7AD
File Size:
2.91 MB, 2910624 bytes
|
|
MD5:
e8018216efeb02066c0fdee87c4b1e45
SHA1:
20ec857713b547ec81dad1e9b1030983ee01b508
SHA256:
E4D50317971CB49520C904B9AD5D6EA21E3C282B63AA16D816254689043BE5CB
File Size:
74.70 KB, 74704 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | This installation was built with Inno Setup. |
| Company Name |
|
| File Description |
|
| File Version |
|
| Legal Copyright |
|
| Legal Trademarks | GoUP and PC HealthBoost are trademarks of Boost Software Inc. |
| Product Name |
|
| Product Version | 2.1.1.10 |
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Boost Software Inc | VeriSign Class 3 Code Signing 2010 CA | Self Signed |
File Traits
- HighEntropy
- Inno
- InnoSetup Installer
- Installer Manifest
- Installer Version
- Nullsoft Installer
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 77 |
|---|---|
| Potentially Malicious Blocks: | 0 |
| Whitelisted Blocks: | 77 |
| Unknown Blocks: | 0 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- Agent.MH
- Agent.MI
- Agent.MU
- Autorun.LA
- FakeAV.AU
Show More
- Trojan.Downloader.Gen.BQ
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\programdata\pchealthboost\pchealthboost-setup.exe | Synchronize,Write Data |
| c:\programdata\pchealthboost\pchealthboost-setup.exe.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete,LEFT 262144 |
| c:\users\user\appdata\local\temp\nsn444.tmp\crccheck.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsn444.tmp\langdll.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsn444.tmp\system.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsn444.tmp\uac_unicode.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsn444.tmp\userinfo.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsy434.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete |
| c:\users\user\appdata\local\temp\nsze479.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete |
| c:\users\user\appdata\local\temp\nsze489.tmp | Synchronize,Write Attributes |
Show More
| c:\users\user\appdata\local\temp\nsze489.tmp\uac.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsze489.tmp\uac.dll | Synchronize,Write Attributes |
Registry Modifications
Registry Modifications
This section lists registry keys and values that were created, modified and/or deleted by samples in this family. Windows Registry activity can provide valuable insight into malware functionality. Additionally, malware often creates registry values to allow itself to automatically start and indefinitely persist after an initial infection has compromised the system.| Key::Value | Data | API Name |
|---|---|---|
| HKLM\system\controlset001\control\session manager::pendingfilerenameoperations | *1\??\C:\Windows\SystemTemp\MicrosoftEdgeUpdate.exe.old122e4*1\??\C:\Windows\SystemTemp\CopilotUpdate.exe.old12352*1\??\C:\P | RegNtPreCreateKey |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| User Data Access |
|