Best Free Keylogger Lite
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 3,664 |
| Threat Level: | 10 % (Normal) |
| Infected Computers: | 2,302 |
| First Seen: | November 26, 2019 |
| Last Seen: | October 4, 2026 |
| OS(es) Affected: | Windows |
The detection of Best Free Keylogger Lite on your system indicates a potential security threat that requires immediate attention. This Trojan-type threat is designed to secretly monitor and record keystrokes, potentially leading to unauthorized access to sensitive information such as passwords, credit card numbers, and other personal data.
Table of Contents
What Is Best Free Keylogger Lite?
Best Free Keylogger Lite is a type of malicious software that is designed to remain hidden on an infected system, making it difficult to detect without the use of specialized security software. Its primary function is to capture and record keystrokes, which can then be transmitted to a remote server or saved locally for later retrieval. This type of threat can be particularly dangerous, as it can lead to identity theft, financial fraud, and other serious consequences.
How Best Free Keylogger Lite Operates
Once Best Free Keylogger Lite has infected a system, it can begin to monitor and record keystrokes in real-time. This can include login credentials, email passwords, and other sensitive information. The malware may also be able to capture screenshots, monitor browsing activity, and even record audio and video. In some cases, the malware may also be able to spread to other systems through infected files, emails, or other means.
Symptoms of Infection
Systems infected with Best Free Keylogger Lite may exhibit a range of symptoms, including slow system performance, unusual network activity, and unexplained changes to system settings. In some cases, the malware may also cause system crashes, freezes, or other instability issues. However, in many cases, the malware may operate silently, making it difficult to detect without the use of specialized security software.
- Unexplained system crashes or freezes
- Slow system performance
- Unusual network activity
- Unexplained changes to system settings
How to Remove Best Free Keylogger Lite
- Boot your system in Safe Mode with Networking to prevent the malware from loading and to allow for easier removal.
- Use a reputable security tool, such as SpyHunter, to perform a full scan of your system and detect and remove any malware.
- Uninstall any suspicious programs or applications that may be related to the malware.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any malicious extensions or add-ons.
- Reboot your system and perform a follow-up scan to ensure that the malware has been completely removed.
Conclusion
The detection and removal of Best Free Keylogger Lite is a critical step in protecting your system and sensitive information from potential security threats. By following the steps outlined above and using reputable security software, you can help to ensure that your system is safe and secure. It is also important to practice good security habits, such as regularly updating your operating system and software, using strong passwords, and avoiding suspicious emails and attachments, to help prevent future infections.
SpyHunter Detects & Remove Best Free Keylogger Lite
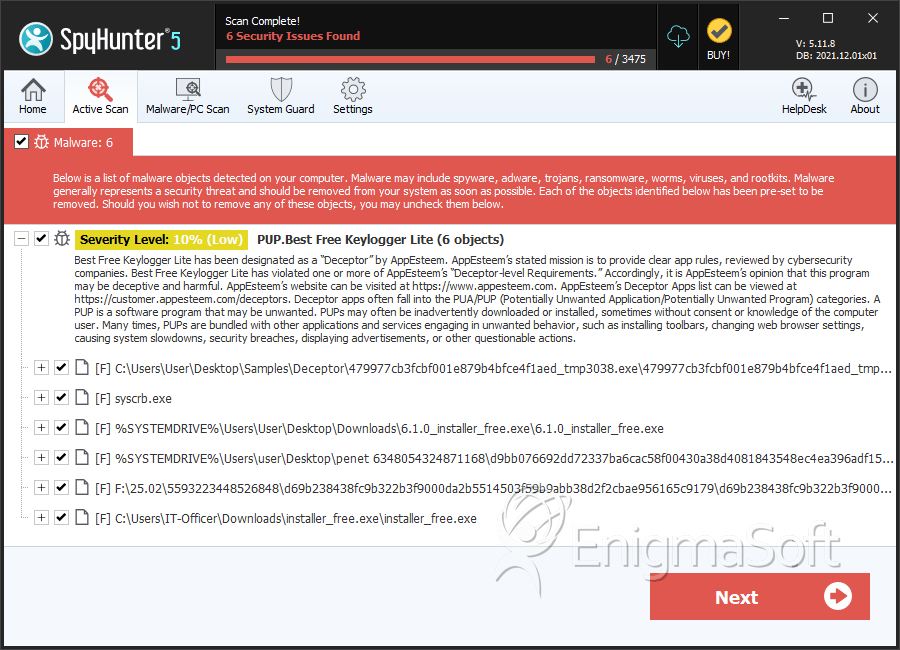
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | 479977cb3fcbf001e879b4bfce4f1aed_tmp3038.exe | 479977cb3fcbf001e879b4bfce4f1aed | 84 |
| 2. | d9bb076692dd72337ba6cac58f00430a38d4081843548ec4ea396adf150fd7a6 | 647570f549305357a343a9d1182255ae | 23 |
| 3. | installer_free.exe | 76e1e74420a575f8504002101ac5170f | 19 |
| 4. | 6.1.0_installer_free.exe | bb55d6a650fdaf946ebcdd26c24f989d | 15 |
| 5. | d69b238438fc9b322b3f9000da2b5514503f59b9abb38d2f2cbae956165c9179 | bf92df38e3ed45c23d581fec2c15b4f9 | 13 |
| 6. | syscrb.exe | 811620702659cf36f3e0bf0a499b1566 | 10 |
| 7. | CBAccess.exe | 880bc48473c99cd781ea6db706fc2ed3 | 7 |
Analysis Report
General information
| Family Name: | PUP.Best Free Keylogger Lite |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
5babb2841593aa81b486dccce953da72
SHA1:
910165fb3420ad029d58eddf923d71d3fb332007
SHA256:
16D30BDE7BE101E05DCD8F3A2665CE966DA59FDE9657F852A8F3D10B72191342
File Size:
2.56 MB, 2561536 bytes
|
|
MD5:
d0c7e58ff85c49c4277f6776716a50ea
SHA1:
93e9fa7973330c33ec0f0f7598bb6d2376894b2d
SHA256:
16BFF1AF258714840BF5F2B1867D6307CB3AE357F329ED3DE63AEBE47006FC62
File Size:
7.74 MB, 7737345 bytes
|
|
MD5:
e6e2af446393e600a5f7ee70db4ecdb2
SHA1:
9457d9bfdbaa8745564577b1a49ea81cbe498f14
SHA256:
35F851ADA36E4C7504821C386676B6515AB924FDA26C7362B5FB55372D12AFF1
File Size:
19.46 KB, 19456 bytes
|
|
MD5:
d3cba993500a61d9926ea605ad6175fd
SHA1:
e308c373f1b50e917f8f5f0c6328e24b7c77a15a
SHA256:
863A59E5B2231C4127DBEF4D4C3002AF523845F47B6E808355E826D43276E23B
File Size:
2.60 MB, 2601984 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has exports table
- File has TLS information
- File is .NET application
- File is 32-bit executable
- File is console application (IMAGE_SUBSYSTEM_WINDOWS_CUI)
Show More
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Assembly Version |
|
| Comments |
|
| Company Name |
|
| File Description |
|
| File Version |
|
| Internal Name |
|
| Legal Copyright |
|
| Original Filename |
|
| Product Name |
|
| Product Version |
|
File Traits
- .NET
- dll
- NewLateBinding
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 1,981 |
|---|---|
| Potentially Malicious Blocks: | 121 |
| Whitelisted Blocks: | 1,210 |
| Unknown Blocks: | 650 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\users\user\appdata\local\temp\is-25ld8.tmp\93e9fa7973330c33ec0f0f7598bb6d2376894b2d_0007737345.tmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\is-7u97e.tmp\_isetup\_setup64.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\is-7u97e.tmp\image.bmp | Generic Write,Read Attributes |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Syscall Use |
Show More
|
| User Data Access |
|
| Anti Debug |
|
| Encryption Used |
|
| Process Shell Execute |
|
| Keyboard Access |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
"C:\Users\Idqxouue\AppData\Local\Temp\is-25LD8.tmp\93e9fa7973330c33ec0f0f7598bb6d2376894b2d_0007737345.tmp" /SL5="$501F8,6911403,832512,c:\users\user\downloads\93e9fa7973330c33ec0f0f7598bb6d2376894b2d_0007737345"
|


