Bandoo Datamngr
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 3,177 |
| Threat Level: | 50 % (Medium) |
| Infected Computers: | 47,359 |
| First Seen: | September 20, 2010 |
| Last Seen: | September 22, 2026 |
| OS(es) Affected: | Windows |
The detection of Bandoo Datamngr on your system indicates a potential security threat that requires immediate attention. This report provides an overview of the threat, its operating methods, symptoms of infection, and steps to remove it from your system.
Table of Contents
What Is Bandoo Datamngr?
Bandoo Datamngr is identified as a type of Trojan threat, which is a broad category of malware designed to deceive users into installing it on their systems. Trojans can lead to various malicious activities, including data theft, unauthorized access, and further malware distribution. The name itself does not specify a known malware family, so it's crucial to understand its behavior and impact rather than its classification.
How Bandoo Datamngr Operates
Trojans like Bandoo Datamngr typically operate by disguising themselves as legitimate software or attachments. Once installed, they can perform a variety of malicious actions, such as monitoring user activity, stealing sensitive information, or downloading additional malware. They often exploit vulnerabilities in software or manipulate users into executing them, making them a significant security risk. Understanding how such threats operate is key to preventing future infections.
Symptoms of Infection
Symptoms of a Bandoo Datamngr infection can vary, but common indicators include unusual system behavior, such as slow performance, frequent crashes, or the appearance of unwanted programs or toolbars. Users might also notice changes in their browser settings or the presence of pop-ups and unwanted advertisements. In some cases, the infection might not display overt symptoms, making regular system scans crucial for detection.
How to Remove Bandoo Datamngr
- Enter Safe Mode with Networking to limit the malware's ability to interfere with the removal process. This mode allows you to use the internet to download necessary tools while minimizing system functionality to prevent the malware from spreading.
- Perform a full scan of your system using a reputable anti-malware tool, such as SpyHunter. Ensure the tool is updated to the latest version to maximize its effectiveness against the latest threats.
- Uninstall suspicious programs that were installed around the time the malware was detected. Be cautious and only remove programs you do not recognize or no longer need.
- Reset your browsers (Chrome, Firefox, Edge, etc.) to their default settings. This step can help remove any malicious extensions or settings changes made by the malware.
- After completing the above steps, reboot your system and perform another scan to ensure the malware has been fully removed. This final scan is crucial to confirm the system's cleanliness and to catch any remnants that might have been missed.
Conclusion
Removing Bandoo Datamngr requires a systematic approach to ensure all components of the malware are eliminated from your system. By following the steps outlined above and maintaining good security practices, such as regularly updating your software and being cautious with email attachments and downloads, you can significantly reduce the risk of future malware infections. Remember, prevention and vigilance are key to protecting your digital assets and personal information in today's evolving cybersecurity landscape.
Aliases
1 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| NOD32 | a variant of Win32/Toolbar.SearchSuite |
SpyHunter Detects & Remove Bandoo Datamngr
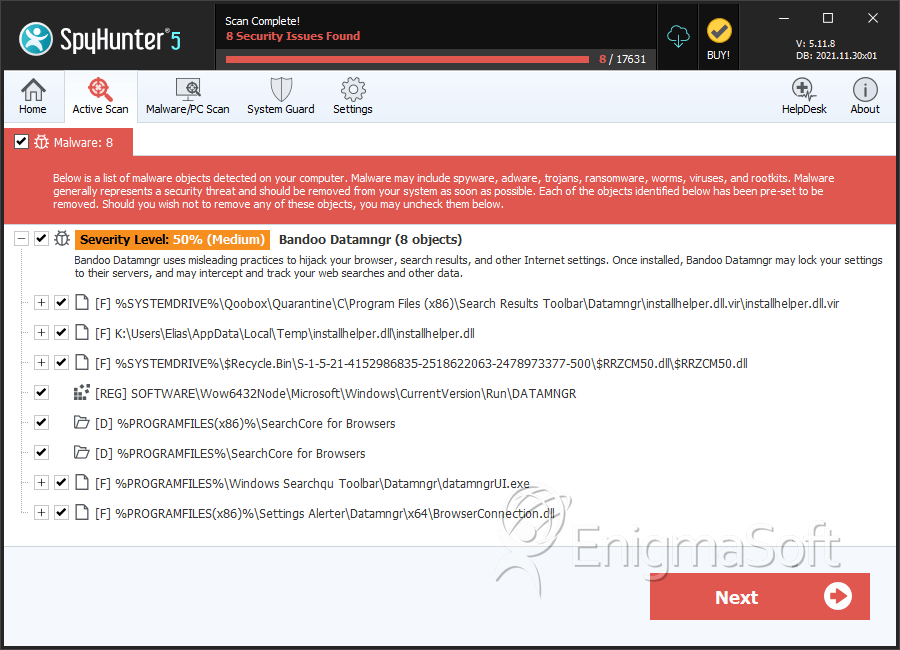
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | installhelper.dll.vir | 46baa11b87c127ad9386d91e844c7351 | 3,665 |
| 2. | $RRZCM50.dll | 2304bf0ff7b559373be4645a09f34f3e | 877 |
| 3. | installhelper.dll | 4b8c528b795b0d872774205aea3fe116 | 645 |
| 4. | DatamngrCoordinator.exe | 21e549a289662f116d7b3398c43654c7 | 571 |
| 5. | del_DM_EXE_49.dll | 82e9093b9404d44d56e89c7a2c29a149 | 454 |
| 6. | del_DM_EXE_83.dll | 122a47b49993422f29b2a20d439e15ca | 118 |
| 7. | datamngr.dll | 9c7ba5358dc5ec4f66716d395fc2a7ab | 12 |
| 8. | DatamngrUI.exe | db2cd06abb5d7c7a6e4d71969a78e52f | 2 |
| 9. | BrowserConnection.dll | 5b95ebbb44e8b8160c8903387697d11c | 2 |
Registry Details
Directories
Bandoo Datamngr may create the following directory or directories:
| %PROGRAMFILES%\SearchCore for Browsers |
| %PROGRAMFILES(x86)%\SearchCore for Browsers |
Analysis Report
General information
| Family Name: | Bandoo Datamngr |
|---|---|
| Signature status: | Self Signed |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
458706d3b83bb0ed0dd2f5751d4dfacf
SHA1:
9a9fcc69efa9663cef9cfcf5824bc1dafa38c46d
File Size:
8.06 MB, 8062368 bytes
|
|
MD5:
442a139475bc38425c683f1569e342ff
SHA1:
c8e295eaa481004abff9764a55614267d82ccf91
SHA256:
BC81054C9DAB108378819E3FA6DDB8C9650682B9179AB2A2B2D23670E76AF46E
File Size:
119.81 KB, 119808 bytes
|
|
MD5:
46323601e689ca0e7db1eebe32de686a
SHA1:
706add146f83a6793a2441df938a70fc7d04178d
SHA256:
99329775C3B9955F322E4C24BEF391567CDCBEB04F0DAC12A03105FED5E0E4FA
File Size:
156.23 KB, 156230 bytes
|
|
MD5:
97e1f8521dbc7b14c98c0f6e6a69451e
SHA1:
6ee82d78af4728169bffc41cb95cd95a5b79f60c
SHA256:
9276F8757A18A392B3AB3B81ABE7A687982935B956C9CD6EC5124309B1A08FC9
File Size:
230.24 KB, 230240 bytes
|
|
MD5:
574166a7a811b1f71232345da17251e4
SHA1:
f8d9497cf37f96ad5538ae2f1dc3fcbff3d0722e
SHA256:
58C9C7097D24801B1C9166C3ABFE8C1E29CF9B5F9A528D1A5BE6BCC0B4AFCA0D
File Size:
440.85 KB, 440848 bytes
|
Show More
|
MD5:
2c2ff7642499a567cb93bf7b6325ffb4
SHA1:
f270ddf32f0769868bf0ab6b9a19dc2e31600e93
SHA256:
10C98BC272CEF5FF86AA981651E34272642913549556A1938FB1A6982C706001
File Size:
7.91 MB, 7913472 bytes
|
|
MD5:
571375e0e59e6a114ca0a9b771df8bf4
SHA1:
f2dfc4be5a242e843876bc3f5d79705b78224e54
SHA256:
1E8B11520B4EC045907FB9456FEAFA415A4915B2AF9BA7C5EA4DA3DDA417008C
File Size:
1.32 MB, 1318592 bytes
|
|
MD5:
9165efe7747ac72fc7769008fc6bac7d
SHA1:
ae1f18f65a1ce62bf6e322fa8c55539489b5a087
SHA256:
778F69A026C30CAD419F12D5422ECFB93C2832A9A0FE50F8CE735878E7D78FD5
File Size:
1.64 MB, 1643624 bytes
|
|
MD5:
51421d17ddf4c32df888c2a5f6e9a3ce
SHA1:
429365e94470c116c59113961fabfcc08990bb97
SHA256:
E64FE977289301CCBBB4D7C404E3AE277F305D76FBA5F666176116E2342C7F63
File Size:
1.32 MB, 1320680 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has exports table
- File is 32-bit executable
- File is console application (IMAGE_SUBSYSTEM_WINDOWS_CUI)
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
Show More
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Company Name |
|
| File Description |
|
| File Version |
|
| Internal Name |
|
| Legal Copyright |
|
| Original Filename |
|
| Product Name |
|
| Product Version |
|
Digital Signatures
Digital Signatures
This section lists digital signatures that are attached to samples within this family. When analyzing and verifying digital signatures, it is important to confirm that the signature’s root authority is a well-known and trustworthy entity and that the status of the signature is good. Malware is often signed with non-trustworthy “Self Signed” digital signatures (which can be easily created by a malware author with no verification). Malware may also be signed by legitimate signatures that have an invalid status, and by signatures from questionable root authorities with fake or misleading “Signer” names.| Signer | Root | Status |
|---|---|---|
| Bandoo Media, Inc | Thawte Code Signing CA - G2 | Hash Mismatch |
| Koyote-Lab Inc. | Thawte Code Signing CA - G2 | Self Signed |
| Bandoo Media, Inc | Thawte Premium Server CA | Root Not Trusted |
| Bandoo Media, Inc | thawte Primary Root CA | Root Not Trusted |
| Koyote-Lab Inc. | thawte Primary Root CA | Root Not Trusted |
File Traits
- big overlay
- HighEntropy
- Installer Manifest
- Installer Version
- nosig nsis
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- AdGazelle.A
- Downloader.Agent.TJ
- Mobogenie
- SearchSuite.C
- Zusy.CA
Files Modified
Files Modified
This section lists files that were created, modified, moved and/or deleted by samples in this family. File system activity can provide valuable insight into how malware functions on the operating system.| File | Attributes |
|---|---|
| c:\program files (x86)\free flv player\log.log | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\glcae1c.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data |
| c:\users\user\appdata\local\temp\nseb934.tmp\apphelp.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nseb934.tmp\license.txt | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nseb934.tmp\modern-header.bmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nseb934.tmp\registry.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nseb934.tmp\soffer.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nseb934.tmp\system.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nseb934.tmp\uac.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nseb934.tmp\uninstall.exe | Generic Write,Read Attributes |
Show More
| c:\users\user\appdata\local\temp\nseb934.tmp\userinfo.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsfbba5.tmp\helper.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsfbba5.tmp\license.txt | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsfbba5.tmp\modern-header.bmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsfbba5.tmp\nsdialogs.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsfbba5.tmp\system.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsfbba5.tmp\uac.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\apphelp.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\license.txt | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\modern-header.bmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\nsdialogs.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\registry.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\soffer.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\system.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\uac.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\uninstall.exe | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsi4416.tmp\userinfo.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\chappconfirm.exe | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\extassist.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\modern-header.bmp | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\registry.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\soffer.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\system.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\uac.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsia8a0.tmp\userinfo.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nspe13b.tmp | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete |
| c:\users\user\appdata\local\temp\nsue15b.tmp\helper.dll | Generic Read,Write Data,Write Attributes,Write extended,Append data,Delete,LEFT 262144 |
| c:\users\user\appdata\local\temp\nsue15b.tmp\helper.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsue15b.tmp\helper.dll | Generic Write,Read Attributes,Delete,LEFT 262144 |
| c:\users\user\appdata\local\temp\nsue15b.tmp\helper.dll | Generic Write,Read Attributes,LEFT 262144 |
| c:\users\user\appdata\local\temp\nsue15b.tmp\helper.dll | Generic Write,Read Data,Read Attributes,Delete,LEFT 262144 |
| c:\users\user\appdata\local\temp\nsue15b.tmp\helper.dll | Generic Write,Read Data,Read Attributes,LEFT 262144 |
| c:\users\user\appdata\local\temp\nsue15b.tmp\registry.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsue15b.tmp\starter.exe | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsue15b.tmp\system.dll | Generic Write,Read Attributes |
| c:\users\user\appdata\local\temp\nsue15b.tmp\userinfo.dll | Generic Write,Read Attributes |
Registry Modifications
Registry Modifications
This section lists registry keys and values that were created, modified and/or deleted by samples in this family. Windows Registry activity can provide valuable insight into malware functionality. Additionally, malware often creates registry values to allow itself to automatically start and indefinitely persist after an initial infection has compromised the system.| Key::Value | Data | API Name |
|---|---|---|
| HKLM\software\classes\applications\429365e94470c116c59113961fabfcc08990bb97_0001320680::ishostapp | RegNtPreCreateKey |
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| User Data Access |
|
| Encryption Used |
|
| Anti Debug |
|
| Other Suspicious |
|


