Backdoor.Sinowal
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 60 % (Medium) |
| Infected Computers: | 11 |
| First Seen: | February 6, 2014 |
| Last Seen: | August 7, 2019 |
| OS(es) Affected: | Windows |
The detection of Backdoor.Sinowal on your system indicates a potential security threat that requires immediate attention. This backdoor threat can compromise your system's security and put your personal data at risk. It is essential to understand the nature of this threat and take prompt action to remove it and prevent future infections.
Table of Contents
What Is Backdoor.Sinowal?
Backdoor.Sinowal is a type of malware that allows unauthorized access to your system, enabling hackers to steal sensitive information, install additional malware, or use your system for malicious activities. Backdoors like Backdoor.Sinowal can be particularly dangerous as they can remain hidden on your system for an extended period, causing damage without being detected.
How Backdoor.Sinowal Operates
Backdoor.Sinowal, like other backdoor threats, operates by creating a secret channel of communication between your system and a command and control server controlled by the attacker. This channel allows the attacker to send commands to your system, steal data, or install additional malware. The malware may use various techniques to evade detection, such as disguising itself as a legitimate program or using encryption to hide its communication.
- It can exploit vulnerabilities in your system or applications to gain access.
- It may use social engineering tactics to trick you into installing the malware.
- Once installed, it can communicate with the command and control server to receive instructions.
Symptoms of Infection
Identifying a backdoor infection can be challenging, as these threats are designed to remain hidden. However, some common symptoms may indicate the presence of Backdoor.Sinowal or similar malware:
- Unexplained changes to your system settings or files.
- Increased network activity or unusual data transfers.
- Slow system performance or frequent crashes.
- Appearance of unfamiliar programs or icons.
How to Remove Backdoor.Sinowal
Removing Backdoor.Sinowal requires a systematic approach to ensure all components of the malware are eliminated. Follow these steps:
- Boot your system in Safe Mode with Networking to limit the malware's ability to interfere with the removal process.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system. This will help identify and remove all infected files and components.
- Uninstall any suspicious programs or applications that were installed around the time of the infection.
- Reset your web browsers (Chrome, Firefox, Edge) to their default settings to remove any malicious extensions or settings.
- Reboot your system and perform another scan with your anti-malware tool to ensure all threats have been removed.
Conclusion
The removal of Backdoor.Sinowal is crucial to securing your system and protecting your personal data. By understanding how backdoor threats operate and following the removal steps outlined above, you can effectively eliminate this malware and prevent future infections. Remember, maintaining up-to-date antivirus software, being cautious with email attachments and downloads, and regularly scanning your system for threats are key practices in keeping your digital environment secure.
SpyHunter Detects & Remove Backdoor.Sinowal
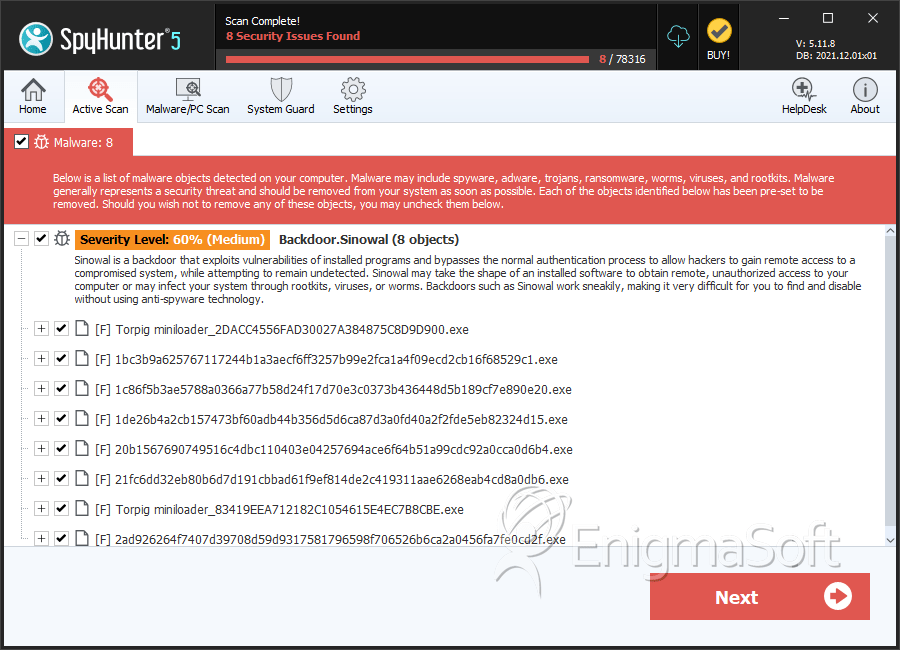
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | Torpig miniloader_2DACC4556FAD30027A384875C8D9D900.exe | 2dacc4556fad30027a384875c8d9d900 | 2 |
| 2. | Torpig miniloader_83419EEA712182C1054615E4EC7B8CBE.exe | 83419eea712182c1054615e4ec7b8cbe | 1 |
| 3. | Torpig miniloader_87851480DEB151D3A0AA9A425FD74E61.exe | 87851480deb151d3a0aa9a425fd74e61 | 1 |
| 4. | Torpig miniloader_809910F29AA63913EFA76D00FA8C7C0B.exe | 809910f29aa63913efa76d00fa8c7c0b | 1 |
| 5. | Torpig miniloader_0F82964CF39056402EE2DE9193635B34.exe | 0f82964cf39056402ee2de9193635b34 | 1 |
| 6. | Torpig miniloader_011C1CA6030EE091CE7C20CD3AAECFA0.exe | 011c1ca6030ee091ce7c20cd3aaecfa0 | 1 |
| 7. | Torpig miniloader_C3366B6006ACC1F8DF875EAA114796F0.exe | c3366b6006acc1f8df875eaa114796f0 | 1 |
| 8. | Torpig miniloader_4A3543E6771BC78D32AE46820AED1391.exe | 4a3543e6771bc78d32ae46820aed1391 | 1 |
| 9. | 1bc3b9a625767117244b1a3aecf6ff3257b99e2fca1a4f09ecd2cb16f68529c1.exe | a16c9f80d4a22232fa9fb6e27f95646e | 0 |
| 10. | 1c86f5b3ae5788a0366a77b58d24f17d70e3c0373b436448d5b189cf7e890e20.exe | 0b9b058f0c05498ed0df34400095d384 | 0 |
| 11. | 1de26b4a2cb157473bf60adb44b356d5d6ca87d3a0fd40a2f2fde5eb82324d15.exe | 42bc3559d72be6bbcf2d3a098943c150 | 0 |
| 12. | 20b1567690749516c4dbc110403e04257694ace6f64b51a99cdc92a0cca0d6b4.exe | 18e7b65e65b9c45df2d1fe93d4d61da6 | 0 |
| 13. | 21fc6dd32eb80b6d7d191cbbad61f9ef814de2c419311aae6268eab4cd8a0db6.exe | 8e3136c7f7d3f1b95e635997788fbabb | 0 |
| 14. | 2ad926264f7407d39708d59d9317581796598f706526b6ca2a0456fa7fe0cd2f.exe | a564c081a0193e396c54b2d92cb9339b | 0 |
| 15. | 313f6264a0b604ff5d05777f7383359f422c8a3df4b3fd51290b0626bcc1e681.exe | fa7ac63cf83a890b8c7e8c8792322b50 | 0 |
| 16. | 3f26f5ba635a070597cbe90ad2967431eceac530fecf0dc1bd13ba6a456feccd.exe | 4f7e9d298faab7010e9665caac561e91 | 0 |
| 17. | 412e2e11b9782a27da0fa66229d0aacb71bc15128e993e77ca7cb5102a4127db.exe | cb03cdf8a88e95080b31e3658ae81d51 | 0 |
| 18. | 4b6bf95a7533ca5976e522e1456d54f4d9f1d207f25d3d840ef264773dbedb3b.exe | daa95d7c1c0849ddd5aa1e6d3042dd16 | 0 |
| 19. | 68ac02330b5db84a585dbb9cf262a5e08b6a4677b540bb99159517a6a2bce0eb.exe | 9915f89bb254dc07c714aa9c49d2fbd2 | 0 |
| 20. | 6e50eb82f0511006c411866ad911340430b8acd8c6fa39552719ff72c13280b7.exe | f19b78f18399e6fded974f353a36ea96 | 0 |
| 21. | 7eaf3197bb4faa3a020f6e6435cd7609898fc4663eb75e9ddf047570d0552690.exe | 80ddf0a7f5b1180efee6c4329f06ad08 | 0 |
| 22. | 82bdaaa8e5ee3dcea5daef5b61b8398ce0dd20a756562746eb7a35b243d53c56.exe | 3c468693b3c0d9ef2d1c14171536106d | 0 |
| 23. | 9329afb4e8cc940c8c1f0a8bf168e7fc75316747171a5e0cb41043df20113933.exe | f8ef18458eb0ea591a7afaa50f167244 | 0 |
| 24. | a9f9c874d68eec4ffefb2dbc83f5a5edde97a4e894064c5da922015e791c573c.exe | bc9d7f7a32d71186634ba2c24866e5fd | 0 |
| 25. | b58be916b455d1fda3bf7ce51cdf1b8f6ab83edaf643550025bfc46b37d52b71.exe | 778bc5698dc348016b52b90d1fa888a8 | 0 |
| 26. | b70b9f9f78bd82307955eb33aaf70d66640a44b3c7b3f591bf8be019ad231d3c.exe | ad9eb5b870a68dea079437268fcba7d7 | 0 |
| 27. | c852402b1bc82842a7037bac7c2d0f37ebb084e0f6ba31ee5294a3ca6c55004f.exe | d5e6148d691a3277750d9c78f3b0ab71 | 0 |
| 28. | c9d44c35dc86668349805b01539ab037aa8a16910920c2bde77aac6e99f4c5ab.exe | 3a69991e3010bdce7b342f1dbefe0bfd | 0 |
| 29. | df350e17b9bc026ef5b4fcf8bbb1eb3debc1fb872d6064f76c48c6a5d57efde4.exe | 3224b24814471bdf2abf53d3a13912ed | 0 |


