Backdoor.Bladabindi.B
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Popularity Rank: | 3,993 |
| Threat Level: | 80 % (High) |
| Infected Computers: | 5,151 |
| First Seen: | February 22, 2013 |
| Last Seen: | October 2, 2026 |
| OS(es) Affected: | Windows |
The detection of Backdoor.Bladabindi.B on your system indicates a potential security threat that requires immediate attention. This backdoor threat can compromise the integrity of your computer, allowing unauthorized access and potentially leading to further malware infections, data theft, or other malicious activities. It is essential to understand the nature of this threat and take prompt action to remove it and prevent future occurrences.
Table of Contents
What Is Backdoor.Bladabindi.B?
Backdoor.Bladabindi.B is a type of malware that operates as a backdoor, which means it can open a secret portal on your computer, allowing hackers to remotely access and control your system. This can lead to a range of malicious activities, including data theft, installation of additional malware, or use of your computer for malicious purposes. The name Backdoor.Bladabindi.B itself does not specify a known malware family, but rather indicates the type of threat it poses.
How Backdoor.Bladabindi.B Operates
Backdoor.Bladabindi.B, like other backdoor threats, is designed to bypass security measures and remain undetected on your system. Once installed, it can communicate with its command and control servers to receive instructions, which may include downloading and installing additional malware, stealing sensitive information, or using your computer's resources for malicious activities. The exact mechanisms of operation can vary, but the primary goal is to provide unauthorized access to your computer.
Symptoms of Infection
Symptoms of a Backdoor.Bladabindi.B infection can be subtle and may not always be immediately apparent. However, signs of infection may include unusual network activity, slow system performance, unexpected changes to system settings, or the presence of unfamiliar programs. Since backdoors are designed to be stealthy, it's possible that your system may not exhibit any noticeable symptoms, making regular security scans crucial for detection.
How to Remove Backdoor.Bladabindi.B
- Boot your computer in Safe Mode with Networking to prevent the malware from loading and to allow for internet access for updates and scans.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system. Ensure the tool is updated with the latest definitions to enhance detection and removal capabilities.
- Uninstall any suspicious programs that were installed around the time of the infection. Be cautious and only remove programs you are certain are malicious or unnecessary.
- Reset your web browsers (Google Chrome, Mozilla Firefox, Microsoft Edge) to their default settings to remove any malicious extensions or settings that the backdoor might have altered.
- After completing the above steps, reboot your computer and perform another full scan with your anti-malware tool to ensure that all components of the backdoor have been removed.
Conclusion
Removing Backdoor.Bladabindi.B requires careful and immediate action to prevent further damage to your system and protect your sensitive information. By following the removal steps outlined and maintaining good security practices, such as regularly updating your operating system and security software, using strong antivirus programs, and being cautious with emails and downloads, you can significantly reduce the risk of future infections. Remember, vigilance and proactive security measures are key to protecting your digital assets in today's evolving cybersecurity landscape.
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| Panda | Trj/CI.A |
| Fortinet | MSIL/Injector.PE!tr |
| AntiVir | TR/Dropper.Gen |
| F-Secure | Gen:Variant.Barys.2254 |
| Comodo | TrojWare.Win32.Agent.ECA |
| Sophos | Mal/Generic-S |
| Kaspersky | Trojan.Win32.Jorik.Agent.cor |
| Symantec | WS.Reputation.1 |
| K7AntiVirus | Trojan |
| McAfee | Artemis!2BEE3790F42F |
| CAT-QuickHeal | Trojan.Agent.cor |
| Panda | Generic Trojan |
| AVG | MSIL.AP |
| Fortinet | MSIL/Agent.PPP!tr |
| Microsoft | Trojan:MSIL/Bladabindi.F |
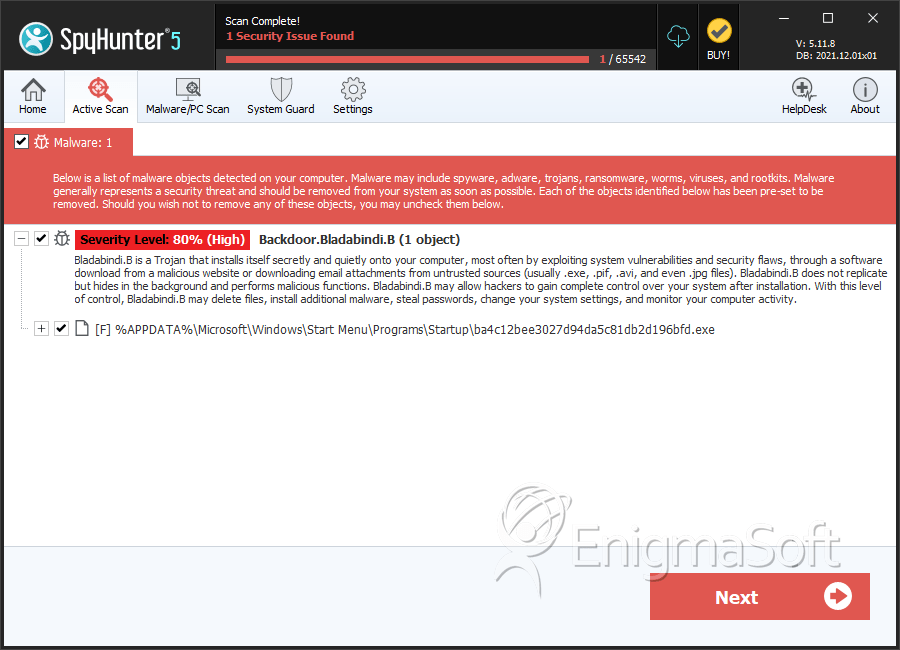
SpyHunter Detects & Remove Backdoor.Bladabindi.B
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | ba4c12bee3027d94da5c81db2d196bfd.exe | 2bee3790f42fb4dd98ecaab6975c7c4c | 2 |
Analysis Report
General information
| Family Name: | Backdoor.Bladabindi.B |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
a09b6c1c73183f67f137f87e8e6e0a63
SHA1:
62a0de4c2e29c2f44b6b4f075047f2731a6b9637
SHA256:
82D927612A1D81B5ADE78ECDB37DDFE86B6A4B80A972D35568DEC8C9A5632358
File Size:
17.92 KB, 17920 bytes
|
|
MD5:
ee79e4dc36e481a944dbfa1f4b116487
SHA1:
9ef26a68fb429aca27d958ed16ca54f67f71fef7
SHA256:
8B74EEA68C6D830BB833302DA8FA4487688804870ACA546FF8B72BD681EC2033
File Size:
581.63 KB, 581632 bytes
|
|
MD5:
f17e7f06fa78fc8c898c83f4b0d50296
SHA1:
cc7cdb320cffda144fbae4473844e4b75beb3d53
SHA256:
1D5291F72BE45C3B23A8F4FF83E6EC77EB1115A281FA4541F02014EE6035BA7E
File Size:
851.97 KB, 851968 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File has been packed
- File has exports table
- File has TLS information
- File is 32-bit executable
- File is either console or GUI application
Show More
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.


Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| Comments | http://www.netbull.com |
| Company Name | NetBull |
| File Description | NetBull |
| File Version | 3.1.0.8 |
| Internal Name | NetBull |
| Legal Copyright | Copyright © 1999-2023 NetBull.com |
| Legal Trademarks | NetBull |
| Original Filename | NetBull.exe |
| Product Name | NetBull |
| Product Version | 3.1.0.8 |
File Traits
- big overlay
- dll
- No Version Info
- packed
- x86
Block Information
Block Information
During analysis, EnigmaSoft breaks file samples into logical blocks for classification and comparison with other samples. Blocks can be used to generate malware detection rules and to group file samples into families based on shared source code, functionality and other distinguishing attributes and characteristics. This section lists a summary of this block data, as well as its classification by EnigmaSoft. A visual representation of the block data is also displayed, where available.| Total Blocks: | 609 |
|---|---|
| Potentially Malicious Blocks: | 27 |
| Whitelisted Blocks: | 581 |
| Unknown Blocks: | 1 |
Visual Map
? - Unknown Block
x - Potentially Malicious Block
Similar Families
Similar Families
This section lists other families that share similarities with this family, based on EnigmaSoft’s analysis. Many malware families are created from the same malware toolkits and use the same packing and encryption techniques but uniquely extend functionality. Similar families may also share source code, attributes, icons, subcomponents, compromised and/or invalid digital signatures, and network characteristics. Researchers leverage these similarities to rapidly and effectively triage file samples and extend malware detection rules.- BadJoke.XA
- Banker.YA
- Injector.FHBC
- Injector.KDF
- Injector.KZP
Show More
- Injector.XN
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Anti Debug |
|
| User Data Access |
|
| Syscall Use |
Show More
|
| Process Manipulation Evasion |
|
| Process Shell Execute |
|
Shell Command Execution
Shell Command Execution
This section lists Windows shell commands that are run by the samples in this family. Windows Shell commands are often leveraged by malware for nefarious purposes and can be used to elevate security privileges, download and launch other malware, exploit vulnerabilities, collect and exfiltrate data, and hide malicious activity.
C:\WINDOWS\SysWOW64\rundll32.exe C:\WINDOWS\system32\rundll32.exe c:\users\user\downloads\9ef26a68fb429aca27d958ed16ca54f67f71fef7_0000581632.,LiQMAxHB
|